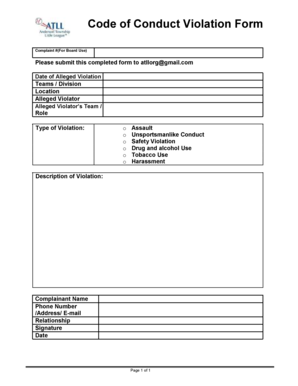
Code Of Conduct Violation Form
Use a Code Of Conduct Violation Form template to make your document workflow more streamlined.
What this violation form records
A Code Of Conduct Violation Form records an alleged breach of an organization’s conduct policy and the resulting review. It identifies the person involved, describes the reported behavior, captures dates, witnesses, supporting documents, policy references, reviewer findings, and corrective action. The form can also document notice and acknowledgment by the employee or manager. In signNow, upload the form, review auto-detected fillable fields, add recipients and signature fields, send it for completion, and retain the signed PDF with its audit trail. Internal policy and applicable state employment law determine the required content.
Who uses this violation form
Human resources
Human resources teams document an alleged conduct breach, identify the policy involved, record the response, and route acknowledgments or signatures through a controlled workflow.
Compliance teams
Compliance officers and managers preserve the reported facts, supporting attachments, reviewer decisions, and employee acknowledgment in one auditable record.
Features for conduct investigations
signNow connects the form’s narrative, acknowledgment, routing, signature, and record-preservation requirements in one documented workflow.
Field detection
Auto-detected fields help identify existing names, dates, narratives, and signature areas before the violation form is routed for review.
Role routing
Role-based routing sends the report to the employee, manager, witness, or reviewer in the intended sequence.
Audit trail
Audit trails record signer activity, timestamps, and document history for later internal review.
Electronic signing
Typed or drawn signatures document acknowledgment without requiring paper exchange between authorized participants.
Mobile access
Mobile apps let authorized users review and sign the violation form from iOS or Android devices.
Reusable templates
Templates keep approved conduct-policy language and required acknowledgment fields consistent across investigations.
Recommended violation-form setup
Configure the form around confidential employee information, documented consent, controlled access, and an exportable record of every signing event.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Capture timestamps, IP, and signer actions |
| Document retention | Follow policy and applicable record rules |
| Encryption | TLS 1.2/1.3 and AES-256 protection |
How the violation form works
The signNow workflow keeps preparation, review, acknowledgment, and record preservation in a defined sequence.
Upload form: Upload the blank violation form. Check fields: Review detected fields and add missing inputs. Assign roles: Assign employee, manager, and reviewer roles. Complete record: Send, sign, and preserve the completed record.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Complete the form in signNow
Follow these steps to prepare, route, sign, and preserve the Code Of Conduct Violation Form.
Upload form:
Upload the completed form template. Check fields:
Confirm detected fields and add signatures. Assign recipients:
Assign each reviewer and signer. Send form:
Send the form through signNow. Store record:
Download the signed PDF and audit trail.
What the audit trail records
A signNow audit trail provides a technical record of how the Code Of Conduct Violation Form moved from preparation through completion.
Authenticate signer:
Capture timestamp:
Hash document:
Seal record:
Export evidence:
Archive securely:
Security for signed violation records
Signer authentication:
Second factor:
Audit evidence:
Transport encryption:
Stored encryption:
Security certifications:
Platform requirements for signing
The Code Of Conduct Violation Form can be prepared in a browser using Chrome, Firefox, Safari, or Edge on Windows or macOS. Signers can also review and complete assigned fields through signNow mobile apps on iOS or Android.
Browsers Chrome, Firefox, Safari, Edge Operating systems Windows, macOS, iOS, Android Mobile signing signNow mobile apps available
Organizations handling confidential conduct investigations should use managed devices, role-based access, and approved storage locations. Enterprise deployments may connect signNow with identity provisioning, API workflows, or systems such as Microsoft 365 and Google Workspace while preserving the completed PDF and audit trail.
Privacy and disclosure pitfalls
Including medical details, protected characteristics, or personal contact information in the violation form can disclose more employee data than the investigation requires. Sending the completed form to an incorrect recipient can expose allegations, witness statements, or disciplinary information outside the authorized review group. Failing to capture electronic consent before signing may weaken evidence that the employee agreed to receive and sign the record electronically. Broad folder permissions can let unrelated staff view a conduct investigation, undermining confidentiality and increasing unauthorized-disclosure risk.
Risks of improper documentation
Incomplete incident record
Acknowledgment dispute
Privacy exposure
Weak evidence trail
Legal standing and evidentiary value
A signed Code Of Conduct Violation Form may support a U.S. business record when intent, signer attribution, electronic consent, and reliable retention are shown under ESIGN, 15 U.S.C. ch. 96, and applicable state law, including UETA or New York ESRA. Wills, court orders, family law decrees, and other statutory exclusions require separate legal handling.

Pricing and features for this form
Compare verified signNow plan details with competitor information that remains unavailable in the supplied vendor data.
| Features | signNow | DocuSign | Adobe Sign | PandaDoc | Dropbox Sign |
|---|---|---|---|---|---|
| Annual Business plan price | $8/user/month billed annually | Not verified | Not verified | Not verified | Not verified |
| Free trial availability | 7-day trial, no card required | Not verified | Not verified | Not verified | Not verified |
| Bulk send availability | Business Premium plan | Not verified | Not verified | Not verified | Not verified |
| Audit trail availability | Included in Business plan | Not verified | Not verified | Not verified | Not verified |
| HIPAA compliance availability | Available with BAA | Not verified | Not verified | Not verified | Not verified |
Troubleshooting this violation form
These answers address field preparation, confidential records, electronic consent, signer access, and audit evidence for a Code Of Conduct Violation Form.
Upload the original Code Of Conduct Violation Form as a PDF or supported document, then inspect signNow’s detected fields. Add missing signature, date, acknowledgment, or narrative fields manually before sending the record for review.
Use signNow’s role assignment to distinguish the reporting manager, employee, reviewer, and witness. Place each signature or acknowledgment field beside the correct party’s information, then confirm routing order before sending.
The signNow Business plan includes legally binding eSignatures and audit trails. For employee records containing protected health information, use a HIPAA-compliant configuration with a required business associate agreement before processing PHI.
For consumer-facing electronic records, ESIGN requires disclosure of the right to paper, access to the electronic format, and a process to withdraw consent under 15 U.S.C. §7001(c). Employee workflows may require separate policy review.
If a signer cannot open the invitation, verify the recipient address, resend the signNow invite, or generate a controlled signing link. Avoid forwarding confidential allegations through an unrestricted link or personal email account.
Export the completed signNow audit trail with the signed PDF. The record should preserve signer identity events, timestamps, IP information, action history, and the certificate of completion for later internal review.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.