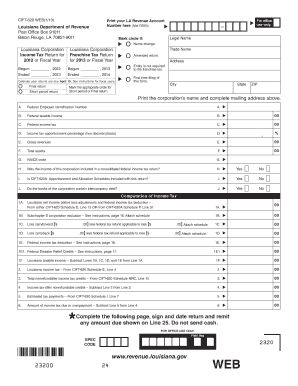
Cift 620 Form
Use a Cift 620 template to make your document workflow more streamlined.
What Cift 620 Form does
Cift 620 Form is a document template that can be completed, signed, and retained through a controlled electronic workflow. Because the name alone does not identify an issuing agency, filing deadline, or legally defined purpose, confirm the source instructions before entering data. With signNow, upload the PDF, review detected fields, assign signers, and send it for completion. The resulting PDF can be paired with an Audit Trail recording signer actions, timestamps, and document history. ESIGN and applicable state electronic-transaction law may support electronic execution when consent, intent, attribution, and record access requirements are satisfied.
How Cift 620 Form works
The signNow workflow moves Cift 620 Form from an uploaded PDF to a signed, auditable record.
Upload: Upload the source PDF. Check fields: Review detected fields and correct placement. Send: Add signers and send securely. Archive: Capture signatures and retain the completed record.
Mobile options for Cift 620 Form
Use the signNow mobile apps on iOS and Android to review Cift 620 Form, capture a document with the camera, and complete signing workflows. Confirm current app support before deployment because operating-system compatibility can change.
iPhone iOS 16 or later Android Android 11 or later Mobile tools Camera capture and offline signing
Offline signing can help when a signer works without continuous connectivity, while camera-based capture can convert a paper Cift 620 Form into a digital workflow. For regulated records, synchronize the completed document and Audit Trail, then apply your organization’s retention and access controls.
Recommended Cift 620 Form setup
Configure signer identity, audit evidence, retention, encryption, and access controls before sending Cift 620 Form.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS verification |
| Audit trail | Export after completion |
| Document retention | Apply the underlying legal schedule |
| Encryption | AES-256 at rest and TLS in transit |
| User provisioning | Role-based access with administrator control |
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Audit trail for Cift 620 Form
A signNow Audit Trail connects Cift 620 Form to signer actions and completion evidence for later review.
Authenticate signer:
Timestamp actions:
Hash document:
Seal record:
Log activity:
Export evidence:
Protect Cift 620 Form records
Use a documented retention process that preserves the completed form, audit evidence, and access history together.
Apply the correct retention rule
Export every audit trail
Secure the final signed copy
Index signed records accurately
Cift 620 Form retention schedule
Choose the retention period from the record’s legal purpose, not from the form name alone.
Three years from filing
Six years for major understatement
Three years after hire
Six years for HIPAA records
Longer period under state law
Documents needing extra review
Notarization
Wills
Family law
Real-estate deeds
Privacy pitfalls to address
Personal identifiers entered into Cift 620 Form may appear in emails, downloads, and shared folders without appropriate access restrictions. A signer may complete Cift 620 Form without a documented consumer consent disclosure when ESIGN §7001(c) applies. Delegated sending can expose the completed form to an unauthorized recipient if role permissions and signer addresses are not reviewed. Keeping only the signed PDF and omitting the Audit Trail weakens evidence of identity, intent, timestamps, and document history.
Security for Cift 620 Form
Signer authentication:
Audit evidence:
Stored data:
Transport security:
Independent assurance:
U.S. eSignature:



Cift 620 Form troubleshooting
Resolve signing, field, authentication, and recordkeeping questions before distributing a completed Cift 620 Form.
Upload the original Cift 620 Form PDF and inspect the detected fields before sending. signNow’s editor lets you add or correct text, date, checkbox, and signature fields when automatic detection misses a required location.
The signNow Business plan includes legally binding eSignatures, templates, and Audit Trails at $8 per user monthly when billed annually. If the workflow needs bulk sending, Business Premium adds that capability at $15 per user monthly.
A completed Cift 620 Form can be supported by signNow’s Audit Trail, timestamps, document history, and signer actions. For U.S. transactions, admissibility still depends on intent, consent, attribution, and record retention under ESIGN and applicable UETA law.
For consumer-facing transactions, provide the electronic-record disclosure and confirm the signer can access the format. ESIGN, 15 U.S.C. §7001(c), also requires a process for withdrawing consent before relying on electronic delivery.
Use signNow’s SMS authentication or other available signer controls when identity evidence matters. Advanced signer authentication is listed with Enterprise, while regulated workflows may require a separate assessment of HIPAA or 21 CFR Part 11 obligations.
After completion, download the signed PDF and Audit Trail from signNow and store both together. A Business subscription includes Audit Trails, while long-term legal retention remains the organization’s responsibility under the applicable recordkeeping rule.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.