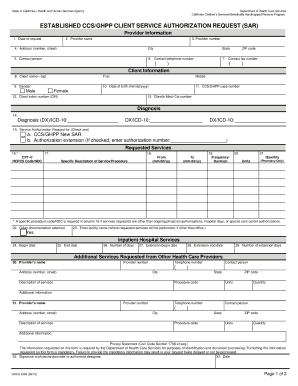
Established Ccsghpp Client Service Authorization Request Sar Dhcs Ca Form
Use a ESTABLISHED CCSGHPP CLIENT SERVICE AUTHORIZATION REQUEST SAR Dhcs Ca template to make your document workflow more streamlined.
What this authorization request form does
This form is a California Department of Health Care Services authorization request used to document a client service authorization request. It identifies the requested service, client information, provider details, authorization period, and supporting justification so the reviewing organization can evaluate the request. Users complete the applicable fields, check the entries for accuracy, and obtain required signatures before submission through the designated DHCS or program workflow. signNow can convert the source PDF into a fillable workflow, route it to authorized signers, and preserve the completed record with an audit trail.
Who uses this DHCS request
Healthcare providers
California healthcare providers and authorized service teams use the request to collect client, provider, service, authorization-period, and signature information for DHCS-related processing.
Authorization teams
Administrative staff and authorized reviewers use the completed request to route individualized service authorization documentation while controlling access to client information and completion evidence.
How this request moves through signNow
The signNow workflow keeps the source DHCS request intact while adding fields, recipients, signatures, and completion evidence.
Upload: Upload the DHCS request PDF. Prepare: Review detected and missing fields. Route: Assign recipients and signing order. Complete: Collect signatures and archive evidence.
Complete this DHCS request in signNow
Use the source request as the controlling document, then verify every client, service, provider, and authorization field before routing it.
Upload form:
Upload the completed DHCS request PDF. Check fields:
Review detected fields and add missing client, provider, service, and signature fields. Assign signers:
Assign each field to the authorized DHCS participant or provider signer. Send request:
Send the request through the approved recipient workflow and monitor completion. Store record:
Download the signed request and audit trail for authorized records storage.
Features for the DHCS authorization request
signNow organizes the California DHCS request from PDF preparation through assigned signatures, completion evidence, and controlled record storage.
PDF preparation
Upload the DHCS authorization request PDF and use signNow’s field detection to identify existing fillable areas before adding missing fields.
Recipient routing
Route client service authorization information to assigned recipients in a defined signing order, reducing manual forwarding and recipient confusion.
Audit evidence
Capture signer actions, timestamps, delivery events, and completion evidence with the request’s audit trail for later review.
Mobile access
Use mobile apps when authorized staff need to review or sign the request away from a desktop workstation.
Record control
Store the signed request and completion record in a controlled workflow connected to the organization’s record-management process.
Signer security
Use two-factor authentication or stronger signer controls when the request contains sensitive client or health information.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Privacy and disclosure controls
Client identifiers and service details can appear in the completed PDF; limit access to authorized DHCS personnel and providers. Missing authorization language or signer consent can create uncertainty about whether the client approved the requested disclosure or service. Sending the request to the wrong recipient can expose protected health information and complicate incident response. Uncontrolled copies in email or personal storage can weaken retention, access, and audit-trail controls.
Platform requirements for this form
Prepare and review the Established Ccsghpp Client Service Authorization Request Sar Dhcs Ca Form in Chrome, Firefox, Safari, or Edge on Windows or macOS. signNow also provides iOS and Android apps for authorized mobile review and signing. Data protection includes TLS 1.2/1.3 in transit and AES-256 at rest.
Web browsers Chrome, Firefox, Safari, Edge Mobile apps iOS and Android apps Data protection TLS 1.2/1.3 and AES-256
Organizations handling California client-service information should use managed Windows, macOS, iOS, or Android devices, controlled user provisioning, and restricted downloads. Connect approved storage or case-management systems through available integrations such as Google Drive, Box, Egnyte, or Microsoft 365, while applying the organization’s HIPAA, DHCS, and state-law controls.
Authentication and signing safeguards
PKI and X.509 certificates:
Two-factor authentication:
SMS one-time codes:
Optional ID verification:
Timestamped signing history:
Role-based document access:
Recommended DHCS request setup
Use controlled authentication, signing, audit, retention, and encryption choices for California client-service authorization records.
| Setting | Recommendation |
|---|---|
| Authentication method | Email plus SMS OTP |
| Signature type | Legally binding electronic signature |
| Audit trail | Enabled with completion certificate |
| Document retention | Six years for HIPAA records |
| Encryption | TLS 1.2/1.3 and AES-256 |
What the audit trail records
The audit trail documents the signing events that support review of this individualized California DHCS authorization request.
Authenticate signer:
Record timestamp:
Link document:
Seal record:
Inspect history:
Export evidence:
Retain and audit the completed request
Preserve the signed DHCS request with its audit evidence, access controls, and the retention rule applicable to the underlying record.
Apply the governing retention rule
Export the completion evidence
Limit access to authorized staff
Track request versions
Rollout and retention for this request
Use a controlled rollout for the DHCS request, then preserve signed records according to the applicable program and privacy requirements.
Prepare request:
First send:
Team onboarding:
Seven-day trial:
Complete signatures:
Export evidence:
Six-year HIPAA rule:
Secure archive:
State rules and document exclusions
Check state rules
No electronic execution
Paper process applies
Recording may be rejected
Legal standing of the authorization request
A completed electronic DHCS authorization request can support a U.S. business record when the signer demonstrates intent, consents to electronic records, can be identified, and the record remains reproducible. ESIGN, 15 U.S.C. chapter 96, and applicable state law support electronic records, but wills, certain court filings, and specified family-law documents remain excluded.

Troubleshoot this DHCS request workflow
Resolve field, signer, consent, plan, privacy, and correction issues before treating a completed authorization request as final.
Upload the original PDF again and inspect the detected fields before sending. signNow’s Business plan includes templates and audit trails, but field detection does not replace a manual check of every DHCS-specific client, provider, service, and authorization field.
Confirm that each field is assigned to the correct recipient and that the signing order matches the organization’s authorization process. Business Premium adds bulk send, but bulk routing should not be used when each request contains individualized client information.
For a client-facing electronic record, provide the ESIGN consumer disclosure and confirm the signer can access the electronic format. ESIGN requires intent, consent, attribution, and reliable record retention; signNow’s audit trail helps document the transaction but does not replace the disclosure.
Business is listed at $8 per user per month with annual billing and includes legally binding eSignatures and audit trails. The published plan information also states that subscription plans include 100 signature invites per user per year; review current overage terms before high-volume use.
A HIPAA workflow requires a business associate agreement with signNow. HIPAA documentation must be retained for six years from creation or the last effective date under 45 CFR 164.530(j), while the organization must also apply any longer program-specific rule.
Export the signed PDF and audit trail, then compare the completed fields with the source request. If a substantive correction is needed, create a controlled replacement rather than silently editing the completed record.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.