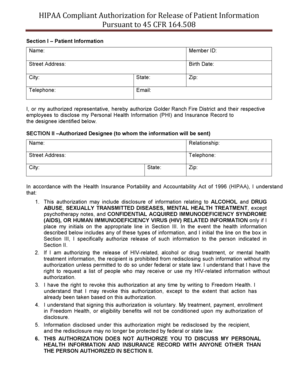
HIPAA Compliant Authorization For Release Of Patient Information
Use a HIPAA Compliant Authorization For Release Of Patient Information template to make your document workflow more streamlined.
What this HIPAA authorization does
A HIPAA Compliant Authorization For Release Of Patient Information is a patient’s written permission for a covered entity or business associate to disclose specified protected health information to identified recipients. It should state the information covered, purpose, recipient, expiration, and required signatures. In signNow, the organization uploads or prepares the authorization, places fields, sends it to the patient or representative, and retains the completed document with an audit trail. HIPAA requires related documentation for six years from creation or the last effective date under 45 CFR §164.530(j).
Who benefits from this authorization workflow
The form serves organizations that need documented patient permission before sharing protected health information with specifically identified recipients.
Solo behavioral-health practices can collect patient authorization for releasing records to named providers, attorneys, or family members without coordinating repeated office visits. Regional hospitals and outpatient clinics can route HIPAA authorizations to patients, representatives, and records staff while preserving completion evidence for disclosure review. Enterprise health systems can standardize authorization templates across departments, apply administrative controls, and connect completed releases with established records-management workflows.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Who uses this patient release form
Healthcare practices
Solo practitioners and behavioral-health clinics use the authorization to document patient permission before releasing records to named providers, attorneys, or family members. They can route the form remotely, capture the patient’s signature, and preserve the audit trail with the signed disclosure record.
Records departments
Hospital records departments and health-information exchanges use the authorization when a patient permits disclosure to a defined recipient. Staff can standardize fields, restrict access, and retain the completed authorization for the six-year HIPAA documentation period.
Features for patient release authorizations
signNow combines structured fields, electronic signing, authentication records, and retention evidence for HIPAA authorization workflows involving protected health information.
Audit trail
The completed authorization records the patient’s signature, signing time, and related events, giving records teams evidence of how consent was obtained.
Reusable template
Templates preserve the required recipient, purpose, information, and expiration fields so staff can prepare this authorization consistently across departments.
Remote signing
Email invitations and signing links let patients review and sign the authorization without requiring an in-person document exchange.
Mobile access
signNow mobile apps allow authorized staff and patients to complete the form from supported mobile devices when a desktop is unavailable.
HIPAA workflow
HIPAA compliance is available when the required business associate agreement is in place, supporting workflows involving protected health information.
Record retention
Completed documents and event histories can be retained together, helping organizations meet the six-year HIPAA documentation requirement.
How this authorization works online
The signNow workflow converts a completed patient-information release into a signed record with traceable completion events.
Prepare form: Upload the authorization and confirm its patient, recipient, purpose, and expiration fields. Assign signer: Add the patient or representative as the required signer. Review and sign: The signer reviews the release scope and completes the signature fields. Store record: signNow stores the completed authorization with its audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Quick steps to complete the authorization
Prepare this specific release form in signNow by checking its disclosure scope before sending it for signature.
Upload form:
Upload the patient-information authorization into signNow. Check fields:
Let signNow detect fillable fields, then verify each field. Send request:
Add the patient or representative and send the document. Archive record:
Store the signed authorization and audit trail together.
Recommended authorization workflow setup
Use documented signer identity, protected transmission, an audit trail, and a retention period aligned with HIPAA documentation requirements.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS OTP |
| Signature type | Typed or drawn eSignature |
| Audit trail | Capture IP, timestamps, and actions |
| Document retention | 6 years under 45 CFR §164.530(j) |
| Encryption | TLS 1.2/1.3 and AES-256 |
How the audit trail protects authorization records
A signNow audit trail links signer identity, document integrity, and event history so this patient-information authorization remains reviewable.
Authenticate signer:
Capture timestamp:
Hash document:
Seal record:
Record events:
Export trail:
Security for authorization records
TLS 1.2/1.3 and AES-256:
BAA required:
Report available on request:
Certified information security:
Timestamped document history:
Authentication and session controls:
Platform requirements for signing
Patients and staff can prepare or sign this authorization through Chrome, Firefox, Safari, or Edge on Windows and macOS, or through signNow apps for iOS and Android. Use an up-to-date browser with TLS support and a reliable internet connection.
Browsers Chrome, Firefox, Safari, and Edge Desktop systems Windows and macOS desktop access Mobile apps iOS and Android signNow apps
Healthcare organizations should manage devices, user access, and identity controls according to their HIPAA security policies. Enterprise deployments may also require SSO provisioning, API access, and retention configuration so completed authorizations and audit trails remain available to authorized records personnel.
Best practices for patient authorizations
Clear scope, documented consent, and controlled retention make this authorization easier to administer and review.
Specify recipients and purposes
Confirm the BAA before signing
Document informed electronic consent
Retain authorization evidence
Privacy pitfalls in patient authorizations
Listing an entire medical record without defining the permitted purpose can create an overly broad disclosure scope and complicate later patient or compliance review. Sending the completed authorization through an unsecured channel can expose protected health information beyond the named recipient or intended records department. Allowing shared accounts or uncontrolled links can weaken attribution because the audit trail may not establish which individual accessed or signed the authorization. Omitting an expiration date or event can leave staff uncertain whether the patient’s permission remains effective for a later disclosure.
Retention schedule for authorization records
Retain this authorization and related documentation according to the HIPAA rule, then check whether state law or organizational policy requires a longer period.
Six years from effective date
No tax period applies
No employment period applies
No broker-dealer period applies
Longer state period possible
Legal standing and evidence
An electronic authorization can provide admissible evidence when intent, consent, signer attribution, and reproducible records are established under ESIGN and applicable state law, including UETA or New York ESRA. ESIGN exceptions include wills, codicils, testamentary trusts, court orders, and family law decrees; those exclusions are not ordinary HIPAA authorizations.

Troubleshooting authorization workflows
Resolve the specific signing, consent, retention, and HIPAA configuration issues that can affect this patient-information authorization.
The signNow Business plan includes audit trails and templates, while HIPAA compliance requires a business associate agreement. Confirm the BAA is executed and configure access controls before sending documents containing protected health information.
The signNow Business plan supports legally binding eSignatures and audit trails. Business Premium adds bulk send, while Enterprise adds advanced signer authentication. Select the plan based on volume and authentication requirements, then validate the BAA requirement separately.
If the patient cannot open the authorization, confirm the email address, resend the invitation, or provide a controlled signing link. Do not send protected health information through an unsecured substitute channel while troubleshooting delivery.
A completed eSignature does not replace required HIPAA authorization content. Identify the recipient, purpose, information covered, expiration, and patient signature requirements before relying on the record for disclosure.
For consumer-facing electronic records, ESIGN requires disclosure of the right to receive paper records, access to the electronic format, and procedures for withdrawing consent under 15 U.S.C. §7001(c).
signNow encrypts data in transit with TLS 1.2/1.3 and at rest with AES-256, and lists HIPAA compliance with a BAA required. Review organizational policies and the completed audit trail for each release.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.