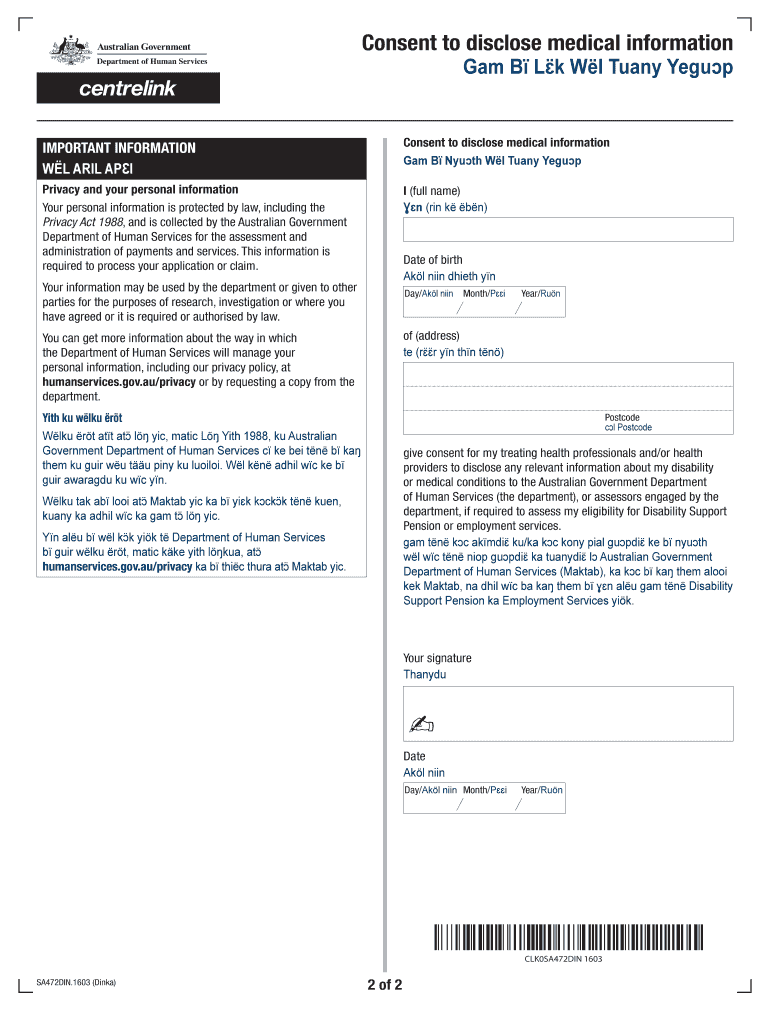
Consent To Disclose Medical Information Dinka
Use a Consent To Disclose Medical Information Dinka template to make your document workflow more streamlined.
What this medical release does
Consent To Disclose Medical Information Dinka is a written authorization for a patient or authorized representative to permit defined medical information to be shared with identified recipients. The document records the patient, recipient, purpose, information scope, authorization period, and signer’s consent so a healthcare organization can evaluate a disclosure request. With signNow, a sender uploads the release, reviews detected fields, routes it to the signer, and stores the completed document with an audit trail. HIPAA-covered organizations must also apply their own privacy policies and use a Business Associate Agreement where required.
Business types that use this consent
Consent To Disclose Medical Information Dinka supports patient authorization workflows across independent practices, regional providers, and enterprise healthcare organizations.
Solo medical practices can send a patient-specific release for signature, identify the approved recipient, and retain the completed authorization without coordinating paper handling across multiple offices. Regional healthcare groups can standardize consent templates, route disclosures to records staff, and apply controlled access when multiple clinics handle patient requests or outside-provider communications. Enterprise health systems can connect structured workflows with administrative controls, audit trails, and HIPAA-governed processes while assigning access according to departmental responsibilities and disclosure policies.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
How this medical release works
Consent To Disclose Medical Information Dinka moves from document preparation to authorized signing, controlled disclosure, and auditable storage.
Upload the form: Upload the medical release document and confirm its pages and readable fields. Check authorization details: Review names, recipients, purpose, scope, and expiration fields before sending. Send for signature: Send the consent form to the patient or authorized signer securely. Archive the record: Store the completed release with its audit trail and signed copy.
Complete and sign the medical release
Use this sequence to prepare, route, sign, and preserve Consent To Disclose Medical Information Dinka with fewer disclosure errors.
Choose the form:
Upload the correct medical release document. Check the details:
Review patient and recipient information carefully. Place signature fields:
Add required signature and date fields. Route securely:
Send only to authorized recipients. Store evidence:
Download the signed record and audit trail.
Recommended workflow configuration
A controlled configuration helps healthcare teams authenticate signers, document consent, protect medical information, and preserve evidence for Consent To Disclose Medical Information Dinka.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS OTP |
| Signature type | Electronic signature with intent |
| Audit trail | Capture timestamps and signer actions |
| Document retention | Six years for HIPAA records |
| Encryption | TLS in transit and AES-256 at rest |
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
What the audit trail records
The signNow audit trail documents technical events around the medical release, helping authorized staff review how consent was authenticated, signed, and preserved.
Authenticate signer:
Record timestamp:
Hash document:
Seal evidence:
Track activity:
Export audit trail:
Security for medical information releases
TLS encryption:
AES-256 encryption:
HIPAA compliance:
SOC 2 Type II:
ISO 27001:
ESIGN and UETA:
Platform requirements for this form
Complete Consent To Disclose Medical Information Dinka through signNow using TLS-protected browser access with Chrome, Firefox, Safari, or Edge on Windows or macOS. signNow also provides mobile apps for iOS and Android.
Browser support Chrome, Firefox, Safari, and Edge Desktop systems Windows and macOS desktop access Mobile access iOS and Android mobile apps
Healthcare organizations should manage access through approved devices and internal privacy controls. Teams requiring HIPAA workflows need a signNow Business Associate Agreement, while administrators should separately review SSO, API access, identity verification, and retention configuration for their deployment.
Best practices for medical disclosure consent
Accurate scope, verified authority, restricted access, and complete records reduce disclosure errors when using Consent To Disclose Medical Information Dinka.
Define the disclosure scope precisely
Verify the authorized signer’s identity
Limit access before disclosure
Preserve evidence and expiration
Privacy and disclosure pitfalls
A release may expose more protected health information than intended when recipients, dates, or disclosure categories are left broad. A missing patient signature, representative relationship, or authorization date can make the disclosure record difficult to validate. Sending the completed consent to an incorrect recipient can create an avoidable privacy incident and require internal investigation. Unrestricted staff access to signed releases can expose medical information beyond the team handling the authorized request.
Legal standing of this medical consent
A signed Consent To Disclose Medical Information Dinka can provide evidence of intent, signer attribution, consent to electronic records, and reliable record retention under ESIGN and applicable UETA rules. Its scope remains document-specific: wills, codicils, certain court orders, and specified family-law instruments fall within statutory exceptions and require separate legal handling.

Retention periods for related records
Retention for this medical consent depends on the organization’s role, record category, and applicable privacy policy; HIPAA-covered records have a six-year federal minimum.
Six years: HIPAA records
Three years: tax records
Later period: Form I-9
Three years: FLSA payroll
Five years: OSHA injuries
Healthcare use cases for this consent
Healthcare organizations use signed medical releases to document permission before sharing defined patient information with authorized recipients.
Fertility healthcare
Fertility Centers of Illinois needed a secure way to coordinate healthcare documents and signatures across its patient-facing operations.
- Patient-facing medical documents
- API-supported signature workflows
Fertility Centers of Illinois is a named signNow customer whose founder reported strong responsiveness and satisfaction with the API. That customer story supports the platform’s fit for healthcare document workflows, but it does not establish the legal sufficiency of every Consent To Disclose Medical Information Dinka or replace the organization’s HIPAA review.
Medical records workflow
A healthcare records team can use a controlled signNow workflow when patients authorize disclosure to another provider or named organization.
- Defined recipient and purpose
- Signed copy with audit trail
The team uploads the release, confirms detected fields, sends it to the authorized signer, and preserves the completed document with its audit trail. The organization remains responsible for validating authority, scope, recipient identity, revocation handling, and applicable HIPAA policies before disclosing information.
Troubleshooting this medical release
These answers address field detection, signer access, HIPAA controls, electronic consent, plan limits, and retention for Consent To Disclose Medical Information Dinka.
Upload the original Consent To Disclose Medical Information Dinka, then inspect signNow’s detected fields before sending. Auto-detection can assist with field placement, but staff must verify patient, recipient, scope, purpose, expiration, signature, and date fields against the source document.
signNow Business includes legally binding eSignatures and audit trails at $8/user/month when billed annually. The plan includes 100 signature invites per user per year; additional invite charges may apply, so confirm expected volume before selecting a subscription.
A HIPAA workflow requires a Business Associate Agreement with signNow. Configure access controls, limit recipients, and follow the covered entity’s policies; signNow’s HIPAA compliance statement does not replace the organization’s own HIPAA privacy and security obligations.
If a signer cannot access the email, verify the recipient address, resend the invitation, or provide a controlled signing link. For stronger assurance, use available signer authentication such as SMS OTP or identity verification when the organization’s policy requires it.
ESIGN and UETA generally recognize electronic signatures when intent, consent, attribution, and record reproducibility are established. For consumer-facing electronic records, review the ESIGN consumer-disclosure requirements in 15 U.S.C. §7001(c) before routing the release.
Export the completed document and audit trail from signNow, then store them together under the healthcare organization’s retention policy. HIPAA 45 CFR §164.530(j) requires six years for covered records from creation or the last effective date.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.