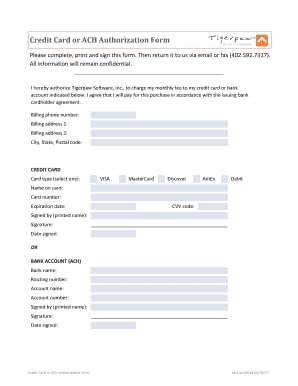
Credit Card Authorization Form
Use a Credit Card Authorization Form template to make your document workflow more streamlined.
What a credit card authorization form does
A Credit Card Authorization Form records a cardholder’s permission for a named merchant to charge an identified amount or account under stated terms. It normally captures the cardholder’s name, billing details, payment information, authorization scope, date, and signature. With signNow, a sender uploads the form, reviews detected fillable fields, sends it to the cardholder, and receives a signed PDF with an audit trail. The form documents consent; it does not itself guarantee payment approval, settle a transaction, or replace applicable card-network rules.
Who uses credit card authorization forms
Financial services
Financial-services teams use signed authorizations to document cardholder approval for invoices, recurring charges, and customer account payments while preserving the amount and transaction context.
Healthcare offices
Healthcare offices use the form when a patient or responsible party authorizes payment, with HIPAA controls and a business associate agreement where protected health information is involved.
Key features for card authorizations
A signNow workflow can turn a completed Credit Card Authorization Form into a traceable payment record without separating the signature evidence from the document.
Field placement
Place cardholder name, billing address, authorization amount, date, and signature fields directly on the uploaded form so the signer reviews the complete payment request.
Remote signing
Send the authorization by email or signing link, allowing the cardholder to review the merchant and approved amount before signing electronically.
Audit trail
Capture signer actions, timestamps, and completion evidence with the authorization so payment teams can investigate disputed transactions without relying on email chains.
Reusable templates
Use templates for recurring customer-payment workflows while preserving transaction-specific fields such as amount, invoice reference, and authorization date.
Mobile completion
Collect signatures through signNow mobile apps when staff process authorizations away from a desk, including customer-facing payment workflows that require immediate completion.
Connected records
Connect completed authorizations to supported systems such as Salesforce, NetSuite, Google Drive, Box, or Microsoft 365 for controlled record handling.
How the credit card authorization form works
A cardholder completes the payment authorization, reviews the approved amount, and signs electronically before the merchant stores the completed record.
Upload form: Upload the authorization form and identify cardholder, merchant, amount, and signature fields. Check fields: Review detected fields, add required signer roles, and confirm authorization language. Send securely: Send the form by email or signing link to the cardholder. Store record: Collect the signature and retain the completed form with its audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Steps to complete the authorization form
Prepare the cardholder authorization in signNow, collect the required signature, and preserve the finished record for payment administration.
Upload form:
Upload the blank authorization form. Add fields:
Place fields for cardholder details, billing address, amount, date, and signature. Send form:
Send the form to the cardholder for review and signing. Save records:
Download the completed form and audit trail for payment records.
What the authorization audit trail records
The audit trail documents who signed the card authorization, when each event occurred, and how the completed record can be retrieved for review.
Authenticate signer:
Timestamp events:
Hash document:
Seal record:
Track actions:
Export trail:
Recommended setup for card authorization
Configure the authorization workflow around signer attribution, payment-data protection, audit evidence, and the retention rule governing the underlying transaction.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS OTP |
| Signature type | Typed or drawn eSignature |
| Audit trail | Capture timestamps and signer actions |
| Document retention | Apply the governing record rule |
| Encryption | TLS 1.2/1.3 and AES-256 |
Retention periods for authorization records
Keep the completed authorization and audit evidence according to the record category it supports; the applicable rule determines the period.
3 years for tax records
6 years for understatement
6 years for HIPAA records
3 years for payroll records
6 years for broker records
Best practices for retaining card authorizations
A defensible card authorization record combines limited payment data, signer evidence, controlled access, and a retention period tied to its business purpose.
Minimize retained cardholder information
Preserve the audit trail
Map retention to the governing rule
Control archival access and deletion
Security controls for card authorization records
Payment protection:
Transit encryption:
Stored encryption:
Control assurance:
Security certification:
Healthcare protection:
Credit card authorization form troubleshooting
Resolve field, consent, authentication, plan, and payment-data issues before sending the authorization to a cardholder.
Upload the form again as a readable PDF, then review signNow’s detected fields before sending. Confirm that the cardholder name, billing address, amount, date, and signature fields align with the document.
Business includes legally binding eSignatures, templates, and audit trails. Business Premium adds bulk send, kiosk mode, request payments, and quick invite links. Select the plan based on the number and method of authorizations processed.
For a consumer-facing authorization, provide the ESIGN disclosure, explain the right to receive paper records, confirm electronic access, and explain withdrawal procedures under 15 U.S.C. §7001(c).
Use signer authentication appropriate to the payment risk. signNow supports SMS-based verification and stronger authentication options; record the completed audit trail with the authorization for attribution evidence.
A signNow subscription plan includes 100 signature invites per user per year, with overage fees. The Site License uses $1.50 per signature invite and is designed for usage-based volume.
signNow is PCI DSS certified and supports encryption in transit with TLS 1.2 or 1.3 and at rest with AES-256. Do not retain CVV unless a documented legal and payment-policy basis permits it.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.