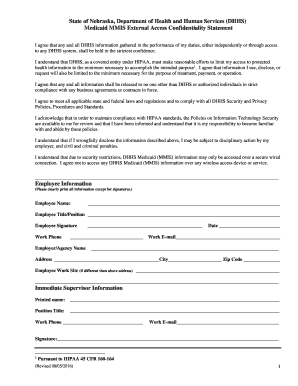
Dhhs Medicaid Mmis External Access Confidentiality Statement Form
Use a DHHS Medicaid MMIS External Access Confidentiality Statement template to make your document workflow more streamlined.
What this Medicaid confidentiality form does
The Dhhs Medicaid Mmis External Access Confidentiality Statement Form documents an external person’s acknowledgment and permitted access to Medicaid Management Information System information. It is completed by the authorized individual, reviewed by the responsible program or organization, and signed before access is granted or maintained. With signNow, the sender uploads the statement, checks detected fields, assigns the signer, sends the document, and retains the signed PDF with its audit trail. The form’s own instructions and agency policy control its exact fields and approval requirements.
Who uses this confidentiality statement
Medicaid program teams
Medicaid agency staff can use the statement to document an external party’s permitted access to MMIS-related information, while contractors and partners complete only the fields relevant to their authorization. The workflow supports controlled review, signer attribution, and retention of the final confidentiality record.
Authorized external parties
External consultants, vendors, auditors, and service providers can receive the form for review and signature before accessing approved Medicaid information. SignNow can route the statement to the designated signer and preserve the completed document with its signing history.
How this Medicaid form works
The signNow workflow keeps the form intact while guiding preparation, signature collection, and secure record handling.
Upload form: Upload the confidentiality statement PDF Check fields: Review detected fields and add missing fields Assign signer: Assign the authorized Medicaid recipient Complete record: Send, sign, and retain the completed record
Audit trail steps for this form
The audit trail records evidence around the confidentiality statement’s signing event rather than replacing the form’s authorization language.
Signer authentication:
Timestamp capture:
Document integrity:
Sealed history:
Action history:
Audit export:
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended setup for this form
Use controlled authentication, explicit signer intent, audit evidence, and secure retention when processing this Medicaid confidentiality statement.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Electronic signature with signer intent |
| Audit trail | Enable completion history and export |
| Document retention | Six years for HIPAA records |
| Encryption | TLS 1.2/1.3 and AES-256 |
Security for Medicaid confidentiality forms
Data encryption:
HIPAA safeguards:
SOC 2 Type II:
ISO 27001:
Secure transmission:
Stored document protection:
Platform requirements for this form
Complete the Dhhs Medicaid Mmis External Access Confidentiality Statement Form in Chrome, Firefox, Safari, or Edge on Windows or macOS. signNow also provides mobile apps for iOS and Android, allowing authorized users to review and sign from supported mobile devices.
Supported browsers Chrome, Firefox, Safari, and Edge Desktop systems Windows and macOS desktop access Mobile access iOS and Android mobile apps
Use organization-managed devices when the statement includes Medicaid access information. Administrators should apply approved identity controls, user provisioning, SSO, API, and certificate settings where required by the deployment. Confirm that the selected signNow plan and organizational policy support the required HIPAA safeguards and audit-trail retention.
Privacy pitfalls when completing the form
Sending the confidentiality statement to an unauthorized recipient can expose Medicaid-related information outside the approved access process. Leaving required identity, access-purpose, or signature fields blank can delay review of the completed confidentiality statement. Using a shared signing link without access controls may make signer attribution harder to establish. Failing to preserve the signed PDF and audit trail can weaken the record supporting authorized external access.
Best practices for this form
Accurate field assignment, controlled delivery, documented consent, and secure archival reduce preventable confidentiality and record-keeping problems.
Confirm the recipient and access purpose
Check every field assignment before sending
Capture informed electronic consent
Archive the signed form and audit trail
Legal standing of the signed statement
A completed electronic confidentiality statement can provide evidence of signer intent, attribution, consent, and record integrity under ESIGN, 15 U.S.C. ch. 96, and applicable state law such as UETA. The framework does not override exclusions for wills, certain court orders, family-law decrees, or other documents requiring special treatment.

Features for completing this form
signNow connects form preparation, authorized signing, audit evidence, and document retention for a controlled confidentiality-statement workflow.
Form preservation
Upload the existing confidentiality statement and preserve its original wording while adding signNow fields for completion and signature.
Field assignment
Assign access-purpose, acknowledgment, and signature fields to the authorized external signer before delivery.
Flexible delivery
Route the statement by email or controlled signing link without requiring every signer to create an account.
Audit trail
Capture signer actions, timestamps, and document history to support review of the completed confidentiality statement.
Data protection
Apply encryption in transit and at rest, with HIPAA safeguards available when a BAA is required.
Secure archival
Download the signed PDF and completion record for the organization’s approved Medicaid records repository.



Troubleshooting the confidentiality statement workflow
Resolve the form’s main signing, access, consent, plan, and retention questions before distributing a completed confidentiality statement.
Business includes legally binding eSignatures, templates, audit trails, and mobile apps at $8 per user per month with annual billing. Upload the confidentiality statement, assign fields, and send it through the signing workflow. Month-to-month pricing is higher at $20 per user per month.
HIPAA use requires a business associate agreement, not merely an account subscription. Confirm that the organization has the required BAA and configure access controls before sending a confidentiality statement containing protected health information.
If the uploaded PDF has no recognized fields, add text, date, acknowledgment, and signature fields manually. Review each placement before sending because automatic detection cannot confirm the form’s intended authorization language.
The Business Premium plan includes bulk send, while Business does not list bulk send in the verified plan details. Use Business Premium only when separate copies must be distributed repeatedly to identified recipients.
Consumer-facing electronic records require disclosure of the right to paper records, access to the electronic format, and procedures for withdrawing consent under 15 U.S.C. §7001(c). Provide those disclosures before the signer completes the form.
Export the completed PDF and audit trail after signing, then store them in the approved records system. If the record is a HIPAA record, retain it for six years from creation or last effective date under 45 CFR 164.530(j).
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.