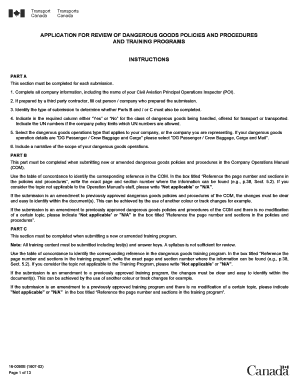
Application For Review Of Dangerous Goods Policies And Proceduresand Training Programs Form
Use a APPLICATION FOR REVIEW OF DANGEROUS GOODS POLICIES AND PROCEDURESAND TRAINING PROGRAMS template to make your document workflow more streamlined.
What this application is and does
The Application For Review Of Dangerous Goods Policies And Proceduresand Training Programs Form is a structured request for evaluating dangerous-goods policies, procedures, and related training programs. It gives an organization a single record for identifying the materials under review, documenting reviewer comments or decisions, confirming training information, and capturing approvals. The supplied form name does not identify an issuing agency, filing deadline, statutory threshold, or universal retention period. In signNow, upload the application, inspect detected fields, add reviewers and signers, collect signatures, and retain the completed PDF with its audit trail.
Who benefits from this application
The application suits organizations that must coordinate dangerous-goods policy review with documented training-program oversight.
A solo dangerous-goods consultant can use the application to document policy and training-program reviews without building a separate signature workflow. A regional carrier can route each application among operations, safety, and training teams, preserving approvals and reviewer accountability in one record. An enterprise logistics organization can standardize applications through shared templates, delegated sending, controlled permissions, and audit-trail retention across business units.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
How this application moves through signNow
The application moves from document preparation through policy review, training confirmation, signature collection, and auditable storage.
Upload the form: Upload the completed application and confirm every policy and training-program field. Prepare fields: Review detected fields and add required signer, date, and acknowledgment fields. Route for review: Send the application to reviewers and designated signers in sequence. Archive records: Collect signatures, preserve the final PDF, and export its audit trail.
Quick steps for completing the application
Use this sequence to prepare, route, sign, and preserve the Application For Review Of Dangerous Goods Policies And Proceduresand Training Programs Form.
Upload application:
Upload the current application PDF to signNow. Review fields:
Check detected fields and add missing review fields. Assign participants:
Assign policy reviewers and training-program signers. Complete and store:
Send, monitor completion, and download the signed record.
Features that fit this review workflow
signNow organizes this application’s policy review, training confirmation, signature collection, and recordkeeping steps in one electronic workflow.
Document upload
Upload the named application and preserve its original layout while preparing an electronic review workflow for designated participants.
Field detection
Auto-detected fields reduce manual placement work, while users can add missing signature, date, acknowledgment, or comment fields.
Role assignment
Assign reviewers and signers individually so policy decisions and training confirmations remain attributable to the correct participants.
Signer routing
Send the application through an ordered workflow when policy review must precede final approval or signature.
Audit trail
Capture timestamps, actions, and completion history alongside the signed application for later internal review.
Reusable workflow
Use templates and integrations to keep recurring dangerous-goods applications consistent across teams and connected systems.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended application workflow setup
Configure the application around accountable participants, documented consent, controlled access, and retention rules approved for your organization.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Electronic signature with intent evidence |
| Audit trail | Retain the completion history |
| Document retention | Follow the organization’s approved schedule |
| Encryption | TLS in transit and AES-256 at rest |
Security for review records
TLS and AES-256:
SOC 2 Type II:
ISO 27001:
Two-factor authentication:
HIPAA with BAA:
ESIGN and UETA:
What the audit trail records
The audit trail provides technical evidence of how this application moved from review preparation to signed completion.
Authenticate participant:
Capture timestamp:
Record document state:
Seal completion:
Track activity:
Export evidence:
Best practices for this application
Accurate routing and controlled records matter because this application combines policy review with training-program confirmation.
Identify the reviewed materials
Assign fields by responsibility
Apply the approved retention schedule
Test before sending the application



Platform requirements for this application
Use signNow through Chrome, Firefox, Safari, or Edge on Windows or macOS. The signNow mobile apps support completing and signing this application on iOS and Android devices.
Browsers Chrome, Firefox, Safari, and Edge Desktop systems Windows and macOS desktops Mobile systems iOS and Android mobile apps
Organizations managing dangerous-goods reviews should also consider device controls, account provisioning, and access policies for staff handling policy documents. Enterprise deployments may require API, SSO, or certificate configuration based on internal governance and the sensitivity of the materials attached to each application.
Legal standing of the signed application
For a business transaction, an electronic version of this application may be supported by the ESIGN Act, 15 U.S.C. ch. 96, and applicable state electronic-transactions law when intent, consent, attribution, and record retention are established. The supplied form name does not itself establish an agency filing rule. Wills, family-law decrees, and certain court filings remain outside ESIGN’s general coverage.

Challenges this workflow addresses
Reviewers receive an outdated policy or training-program version because the sender did not identify the materials under review. Required acknowledgments or signature fields are missing, leaving approval responsibility unclear in the completed application. Reviewer comments, supporting documents, and the final signed application are stored separately, weakening the review record. Signer order is incorrect, allowing final approval before the designated policy or training reviewer completes their assessment.
Managing access for review teams
An administrator creates a reusable application template, controls access, and assigns sender permissions to staff coordinating dangerous-goods policy and training reviews. A compliance coordinator uses delegated sending to route each application to reviewers and signers while preserving centralized templates, status visibility, and audit records.
Troubleshooting this application workflow
These answers address field setup, signer identity, legal use, plan selection, and record handling for this specific review application.
Upload the current PDF again, then inspect auto-detected fields before sending. If the source is a scan, add signature, date, acknowledgment, and reviewer fields manually so the dangerous-goods policy review cannot finish with missing required evidence.
Business includes templates, audit trails, mobile apps, and legally binding eSignatures at $8 per user monthly with annual billing. If bulk send or kiosk mode is required for this application, Business Premium adds those capabilities at $15 per user monthly annually.
The ESIGN Act supports electronic records when intent, consent, attribution, and retention requirements are met. For consumer-facing records, 15 U.S.C. §7001(c) also requires electronic-record disclosures and access procedures; confirm whether this application involves consumers.
Use SMS OTP or another configured authentication control when the reviewer’s identity needs stronger evidence than an email link. signNow’s product security options include two-factor authentication; your organization should set the required level for this application.
Use signNow’s audit trail to preserve timestamps, participant actions, routing history, and completion evidence with the signed application. Export the audit trail with the final PDF and store both under the organization’s approved records policy.
A 7-day free trial is available without a credit card, but plan limits and annual-billing terms still apply. Business subscription plans include 100 signature invites per user per year; confirm expected volume before sending repeated applications.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.