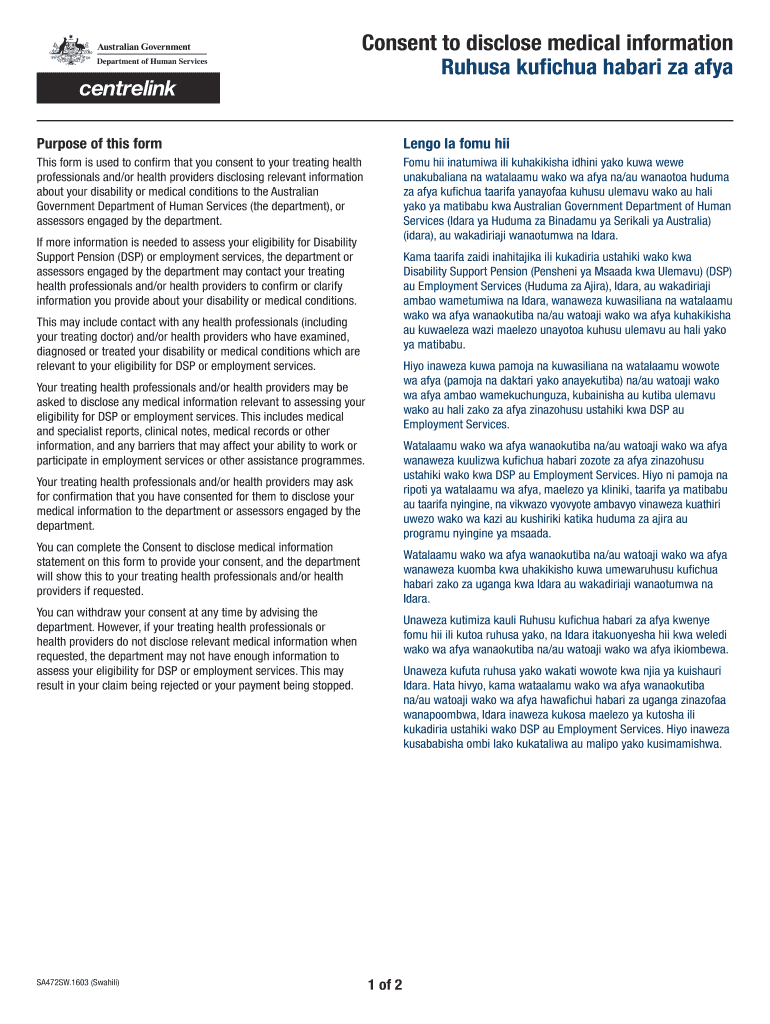
Consent To Disclose Medical Information Swahili Australian
Use a Consent To Disclose Medical Information Swahili Australian template to make your document workflow more streamlined.
What this medical consent form does
Consent To Disclose Medical Information Swahili Australian is a patient authorization allowing specified medical information to be released to an identified recipient for a stated purpose. The signer should review the information categories, recipient, purpose, expiration or event, and revocation terms before signing. In the United States, HIPAA governs many covered-entity disclosures, while state privacy law may add requirements. signNow can upload the form, detect fillable fields, route it for signature, and preserve the completed authorization with an audit trail. The platform does not determine whether a disclosure is legally permitted.
Who uses this medical consent form
Healthcare providers
Healthcare providers use this consent to document a patient’s authorization before releasing specified medical information to a named recipient.
Patients and representatives
Patients and authorized representatives review, sign, and retain the disclosure authorization for a defined purpose and recipient.
Who benefits from this consent workflow
The form supports patient authorization workflows across individual practices, release-of-information teams, and larger healthcare organizations.
Solo medical practices can collect patient authorizations remotely, identify the permitted recipient, and retain signed disclosure evidence without coordinating paper exchanges. Hospital release-of-information teams can route patient consents to approved staff, preserve audit trails, and organize authorizations before releasing specified records. Enterprise healthcare networks can standardize consent templates, delegate sending, and connect disclosure workflows with systems used by multiple clinics and departments.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
How to complete this consent form
Complete the medical disclosure consent by checking each authorization, identifying recipients, signing intentionally, and preserving the completed record.
Review the form:
Upload the completed consent form and confirm all patient and recipient details. Add signature fields:
Use signNow to detect fillable fields and place required signature, date, and initials fields. Send for signature:
Enter authorized recipient email addresses and send the medical disclosure consent securely. Store the record:
Review the signed copy, completion certificate, and audit trail before storing the record.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
What the audit trail records
The audit trail connects this medical disclosure consent to signer identity, document integrity, transaction timing, and evidence available for later review.
Authenticate signer:
Capture timestamps:
Hash document:
Seal transaction:
Record activity:
Export audit trail:
Recommended setup for medical consent
Use a controlled signing workflow that identifies the patient, limits disclosure scope, records authorization events, and protects the completed medical consent.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with two-factor authentication |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Detailed completion history and signer events |
| Document retention | Six years for HIPAA records under 45 CFR §164.530(j) |
| Encryption | TLS 1.2 or 1.3 and AES-256 encryption |
Security controls for medical consent
Protected health information:
Data in transit:
Data at rest:
Security assurance:
Signer verification:
Transaction evidence:
Privacy pitfalls in medical disclosure consent
Including broad medical categories without identifying the specific information authorized for release can make the patient’s intended disclosure unclear. Naming the wrong recipient, provider, or purpose can prevent the receiving party from relying on the signed authorization. Sending a completed consent through unmanaged email or storage can expose protected health information beyond authorized personnel. Omitting an expiration date or revocation process can create uncertainty about whether later disclosures remain authorized.
Legal standing of electronic consent
An electronic authorization may be enforceable when the signer demonstrates intent, consents to electronic records, can be attributed to the record, and the record remains retainable and reproducible under ESIGN, 15 U.S.C. ch. 96, and applicable UETA or New York ESRA rules. HIPAA and state law may impose additional content or process requirements.

Record-keeping practices for medical consent
Keep the signed authorization and evidence together, then apply the retention rule that governs the underlying health record and disclosure process.
Apply the correct health-record retention rule
Preserve authorization and completion evidence
Limit access to protected information
Verify scope before disclosure
Retention periods for related records
For this medical disclosure authorization, apply the retention rule governing the underlying record and document the applicable authority in your policy.
Six years — HIPAA records
Three years — tax records
Six years — tax understatement
Three years — payroll records
Five years — injury records



Medical consent form troubleshooting
Resolve signing, identity, privacy, plan, and retention questions before releasing medical information under this authorization.
On signNow Business, upload the consent form, place signature and date fields, and send it to the patient or representative. If the form contains sensitive health information, confirm the organization’s HIPAA configuration and required BAA before processing protected health information.
signNow supports HIPAA-compliant workflows when the required Business Associate Agreement is in place. HIPAA compliance does not decide whether the authorization’s recipient, purpose, scope, or expiration satisfies 45 CFR Part 164 and applicable state law.
Use two-factor authentication or another configured signer-verification method when identity assurance matters. The audit trail records transaction events, but staff must still confirm the signer is the patient or authorized representative.
If the recipient cannot access the email invitation, confirm the address, resend the request, or use a controlled signing link. Do not place protected health information in an unrestricted public link or unapproved communication channel.
The Business plan includes templates and audit trails; Business Premium adds bulk send and quick invite links. Select the plan based on workflow volume, then confirm any usage limits before sending multiple authorizations.
Export the signed authorization and completion evidence after signing, then store them in the approved health-record system. HIPAA requires six-year retention for covered records under 45 CFR §164.530(j), unless a longer applicable rule controls.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.