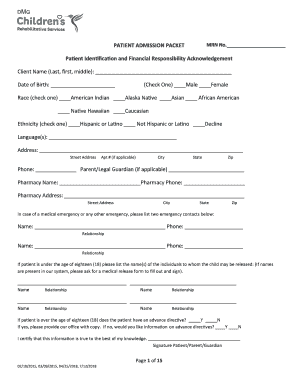
Patient Identication And Financial Responsibility Acknowledgement Form
Use a Patient Identication And Financial Responsibility Acknowledgement template to make your document workflow more streamlined.
What this patient acknowledgement does
The Patient Identication And Financial Responsibility Acknowledgement Form records a patient’s identity, insurance or guarantor information, and understanding of payment responsibility before healthcare services are provided or billed. It typically captures patient and subscriber details, financial-policy acknowledgement, consent, dates, and signatures. Staff review the entries, send the form to the patient or guarantor, and retain the signed record with the patient account. Electronic signing may be supported under ESIGN and applicable state law when intent, consent, attribution, and record reproduction are preserved.
Who benefits from this patient form
The form is most useful wherever healthcare staff must document patient identity and financial responsibility before treatment or billing.
Solo medical practices can collect patient identity, insurance, guarantor, and financial-responsibility acknowledgements before visits without printing separate packets for every appointment. Hospital registration teams can route the same acknowledgement to patients and guarantors, preserve completion evidence, and connect signed records with controlled billing workflows. Enterprise healthcare networks can standardize acknowledgement language across locations while assigning access, templates, and signing responsibilities to authorized registration and revenue-cycle teams.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Challenges with patient responsibility forms
Patients may leave insurance subscriber numbers, guarantor details, or consent fields blank, delaying billing review and signature completion. Mismatched patient names, birth dates, or insurance identifiers can prevent staff from linking the acknowledgement to the correct account. Paper acknowledgements are difficult to route between patients, guarantors, and billing teams without losing version control or completion evidence. Unclear financial-responsibility language can create disputes when patients later question deductibles, copayments, excluded services, or payment obligations.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Best practices for patient acknowledgements
Accurate patient data, clear financial terms, controlled access, and documented consent make this acknowledgement easier to administer and defend.
Verify patient and guarantor details
Match language to financial policy
Require every essential field
Protect and retain signed records
Recommended patient form setup
Configure the acknowledgement around verified patient identity, clear intent to sign, controlled access, and retention appropriate to the health record.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS OTP |
| Signature type | Electronic signature with intent |
| Audit trail | Capture IP, timestamps, and actions |
| Document retention | Six years for HIPAA records |
| Encryption | TLS 1.2/1.3 and AES-256 |
How the patient form audit trail works
The audit trail connects the patient’s authentication, acknowledgement actions, completed fields, and final signed PDF into a retrievable record.
Authenticate signer:
Timestamp action:
Hash document:
Seal document:
Record activity:
Retrieve audit trail:
Retention periods for signed acknowledgements
Retention depends on the record’s role, the provider’s policies, and applicable federal or state requirements; use the longest applicable period.
Six years from creation or date
Three years for federal tax records
Three years for payroll records
Five years after reporting year
Thirty years for exposure records
Risks of incomplete acknowledgements
Consent dispute
Billing mismatch
Evidentiary gap
Privacy violation
Patient form signing tools compared
signNow provides a documented patient-signing workflow; competitor capabilities shown as Not verified where the supplied vendor data does not confirm them.
| signNow | DocuSign | Adobe Acrobat Sign | Availability |
|---|---|---|---|
| Required patient signatures | Yes | Yes | Yes |
| Audit trail capture | Yes | Yes | Yes |
| Healthcare compliance support | HIPAA with BAA | Not verified | Not verified |
| Signer authentication | SMS OTP | Not verified | Not verified |
Troubleshooting patient form signing
Use these answers to resolve field, authentication, compliance, plan, and retention questions while processing this specific patient acknowledgement.
Upload the Patient Identication And Financial Responsibility Acknowledgement Form as a PDF, let signNow detect fillable fields, then verify patient, guarantor, date, and signature placements before sending. Required fields prevent incomplete submissions but do not validate the accuracy of entered insurance information.
Use signNow’s required fields for patient acknowledgement, signature, and date, and review the completed PDF before filing. HIPAA compliance requires a business associate agreement where applicable; HIPAA does not replace the provider’s obligation to verify content and access controls.
Business costs $8/user/month with annual billing and includes legally binding eSignatures, templates, mobile apps, and audit trails. Business Premium costs $15/user/month annually and adds bulk send, kiosk mode, payments, and quick invite links.
If the patient cannot open the email, confirm the address, resend the request, or create a shareable signing link. Use SMS OTP or another enabled authentication method when stronger signer attribution is required by policy.
Electronic signing is generally supported when the signer demonstrates intent, consents to electronic records, can be attributed, and the provider retains a reproducible record under ESIGN and applicable state law. Exclusions include wills, certain court filings, and family-law decrees.
HIPAA-covered records generally require six years from creation or the last effective date under 45 CFR §164.530(j). Apply any longer state, payer, medical-record, or litigation-hold requirement before deleting the signed PDF or audit trail.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.