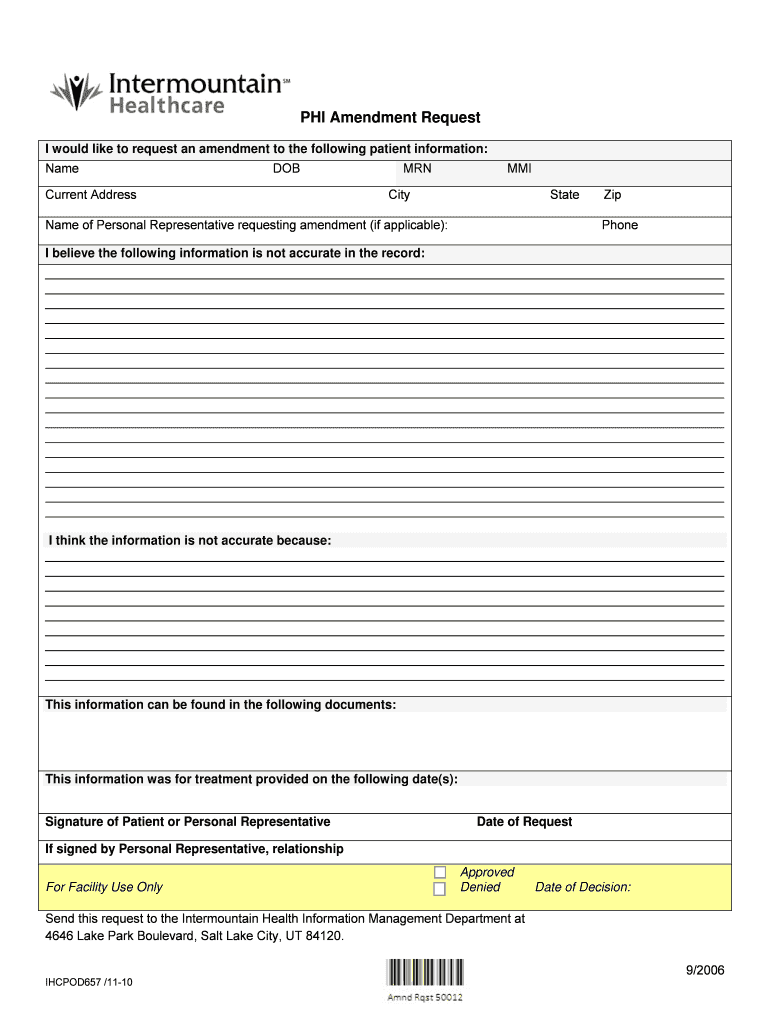
Phi Amendment Request Intermountain Healthcare Form
Use a PHI Amendment Request Intermountain Healthcare template to make your document workflow more streamlined.
What the Phi amendment request form does
The Phi Amendment Request Intermountain Healthcare Form records a healthcare privacy amendment request and the actions needed to review it. It gives an authorized individual a structured way to identify the requested correction, provide relevant supporting information, and sign the submission. In signNow, the source document is uploaded, fillable fields are detected or added, and the completed request is routed to designated signers. The finished document and audit trail can then be stored for the healthcare organization’s records. HIPAA documentation must be retained for six years from creation or the last effective date under 45 CFR 164.530(j).
Who handles Phi amendment requests
Health-information-management staff can prepare, route, and archive Phi amendment requests using shared templates, administrator permissions, and audit trails that document signer activity without circulating paper records. Patients or authorized representatives can review the requested amendment information and sign electronically when the organization’s identity, consent, and HIPAA procedures permit electronic completion through signNow.
How the Phi amendment workflow works
signNow converts the Phi Amendment Request Intermountain Healthcare Form into a controlled electronic workflow from upload through signed-record storage.
Upload document: Upload the Phi amendment source document. Prepare fields: Auto-detect fillable fields and add missing fields. Route for signing: Send the amendment request to authorized signers. Archive evidence: Store the completed record and audit trail.
Complete the Phi amendment in signNow
Follow the document-specific signNow workflow to prepare, route, sign, and preserve the Phi Amendment Request Intermountain Healthcare Form.
Upload document:
Upload the Phi amendment PDF. Check fields:
Review detected fields and add missing fields. Assign signers:
Assign authorized recipients and signing order. Complete workflow:
Send, monitor, and download the completed record.
Security for Phi amendment records
TLS 1.2 and 1.3:
AES-256 at rest:
HIPAA with BAA:
SOC 2 Type II:
ISO 27001 certified:
ESIGN and UETA:
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Review the Phi amendment audit trail
The signNow audit trail records identity, timing, document integrity, and delivery events for each completed Phi Amendment Request Intermountain Healthcare Form.
Signer authentication:
Timestamp capture:
Document hashing:
Tamper sealing:
Action history:
Audit export:
Recommended Phi amendment workflow setup
Configure the Phi Amendment Request Intermountain Healthcare Form around signer identity, PHI safeguards, audit evidence, and controlled access.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS two-factor authentication |
| Signature type | Electronic signature with signer intent |
| Audit and retention | Export audit trail with six-year HIPAA retention |
| Encryption | TLS 1.2 or 1.3 and AES-256 |
| User provisioning | Role-based access through managed administrators |
Use mobile devices for Phi amendments
Complete the Phi Amendment Request Intermountain Healthcare Form through signNow mobile apps for iOS and Android. Browser access supports current Chrome, Firefox, Safari, and Edge releases over TLS 1.2 or TLS 1.3.
Mobile apps iOS and Android apps Offline signing Offline signing availability Camera capture Camera document capture
Healthcare staff can review amendment information, capture supporting pages with a device camera, and sign from managed mobile devices. Confirm offline availability for the selected workflow before relying on it in locations with limited connectivity, then synchronize completed records securely when access returns.



Legal standing for Phi amendment records
A completed Phi Amendment Request Intermountain Healthcare Form can provide admissible evidence when signer intent, consent, attribution, and reliable retention are demonstrated. ESIGN, 15 U.S.C. chapter 96, and applicable state law support electronic records, while UETA generally governs intrastate transactions. Wills, court filings, and specified family-law documents remain excluded.

Risks from incomplete Phi amendments
Consent evidence
Signer attribution
Privacy disclosure
Record correction
Evidence gap
Phi amendment record retention schedule
Retain the signed request, supporting evidence, and related HIPAA documentation according to 45 CFR 164.530(j), which requires six years from creation or the last effective date. State healthcare-record rules may require longer retention.
Six-year HIPAA period
Six-year policy period
Six-year security period
Six-year amendment period
Six-year authorization period
Record-keeping practices for Phi amendments
Preserve the signed amendment, audit evidence, authorization, and retention history together so reviewers can reconstruct the request without reopening the original workflow.
Export the signed record and audit trail
Verify identity before sharing PHI
Apply the six-year HIPAA period
Limit fields and exposed information
Privacy challenges in Phi amendment workflows
Sending the Phi amendment to an unverified recipient can expose protected health information and undermine the organization’s disclosure controls. Accepting a representative’s signature without documenting authorization can leave the amendment request unsupported during a privacy review. Granting broad template or folder access can allow unauthorized staff to view, edit, or download signed PHI records. Failing to preserve the audit trail with the signed request can weaken evidence of consent, attribution, and completion timing.
Phi amendment troubleshooting questions
Resolve field, signer, privacy, plan, and retention issues before releasing a completed Phi Amendment Request Intermountain Healthcare Form.
signNow Business includes templates, mobile apps, and audit trails for routing this amendment request. Business Premium adds bulk send and kiosk mode when staff must distribute the same approved request repeatedly. Choose the plan based on workflow volume and signing context.
A HIPAA workflow requires appropriate safeguards and a business associate arrangement where applicable. signNow identifies HIPAA compliance as requiring a BAA. Confirm the organization’s BAA, access controls, retention policy, and permitted PHI handling before sending.
If auto-detection misses a field, open the uploaded Phi Amendment Request Intermountain Healthcare Form in the editor and place the needed text, date, checkbox, or signature field manually. Review every page before assigning recipients.
Use signNow’s signer authentication options, including two-factor authentication where configured, to strengthen attribution. Verify that the recipient is the patient or authorized representative before disclosure, because an audit trail cannot correct a wrong recipient.
The completed record should include the signed document and its audit trail. Export both from signNow and retain them under the organization’s HIPAA record policy; 45 CFR 164.530(j) sets a six-year documentation period.
Electronic signatures generally receive legal recognition under ESIGN and UETA when intent, consent, attribution, and record reproduction are established. Consumer-facing records also require the ESIGN disclosure process under 15 U.S.C. §7001(c).
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.