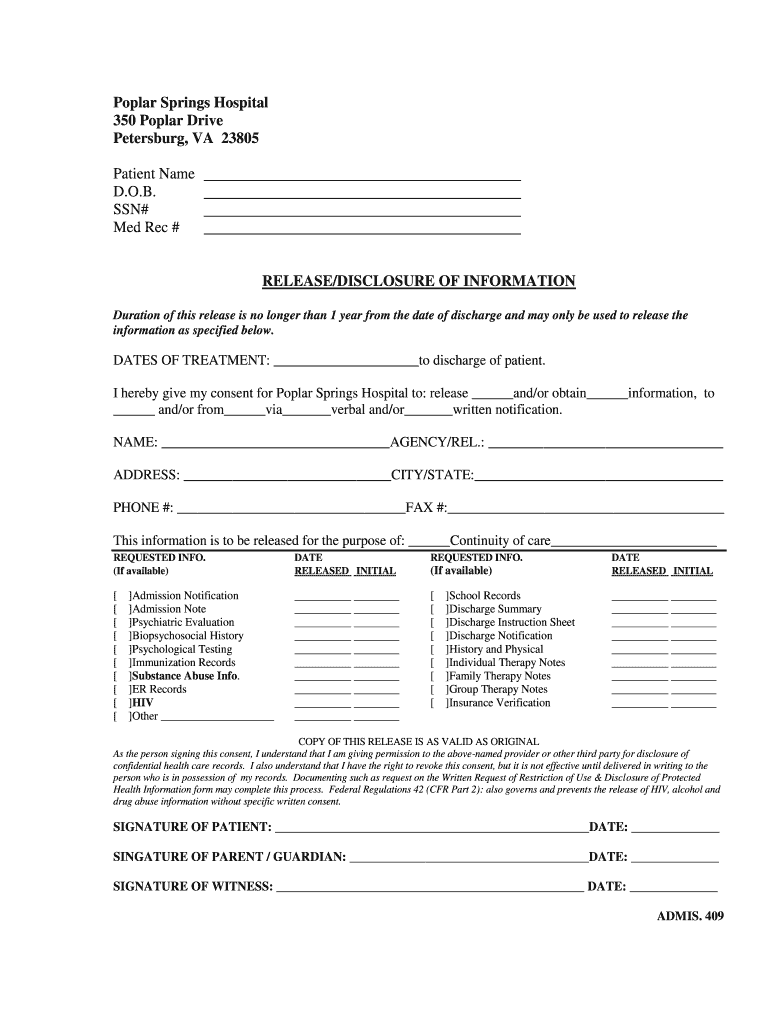
Release Of Information Poplar Springs Hospital
Use a Release Of Information Poplar Springs Hospital template to make your document workflow more streamlined.
What this hospital release does
A Release Of Information Poplar Springs Hospital form authorizes the hospital to disclose specified patient information to a named recipient for a stated purpose and period. The patient or legally authorized representative reviews the requested records, signs the authorization, and receives a completed copy. With signNow, staff upload the hospital form, review detected fields, assign the signer, and send it electronically. The completed release and audit trail can then be retained for compliance review, subject to HIPAA and applicable state requirements.
How the hospital release workflow works
The signNow workflow moves the Poplar Springs Hospital authorization from preparation through signature and controlled record storage.
Upload form: Upload the hospital release and inspect detected fields. Assign roles: Assign patient, representative, and staff roles. Request signature: Send the authorization for secure signing. Preserve evidence: Store the signed release and audit trail.
Complete the hospital release in four steps
Prepare the Poplar Springs Hospital authorization, confirm its disclosure scope, collect the required signature, and preserve the completed record.
Upload form:
Upload the Poplar Springs Hospital release form and let signNow detect fillable fields. Check fields:
Review patient, recipient, purpose, records, expiration, and signature fields before sending. Send signer:
Add the patient or authorized representative as signer and send the release securely. Archive record:
Review the completed release, then store the signed copy with its audit trail.
Audit trail for the hospital authorization
The audit trail records who interacted with the Poplar Springs Hospital release, when actions occurred, and how the completed authorization can be reviewed.
Authenticate signer:
Capture timestamp:
Hash document:
Seal record:
Track activity:
Export trail:
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended release workflow setup
A controlled setup helps Poplar Springs Hospital authenticate signers, document consent, protect health information, and preserve evidence for the required retention period.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS OTP |
| Signature type | Electronic signature with signer intent |
| Audit trail | Capture timestamps, IP, and actions |
| Document retention | 6 years under HIPAA 45 CFR 164.530(j) |
| Encryption | TLS 1.2/1.3 and AES-256 |
Security for hospital information releases
HIPAA compliance:
Transport encryption:
Storage encryption:
Security certification:
Information security:
Document history:
Retention schedule for signed releases
Retain the authorization and related evidence according to the record category, HIPAA requirements, and Poplar Springs Hospital’s approved state-specific schedule.
Six years — HIPAA records
Not applicable — IRS records
Not applicable — I-9 records
Not applicable — FINRA records
State schedule — verify locally
Record-keeping practices for releases
Use a repeatable records process that connects authorization scope, signer evidence, audit history, disclosure review, and secure retention for every hospital release.
Preserve the complete authorization package
Export and restrict audit evidence
Verify authorization scope before disclosure
Strengthen identity and correction controls
Privacy pitfalls in hospital releases
Patient authorization may omit permitted recipients, purposes, expiration dates, or specific record categories, creating uncertainty before Poplar Springs Hospital discloses information. Unprotected email attachments can expose diagnoses, treatment details, or identifying information after the Release Of Information Poplar Springs Hospital is signed. A signer may approve the release without reviewing the recipient, requested records, or expiration terms, weakening evidence of informed authorization. Shared accounts or excessive permissions can let unauthorized staff send, edit, or retrieve the hospital release form and its audit trail.
State rules and document exclusions
Check state rules
Excluded document
Excluded proceeding
Recordation issue
Legal standing of signed releases
A signed Release Of Information Poplar Springs Hospital can document patient authorization when the signer’s intent, consent, identity, and record access are preserved. ESIGN and UETA generally recognize qualifying electronic signatures, while HIPAA governs protected health information handling. Wills, court filings, and certain family-law documents remain excluded from ESIGN.

Healthcare release workflow examples
Healthcare teams can adapt signNow workflows to patient authorizations while retaining responsibility for disclosure decisions and privacy controls.
Healthcare operations
Fertility Centers of Illinois needed a healthcare workflow for collecting patient signatures while maintaining structured electronic records and accessible signing processes.
- Healthcare authorization workflow
Fertility Centers of Illinois founder John Butler described the signNow API as effective for the organization. That experience illustrates how a healthcare provider can connect signing workflows to operational systems, while the hospital must still define its own authorization language, disclosure scope, patient identity controls, and HIPAA retention policy.
Hospital records
A hospital records team can use the same workflow to route a patient authorization, verify the intended recipient, and preserve the signed release.
- Patient records workflow
The workflow separates form completion from disclosure review: staff prepare the authorization, the patient or representative signs, and the records team checks scope before release. signNow supplies the audit trail and signed copy; Poplar Springs Hospital remains responsible for validating the authorization and applying its privacy procedures.
Troubleshoot hospital release signing
Resolve field, signer, privacy, plan, evidence, and legal-recognition questions before disclosing information under the hospital authorization.
Upload the original PDF again and inspect whether scanned pages contain usable fields. signNow can detect fillable areas, but staff should verify patient, recipient, purpose, expiration, and signature fields manually before sending.
Confirm that the signer’s email address is correct and resend the invitation. For protected health information, add SMS OTP or another configured authentication control before the patient or representative signs.
HIPAA compliance requires a business associate agreement where applicable and does not replace Poplar Springs Hospital’s authorization review. Confirm the release scope, recipient, minimum necessary disclosure, and retention policy before sending.
Business includes audit trails and templates, while Business Premium adds bulk send and kiosk mode. Choose the plan according to the hospital’s volume, signing location, and administrative controls.
Review the audit trail for the signer, timestamps, IP address, and completed actions. Preserve the signed PDF and exported audit evidence together under the hospital’s approved records schedule.
Electronic signatures generally receive legal recognition under ESIGN and UETA when intent, consent, attribution, and record reproduction are established. Excluded records, including wills and certain court filings, require a separate legal process.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.