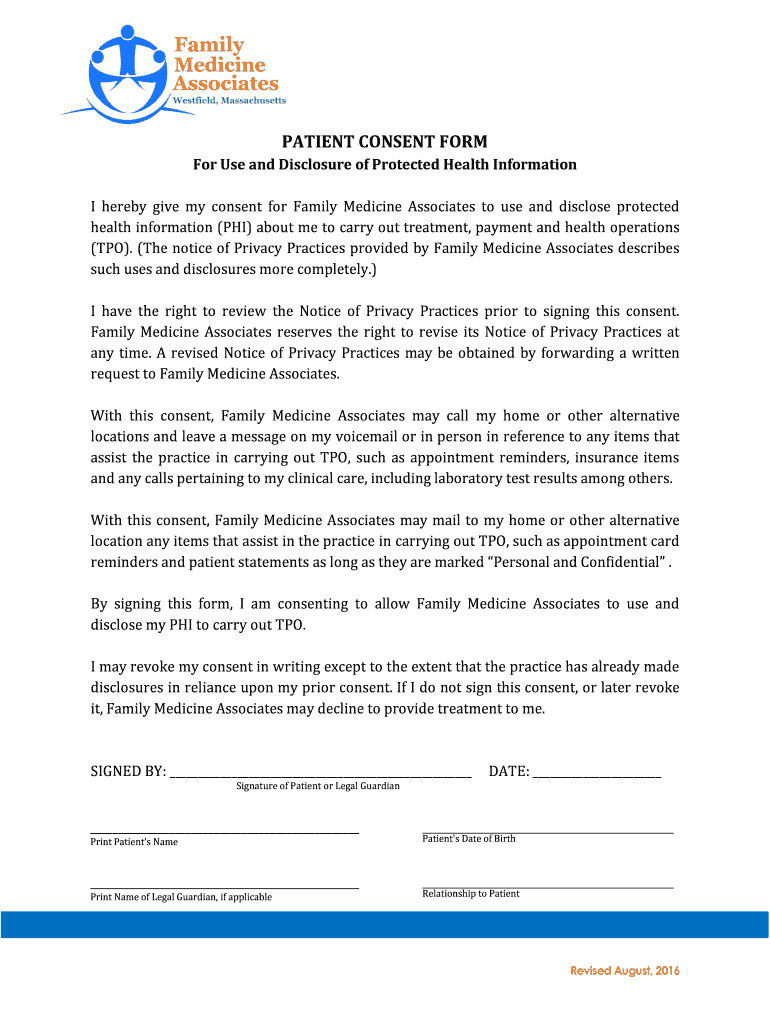
Patient Consent Form Phi Patient Consent Form Phi
Use a Patient Consent Form PHI Patient Consent Form PHI template to make your document workflow more streamlined.
What the patient consent form records
The Patient Consent Form Phi documents a patient’s permission for a stated healthcare use or disclosure of information. In practice, the patient or authorized representative reviews the exact purpose, information involved, recipients, expiration or withdrawal terms, and signature fields before signing. Upload the form to signNow, identify its fillable fields, send it to the intended signer, and preserve the completed record with an audit trail. HIPAA-covered entities should align the form and retention policy with 45 CFR 164.508 and 45 CFR 164.530(j).
Who uses the patient consent form
Healthcare providers
Healthcare providers use the Patient Consent Form Phi to document patient permission for a defined use or disclosure of protected health information. Staff can prepare reusable fields, send the form for signature, and preserve the signed authorization with its audit history. HIPAA-covered workflows require appropriate privacy policies and a business associate agreement when applicable.
Specialty practices
Medical practices, fertility centers, and specialty clinics can use the form when patients must review disclosure details before authorizing a stated recipient or purpose. signNow supports browser and mobile signing, while administrators can restrict access and connect completed records to systems such as Salesforce, Microsoft 365, Google Drive, or Box.
Key features for patient consent forms
Patient Consent Form Phi workflows combine structured fields, verified signing, audit evidence, and controlled storage for healthcare consent records.
Field placement
Upload the Patient Consent Form Phi, place required consent and signature fields, and keep the document ready for consistent completion across your healthcare workflow.
Remote signing
Collect a patient’s consent signature through a browser or mobile device while preserving the completed form and signing activity for later review.
Signer verification
Use signer authentication controls appropriate for patient information, including email delivery and stronger verification when your policy requires it.
Audit trail
Retain the signed consent document with its completion history so staff can confirm who signed, when signing occurred, and which version was completed.
HIPAA workflow
Protect patient information with a HIPAA-compliant signNow workflow when a business associate agreement is in place and access is controlled.
System connections
Connect completed consent records to healthcare operations through named integrations such as Salesforce, Microsoft 365, Google Drive, or Box.
How this consent workflow works
The signNow workflow turns the Patient Consent Form Phi into a controlled sequence from upload through documented authorization.
Upload form: Upload the Patient Consent Form Phi to the signNow workspace. Check fields: Auto-detect fillable fields, then verify consent and signature placement. Send securely: Send the completed template to the patient or representative. Preserve evidence: Store the signed form with its completion history and audit trail.
Complete the patient consent form
Follow these steps to prepare, send, complete, and preserve the Patient Consent Form Phi in signNow.
Upload document:
Upload the Patient Consent Form Phi document to signNow. Verify fields:
Review auto-detected fields and add missing consent fields. Address signer:
Enter the patient’s email or create a controlled signing link. Send form:
Send the authorization for review and signature. Archive record:
Download or store the signed record with its audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
What the audit trail records
The audit trail documents the signing event separately from the form’s clinical or disclosure terms.
Authenticate signer:
Timestamp action:
Record activity:
Seal record:
Link evidence:
Export history:
Recommended consent form setup
Configure the Patient Consent Form Phi around patient identity, documented intent, protected health information, and controlled staff access.
| Setting | Recommendation |
|---|---|
| Authentication and provisioning | Email verification with controlled staff access |
| Signature type | Electronic signature with recorded signer intent |
| Audit trail | Retain completion history with signer actions |
| Document retention | Six years when HIPAA retention applies |
| Encryption | AES-256 at rest and TLS 1.2 or 1.3 in transit |
Security for consent records
HIPAA coverage:
Stored encryption:
Transport encryption:
Security report:
Security certification:
Regulated records:



Best practices for patient consent
Use the Patient Consent Form Phi as a precise authorization record, not merely as a signature page.
Define the disclosure before signing
Preserve intent and signer evidence
Control the approved template
Complete the HIPAA safeguards
Rollout and retention timeline
A controlled rollout connects form preparation, patient signing, audit evidence, and retention obligations without treating consent as a generic document.
Prepare the form:
Send for signature:
Complete authentication:
Store the record:
Seven-day trial:
HIPAA retention:
Access review:
Policy check:
Legal standing of patient consent
A Patient Consent Form Phi can provide evidence of authorization when it identifies the intended use or disclosure, records the signer’s intent and consent, and remains reproducible with its completion history. ESIGN and applicable state electronic-transactions law support electronic signatures, while HIPAA authorization requirements arise under 45 CFR 164.508. Wills, court orders, and family law decrees remain outside ESIGN’s universal coverage.

Privacy pitfalls in patient consent
Listing a broad purpose instead of the specific use or disclosure can make the patient’s authorization unclear under 45 CFR 164.508. Sending the form to an incorrect recipient can expose protected health information before identity and access controls are confirmed. Omitting the patient’s right to revoke authorization can weaken the disclosure record and create avoidable compliance questions. Failing to preserve the signed form and completion history makes it harder to demonstrate what the patient actually authorized.
Key performance indicators that demonstrate SignNow's proven track record.
Patient consent form troubleshooting
These answers address the signNow workflow, HIPAA authorization requirements, and evidence needed for the Patient Consent Form Phi.
Upload the Patient Consent Form Phi as a PDF or supported document, then review signNow’s detected fields before sending. Auto-detection does not replace a staff review: confirm that purpose, recipient, expiration, revocation language, and signature fields match the authorization required under 45 CFR 164.508.
The Business plan costs $8 per user per month when billed annually and includes legally binding eSignatures, templates, audit trails, and mobile apps. Business Premium costs $15 per user per month annually and adds bulk send, kiosk mode, payments, and quick invite links.
signNow states that HIPAA compliance requires a business associate agreement. A healthcare organization should execute the required BAA, limit access to authorized personnel, and align its Patient Consent Form Phi workflow with its privacy and security policies before processing protected health information.
Use signNow’s audit trail and completion history to review signer actions, timestamps, and the final document. Store the exported evidence with the consent record, then apply the organization’s retention schedule and HIPAA’s six-year requirement when applicable under 45 CFR 164.530(j).
If a signer cannot complete the form, verify the recipient address, resend the invitation, or provide a controlled signing link. Confirm that the patient or authorized representative is the intended signer; do not substitute another person merely because the invitation was delivered.
Electronic signing does not replace required consent language or state-specific healthcare rules. Under ESIGN and UETA, enforceability depends on intent, consent to electronic records, attribution, and record reproducibility. Review 45 CFR 164.508 and applicable state law before relying on the authorization.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.