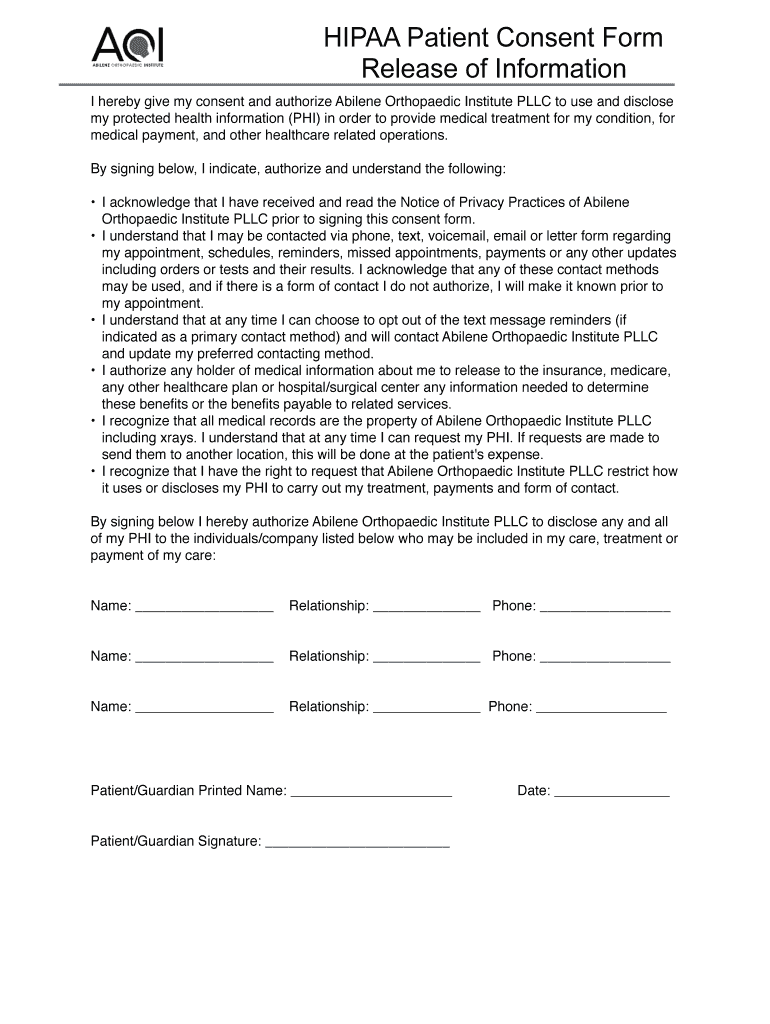
Patient Consent Release Information Form
Use a Patient Consent Release Information Form template to make your document workflow more streamlined.
What this patient release form does
A Patient Consent Release Information Form gives a patient a documented way to authorize disclosure of specified health information to a named recipient. It identifies the patient, recipient, purpose, information covered, expiration or revocation terms, and signer authorization. A healthcare organization can upload the form to signNow, review or add fields, send it to the patient, capture an electronic signature, and retain the completed record with an audit trail. HIPAA and state privacy rules still control the underlying disclosure.
Who uses this patient release form
Healthcare providers
Healthcare providers use the Patient Consent Release Information Form to document a patient’s authorization before disclosing specified medical information to a named person, organization, or care-related recipient.
Patients and representatives
Patients or authorized representatives review the release scope, recipient, purpose, expiration, and privacy language before signing the authorization.
Key features for patient consent releases
A structured digital workflow helps healthcare organizations collect, verify, sign, and retain patient authorization without losing the details that define its scope.
Clear scope
Capture the patient’s authorization, recipient, purpose, and release scope in one structured record that can be reviewed before disclosure.
Required fields
Place signature, date, initials, and acknowledgment fields directly on the Patient Consent Release Information Form for complete execution.
Remote signing
Send the release to patients by email or signing link, allowing remote completion without routing paper through the office.
Audit trail
Use signNow’s audit trail to preserve signing actions, timestamps, and document history alongside the completed authorization.
Reusable template
Reuse an approved release template while keeping patient-specific names, recipients, purposes, and expiration details editable for each request.
Controlled records
Store completed releases with controlled access so authorized healthcare staff can retrieve the patient’s consent record when needed.
How to complete the patient release
Use this workflow to prepare, sign, and retain a Patient Consent Release Information Form in signNow.
Upload form:
Upload the completed Patient Consent Release Information Form. Check fields:
Review detected fields and place missing fields. Add signer:
Add the patient or representative as signer. Send request:
Send the release through signNow. Save record:
Store the signed form and audit trail.
Recommended release workflow setup
Configure the Patient Consent Release Information Form workflow around patient identity, authorization evidence, protected information, and accountable record retention.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Enabled for every completed release |
| Document retention | Six years for HIPAA records |
| Encryption | TLS 1.2/1.3 and AES-256 |
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
What the consent audit trail records
A signNow audit trail documents how the Patient Consent Release Information Form moved from invitation to completed authorization.
Signer authentication:
Timestamp capture:
Document hashing:
Tamper-evident seal:
Action logging:
Audit retrieval:
Security for patient release records
HIPAA protection:
SOC 2 Type II:
ISO 27001:
Transport encryption:
Stored encryption:
Signer authentication:
Platform requirements for signing
Patients can open the Patient Consent Release Information Form in Chrome, Firefox, Safari, or Edge on Windows and macOS, or use signNow mobile apps on iOS and Android.
Browsers Chrome, Firefox, Safari, Edge Desktop systems Windows and macOS desktops Mobile apps iOS and Android mobile apps
Healthcare organizations should use managed devices, approved accounts, and access controls when handling patient information. Confirm network access, authentication settings, and audit-trail retrieval procedures before deploying the workflow across staff or facilities.



Record-keeping practices for releases
Retention and access controls should preserve both the patient’s signed authorization and the evidence needed to understand later disclosures.
Apply the six-year HIPAA reference
Preserve the audit evidence
Archive releases securely
Track changes and revocations
Privacy pitfalls in patient releases
Including more health information than the stated purpose permits can expose sensitive data and undermine the patient’s informed authorization. Missing recipient names, expiration terms, or signature dates can make the release difficult to interpret or rely on during disclosure. Sending the completed form through unrestricted email or shared folders can expose protected health information to unauthorized recipients. Failing to document revocation requests can cause staff to disclose information after the patient has withdrawn authorization.
Legal standing of patient consent releases
A Patient Consent Release Information Form records a patient’s authorization and can support disclosure decisions when its scope, intent, signer attribution, and retained copy are clear. ESIGN and UETA generally recognize electronic signatures, but wills, certain court filings, and family-law decrees remain excluded; HIPAA and state privacy rules still govern disclosures.

Retention periods for related records
Apply the retention rule tied to the record’s actual purpose; state requirements may impose longer periods than these federal references.
Six years — HIPAA records
Three years — tax records
Six years — substantial understatement
Three years — payroll records
Five years — injury records
Compare consent-form signing plans
signNow pricing and capabilities are verified; competitor figures remain unverified where the available source provides no comparable data.
| Features | signNow | DocuSign | Adobe Sign | PandaDoc | Dropbox Sign |
|---|---|---|---|---|---|
| Starting price | $8/user/month, Business plan, billed annually | Not verified | Not verified | Not verified | Not verified |
| Free trial | 7-day trial, no credit card required | Not verified | Not verified | Not verified | Not verified |
| Bulk send | Available with Business Premium at $15/user/month | Not verified | Not verified | Not verified | Not verified |
| Audit trail | Included with Business plan subscriptions | Not verified | Not verified | Not verified | Not verified |
| HIPAA compliance | Available with BAA requirement and applicable configuration | Not verified | Not verified | Not verified | Not verified |
| Annual signature invites | 100 invites per user annually; overage fees apply | Not verified | Not verified | Not verified | Not verified |
Patient consent release troubleshooting
These answers address signing, privacy, plan, authentication, and retention issues that arise when processing this specific patient authorization.
On the Business plan, signNow provides templates, legally binding eSignatures, and audit trails for this release workflow. Review every patient-specific field before sending because the platform does not determine whether the proposed disclosure complies with HIPAA or state privacy law.
signNow’s HIPAA compliance requires a business associate agreement. Configure the healthcare organization’s account and handling procedures accordingly; an electronic signature alone does not authorize disclosure of information outside the release’s stated scope.
Business Premium includes bulk send, but bulk delivery should be limited to identical, approved documents. Patient names, recipients, purposes, and expiration terms usually differ, so review each Patient Consent Release Information Form before sending.
If a patient cannot complete the form, verify the email address, resend the invitation, or provide a signing link through an approved channel. Use SMS OTP or another configured authentication method when stronger identity evidence is required.
The audit trail records signing events, timestamps, and document history, but staff must still retain the completed release according to applicable HIPAA and state requirements. HIPAA records generally require six years under 45 CFR §164.530(j).
Electronic signatures generally receive legal recognition under ESIGN and UETA when intent, consent, attribution, and record reproducibility are established. Consumer-facing records may require an ESIGN disclosure, and healthcare privacy obligations remain separate from signature validity.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.