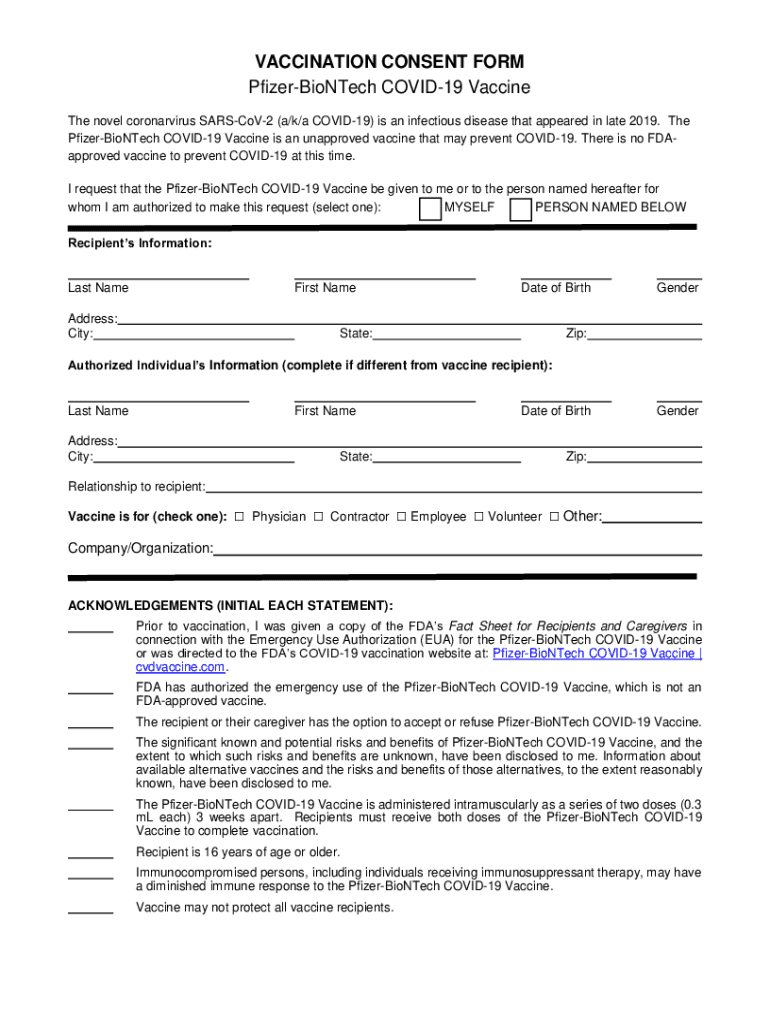
Pfizer Biontech Consent Form
Use a Pfizer Biontech Consent Form template to make your document workflow more streamlined.
What the Pfizer-BioNTech consent form does
The Pfizer-BioNTech consent form records a patient’s or guardian’s authorization for vaccination and preserves the signer’s acknowledgment before administration. A provider prepares the document, identifies the required signer, captures the electronic signature and date, and retains the completed record. With signNow, the provider uploads the form, reviews detected fields, sends it for signing, and receives a completed document with an audit trail. Healthcare organizations handling protected health information should address HIPAA requirements, including a business associate agreement where applicable, and follow state-specific consent rules.
Who uses this consent form
Healthcare providers
Healthcare clinics and vaccination sites use the Pfizer-BioNTech consent form to collect patient or guardian authorization before administering the vaccine and to preserve the signed record.
Vaccination programs
Pharmacies, mobile vaccination teams, and occupational-health programs use assigned signer fields and audit trails to manage consent collection across desktop and mobile workflows.
Legal standing of electronic consent
An electronic Pfizer-BioNTech consent record can support a U.S. transaction when the signer demonstrates intent, consents to electronic records, can be identified, and the record remains reproducible. ESIGN, 15 U.S.C. ch. 96, and applicable state law such as UETA provide the framework, while wills, court filings, and other statutory exclusions require separate review.

Complete the Pfizer-BioNTech consent form
Use this signNow workflow to prepare the Pfizer-BioNTech consent form, route it to the appropriate signer, and preserve completion evidence.
Upload form:
Upload the Pfizer-BioNTech consent form to signNow. Check fields:
Review detected fields and add missing patient or signer fields. Assign signer:
Assign the patient or guardian as the required signer. Send form:
Send the form and monitor completion status. Store record:
Download the completed form and audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Features for Pfizer-BioNTech consent records
signNow combines field preparation, signer routing, audit evidence, mobile access, and storage connections for Pfizer-BioNTech consent workflows.
Field detection
Upload the Pfizer-BioNTech consent form and review detected fields before sending it for completion.
Signer routing
Route the consent form to a patient or guardian with assigned signature and date fields.
Audit trail
Capture signing actions, timestamps, and document history for the completed consent record.
Mobile signing
Use signNow mobile apps when vaccination staff collect signatures away from a desk.
Data protection
Protect patient information with encryption in transit and at rest, subject to the selected workflow.
Cloud storage
Connect completed consent records with Google Drive, Box, or Egnyte for controlled storage.
Audit trail for consent completion
For a Pfizer-BioNTech consent form, the audit trail documents who acted, when they acted, and how the completed record was preserved.
Signer identity:
Timestamp capture:
Document history:
Change evidence:
Audit review:
Export record:
Security for consent records
Stored data:
Data transfer:
Health information:
Service controls:
Security management:
Privacy controls:
Privacy and consent pitfalls
A consent record may expose patient identifiers when downloaded, emailed, or stored outside an approved healthcare repository. A patient or guardian may sign the wrong field if signer roles are not assigned before sending. A staff member may grant access to completed consent records without applying role-based permissions. A missing consent disclosure or incomplete signature sequence can weaken evidence that the patient authorized vaccination.
Best practices for signed consent
Use the approved document, identify the correct signer, protect patient information, and preserve the completed form with its audit evidence.
Use the approved form version
Assign the correct signer
Protect patient information
Archive the evidence record



Retention schedule for consent records
Retention depends on the record’s healthcare, employment, and exposure-record context. Apply the longest controlling requirement after reviewing state law and organizational policy.
Six years from creation
Six years under HIPAA
Three years after hire
Thirty years for exposure
Policy-defined archival period
Risks of incomplete vaccine consent records
Consent dispute
Guardian signature
Evidence gap
Privacy violation
Troubleshooting Pfizer-BioNTech consent workflows
These answers address field detection, healthcare privacy, signer access, audit evidence, and electronic-consent requirements for this vaccination consent workflow.
Upload the Pfizer-BioNTech consent form again as a readable PDF, then inspect signNow’s detected fields before sending. Add any missing patient, guardian, date, or signature fields manually rather than assuming automatic detection captured every required entry.
Business includes templates, audit trails, mobile apps, and legally binding eSignatures at $8 per user per month with annual billing. If the workflow requires bulk send or kiosk mode, Business Premium adds those features at $15 per user per month.
For a healthcare workflow involving protected health information, signNow identifies HIPAA compliance as requiring a business associate agreement. Execute the BAA and configure access controls before sending patient-related consent records.
If a patient or guardian cannot complete the email invitation, verify the address, resend the invitation, or use an approved signing link. Confirm the signer identity before accepting the completed Pfizer-BioNTech consent form.
Use signNow’s audit trail to review the signer event, timestamps, document history, and completion record. Under ESIGN and UETA, enforceability depends on intent, electronic consent, attribution, and retained reproducible records, not merely a visible signature.
Do not treat an electronic consent record as permission for every healthcare use. For consumer-facing electronic records, ESIGN requires disclosure of the right to paper, electronic access, and procedures for withdrawing consent under 15 U.S.C. §7001(c).
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.