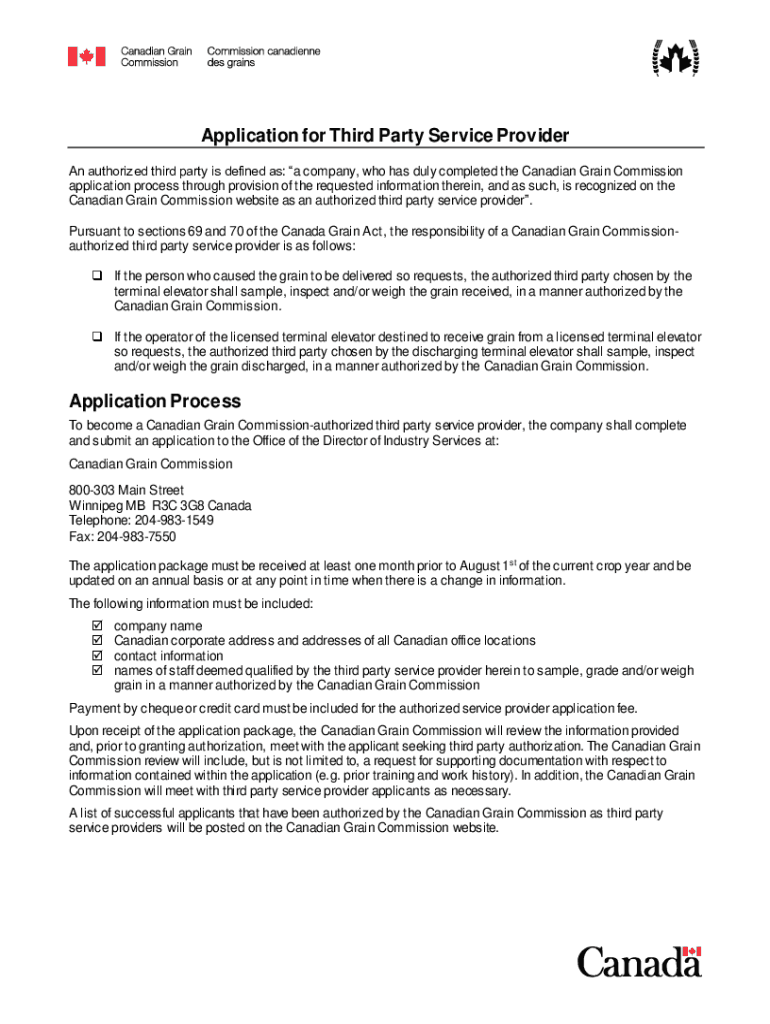
Application For Third Party Service Provider Form
Use a Application For Third Party Service Provider template to make your document workflow more streamlined.
What this provider application does
The Application For Third Party Service Provider Form records information and approvals needed to evaluate or onboard an outside service provider. Because the supplied materials do not identify an issuing agency, official fields, filing deadline, or statutory threshold for this exact form, users should follow the requesting organization’s instructions rather than assume it is an IRS, USCIS, or state government filing. In signNow, upload the document, review detected fields, send it to the authorized signer, and store the completed PDF with its audit trail.
Who uses this provider application
Procurement teams
Procurement teams can use the application for onboarding service providers, collecting business details, approvals, contracts, NDAs, invoices, and supporting consent records in one traceable workflow.
Regulated organizations
Healthcare, financial-services, legal, construction, and education organizations can adapt the application workflow to provider agreements while limiting access to sensitive information and retaining completed records.
Business types using provider applications
The right workflow depends on whether one person, a regulated department, or an enterprise procurement group manages provider onboarding.
A solo procurement consultant can send provider applications, collect signatures, and preserve audit trails without maintaining paper files or separate signature appointments. A healthcare organization can route provider applications through controlled access, use a HIPAA-compliant signNow workflow with a BAA, and restrict completed records containing protected health information. An enterprise procurement department can reuse approved templates, delegate sending, connect signNow with systems such as NetSuite or Salesforce, and maintain consistent approval evidence across provider relationships.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
How to complete this provider form
Use this sequence for the Application For Third Party Service Provider Form, while following the requesting organization’s instructions for required information.
Upload form:
Upload the provider application. Check fields:
Review detected fields and add missing fields. Add signer:
Enter the authorized provider signer. Complete record:
Send, sign, and store the audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended provider application setup
Use controlled access, explicit signing evidence, encrypted storage, and a retention rule matched to the provider information collected.
| Setting | Recommendation |
|---|---|
| Authentication and provisioning | Use administrator-controlled access with invited users |
| Signature type | Use typed, drawn, or click-to-sign fields |
| Audit trail | Retain the completed document and certificate |
| Document retention | Apply six years for HIPAA records |
| Encryption | Use TLS 1.2/1.3 and AES-256 |
Audit trail for provider applications
A signNow audit trail links the provider application to signer activity, timestamps, document history, and the retained completed record.
Authenticate signer:
Capture timestamps:
Record document history:
Preserve signer actions:
Retrieve signed file:
Export evidence:
Platform requirements for provider applications
Complete the Application For Third Party Service Provider Form through a current web browser using TLS-protected signNow access. Chrome, Firefox, Safari, and Edge support desktop workflows on Windows and macOS, while signNow mobile apps support iOS and Android devices.
Browsers Chrome, Firefox, Safari, and Edge Desktop systems Windows and macOS desktop access Mobile systems iOS and Android mobile apps
Organizations should manage provider applications through approved Windows, macOS, iOS, or Android devices. Enterprise deployments may connect signNow through API integrations and SSO provisioning; certificate or long-term validation requirements should be reviewed when a regulated workflow requires them.
Security for provider applications
Transport encryption:
Stored data:
Security reporting:
Information security:
Health information:
Electronic signatures:



Compare form-signing plan options
For this provider application, signNow pricing is verified; competitor pricing and feature details are not verified in the supplied data.
| Features | signNow | DocuSign | Adobe Sign | PandaDoc | Dropbox Sign |
|---|---|---|---|---|---|
| Starting price annually | $8/user/month Business plan | Not verified in supplied vendor data | Not verified in supplied vendor data | Not verified in supplied vendor data | Not verified in supplied vendor data |
| Free trial availability | 7-day trial, no card required | Not verified in supplied vendor data | Not verified in supplied vendor data | Not verified in supplied vendor data | Not verified in supplied vendor data |
| Bulk send availability | Business Premium plan includes bulk send | Not verified in supplied vendor data | Not verified in supplied vendor data | Not verified in supplied vendor data | Not verified in supplied vendor data |
| Audit trail availability | Business plan includes audit trails | Not verified in supplied vendor data | Not verified in supplied vendor data | Not verified in supplied vendor data | Not verified in supplied vendor data |
Recordkeeping practices for provider applications
A defensible record connects the provider application, signer, consent, completed document, and audit trail while applying the rule that matches the information collected.
Define retention by record content
Export the audit trail
Archive sensitive provider information
Document consent and authority
Privacy and disclosure pitfalls
Including unnecessary taxpayer, banking, health, or identity information increases disclosure exposure if the completed application is shared beyond procurement reviewers. Sending before confirming the provider’s authorized signer can weaken attribution and require a second signing cycle. Failing to capture consumer electronic-record consent can create an ESIGN disclosure problem for consumer-facing applications. Leaving completed applications in unrestricted folders can expose provider data to users without a business need.
Troubleshooting provider applications
Resolve field, signer, consent, compliance, and retention questions before treating an application as complete.
Upload the Application For Third Party Service Provider Form as a PDF, review signNow’s detected fields, and add missing signature, date, or approval fields manually before sending.
The Business plan is $8 per user monthly when billed annually and includes legally binding eSignatures, templates, mobile apps, and audit trails. Business Premium adds bulk send at $15 per user monthly annually.
signNow states that HIPAA workflows require a business associate agreement. Confirm the application contains protected health information before selecting the applicable compliance process.
For consumer-facing electronic records, ESIGN requires disclosure of the right to receive paper records, electronic access capability, and withdrawal procedures under 15 U.S.C. §7001(c).
Use an invited signer, email authentication, or stronger authentication where the provider relationship requires it. Confirm signer authority before sending because signNow cannot determine corporate authority for you.
Export the completed application and audit trail after signing. Electronic signatures generally receive legal recognition under ESIGN and applicable state law, but exclusions include wills, court filings, and family-law decrees.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.