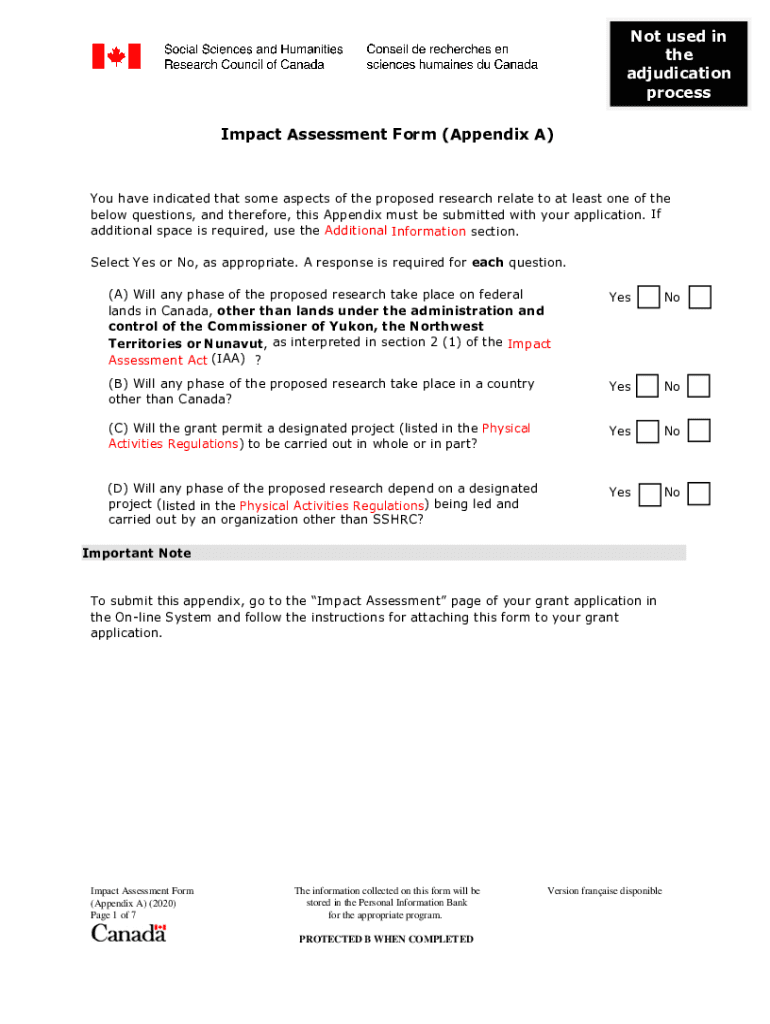
Impact Assessment Form Appendix A
Use a PDF Impact Assessment Form Appendix A template to make your document workflow more streamlined.
What Impact Assessment Form Appendix A covers
Impact Assessment Form Appendix A is a structured record for documenting an organization’s assessment of a proposed activity, process, or project. It captures the subject being reviewed, affected parties, identified impacts, mitigation measures, responsible personnel, approvals, and supporting notes. The completed appendix creates a dated record of the assessment rather than a tax filing or government submission. Upload the form to signNow, review its fillable fields, assign each required signer, and retain the completed PDF with its audit trail. Applicable approval, privacy, and retention requirements depend on the organization and state law.
Platform requirements for completing the appendix
Use an updated browser with TLS 1.2 or 1.3 enabled. signNow supports Chrome, Firefox, Safari, and Edge on Windows and macOS, plus iOS and Android mobile apps.
Browser support Chrome, Firefox, Safari, and Edge on Windows or macOS Mobile access signNow mobile apps for iOS and Android devices Connection security TLS 1.2 or 1.3 secures transmitted assessment records
Organizations handling sensitive assessment information should use managed Windows, macOS, iOS, or Android devices, enforce account controls, and confirm that assigned signers can access the PDF. Enterprise deployments may also configure API access, SSO provisioning, and certificate or long-term validation requirements where applicable.
Who benefits from this assessment appendix
The appendix helps small practices, regulated departments, and distributed enterprises document decisions consistently before work begins.
A solo environmental consultant can document site findings, mitigation recommendations, and client approval in one dated appendix before delivering the assessment record to stakeholders. A healthcare compliance department can use the appendix to record a proposed workflow’s effects on patient information, assign reviewers, and preserve approvals alongside supporting documentation. A large construction or infrastructure enterprise can standardize project-impact reviews across regional teams, route approvals by role, and retain completed appendices for internal governance and audits.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Features that support assessment completion
signNow features connect the appendix’s fields, reviewers, signatures, and retained evidence into one traceable completion workflow.
Reusable template
A reusable signNow template keeps assessment headings, impact fields, mitigation details, and approval areas consistent across projects without retyping the document structure.
Field detection
Auto-detected fields help identify blank areas after upload, making it easier to place names, dates, signatures, initials, and approval fields on the appendix.
Approval routing
Role-based routing sends the appendix to reviewers in sequence, so responsibility for assessment, mitigation, and final approval remains visible to every participant.
Signed record
The completed PDF and certificate of completion preserve the signed assessment together, giving reviewers a clear record of what was approved and when.
Audit trail
An audit trail records signer activity, timestamps, IP information, and document actions, supporting later review of the appendix’s execution history.
Mobile signing
Mobile apps let authorized participants review or sign the assessment from iOS or Android devices when project teams work away from a desktop.
Recommended setup for the assessment workflow
Configure authentication, signing, evidence capture, retention, and encryption before sending Impact Assessment Form Appendix A for approval.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Capture timestamps, IP addresses, and actions |
| Document retention | Retain under the organization’s documented policy |
| Encryption | TLS 1.2 or 1.3 and AES-256 |
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Documents requiring special handling
Missing notarization
Wills and codicils
Family law orders
Real-estate deeds
Managing assessment teams and permissions
An administrator can create a controlled Impact Assessment Form Appendix A template, assign roles, and limit editing or sending permissions so project teams use the approved structure. Shared templates reduce duplicate versions while preserving centralized oversight of who may initiate an assessment workflow, change fields, or view completed records. Delegated sending lets an authorized coordinator prepare the appendix for another responsible sender, while signNow routing places reviewers and approvers in the required order. Teams can use role-based access, shared templates, and audit trails to distinguish the person who prepared the assessment from those who reviewed or signed it.
Ways to send and sign the appendix
- Use the signNow web app when preparing the appendix, checking detected fields, assigning reviewers, and monitoring completion from a desktop workspace.
- Use the signNow mobile app when a project participant must review or sign Impact Assessment Form Appendix A from an iOS or Android device.
- Use kiosk mode for supervised, in-person completion when several participants must sign the same assessment on a controlled device.
- Use a shareable signing link when approved recipients need access without a separate email invitation, while maintaining the appendix’s audit trail.
How the appendix workflow works
The workflow moves from document preparation to review, signature, and preservation of the completed Impact Assessment Form Appendix A.
Upload: Upload appendix PDF Check fields: Review detected fields Route: Assign reviewers Archive: Store signed evidence
What the appendix audit trail records
The audit trail documents execution evidence after the assessment is sent, rather than replacing the appendix’s substantive findings or approval decisions.
Authenticate signer:
Capture timestamp:
Hash document:
Seal record:
Build audit trail:
Retrieve evidence:
Processing stages for the assessment appendix
No universal statutory turnaround period is provided for this appendix; timing depends on preparation, reviewer availability, and internal approval policy.
Prepare the document
Deliver to reviewers
Collect approvals
Complete and archive
Record-keeping practices for the appendix
A reliable record includes the completed appendix, its audit trail, the approval context, and a retention rule tied to the underlying business activity.
Complete every assessment field
Export the audit evidence
Set a purpose-based retention rule
Archive the signed appendix securely
Security controls for assessment records
Data in transit:
Stored document security:
Security assurance:
Information security:
Electronic signatures:
Protected health information:



Privacy and disclosure pitfalls
Sending the appendix to every project participant can expose personal information beyond the people who need it for assessment or approval. A missing consent or acknowledgment field can leave the record unable to show that a participant agreed to electronic processing. Unrestricted template permissions can allow an unauthorized user to alter impact questions, mitigation fields, or approval routing before sending. Replacing a signed appendix with an edited file can break the connection between the approved content and its audit trail.
Key performance indicators that demonstrate SignNow's proven track record.
Troubleshooting Impact Assessment Form Appendix A
Resolve field, signer, plan, legal, audit-trail, and privacy questions before the appendix is finalized or shared.
Upload the original PDF again and confirm it is not password-protected or flattened incorrectly. signNow’s field-detection process can identify fillable areas, but a sender should review every detected field and manually add missing signature, date, or approval fields before sending.
The Business plan includes templates, audit trails, and legally binding eSignatures at $8 per user per month when billed annually. If the workflow needs bulk send, Business Premium is listed at $15 per user per month annually.
ESIGN and UETA generally recognize electronic signatures when intent, consent, attribution, and record retention are demonstrated. Consumer-facing transactions may also require the ESIGN disclosure under 15 U.S.C. §7001(c). Confirm any organization-specific or state requirements before sending.
Add an email or SMS-based authentication step, then verify the signer’s identity before approval. For higher-risk assessments, an organization may require stronger authentication. signNow Enterprise includes advanced signer authentication, while exact controls should follow internal policy.
Export the completed PDF and its certificate of completion, then preserve the audit trail with the organization’s records. The audit trail documents timestamps, signer activity, IP information, and actions, but it does not replace a retention policy or legal hold.
Review the appendix for personal information before sending and restrict access to assigned reviewers. signNow supports encryption in transit with TLS 1.2 or 1.3 and at rest with AES-256; HIPAA workflows require a business associate agreement.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.