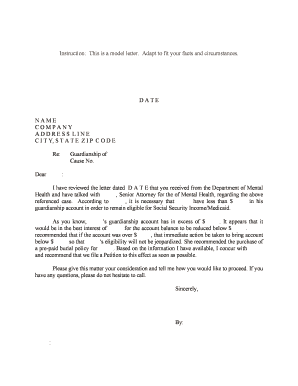
I Have Reviewed The Letter Dated D A T E That You Received From The Department Of Mental Form
Use a I Have Reviewed The Letter Dated D A T E That You Received From The Department Of Mental template to make your document workflow more streamlined.
What this department letter form records
This form records that a person reviewed a letter dated by the relevant department, but the supplied form name does not identify an issuing agency, statutory deadline, or official form code. In practice, the signer should compare the letter’s date, sender, recipient, and review language before completing the acknowledgement. signNow can hold the uploaded document, place signature and date fields, route it to the intended signer, and preserve an audit trail showing authentication, timestamps, and actions. Apply the organization’s privacy and retention policy, especially when the letter contains protected health information.
Who uses this department letter form
Mental health providers
Mental health providers can use the form to document receipt and review of department correspondence, subject to privacy controls and applicable record-retention rules.
Healthcare administrators
Administrative teams can route the letter for acknowledgement, preserve signer evidence, and retrieve the completed record during an authorized review.
How this department letter workflow works
The workflow keeps the received department letter, review acknowledgement, signature, and completion record together in one controlled process.
Upload the letter: Upload the received mental health department letter and identify every required acknowledgement field. Review details: Review wording, dates, recipient details, and any privacy-sensitive information before signing. Send for review: Send the prepared document to the designated reviewer through signNow. Store records: Complete the acknowledgement, then retain the signed copy and audit trail.
Steps to complete the department letter
Use this sequence to prepare the received department letter, obtain the required acknowledgement, and preserve evidence of completion.
Upload document:
Upload the received department letter into signNow. Check fields:
Review detected fields and add missing signature or date fields. Add signer:
Enter the designated reviewer’s email address. Complete record:
Send, sign, and preserve the completed audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended setup for the department letter
Configure the workflow around signer identity, sensitive mental health information, auditability, and the organization’s documented retention policy.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Capture timestamps, IP address, and signer actions |
| Document retention | Follow the applicable health-record retention policy |
| Encryption | TLS 1.2/1.3 and AES-256 protection |
Security for the department letter
Transport encryption:
Storage encryption:
Security certification:
Information security:
Healthcare safeguards:
Electronic signatures:
Legal standing of the signed acknowledgement
A signed acknowledgement may be admissible when the signer intended to sign, consented to electronic records, can be identified, and the record remains reproducible under ESIGN, 15 U.S.C. ch. 96, and applicable UETA law. Those frameworks do not automatically cover wills, codicils, testamentary trusts, court orders, or family-law decrees.

Platform requirements for this form
Use signNow through Chrome, Firefox, Safari, or Edge on Windows or macOS, or through the signNow mobile apps on iOS and Android. Transport protection uses TLS 1.2/1.3.
Supported browsers Chrome, Firefox, Safari, and Edge Desktop systems Windows and macOS desktop access Mobile apps iOS and Android mobile apps
Organizations handling sensitive department letters should manage devices, user permissions, and approved storage centrally. Enterprise deployments may also require API access, SSO provisioning, and documented controls for audit-trail export and retention.
Privacy challenges with this department letter
Uploading the full department letter can expose unnecessary personal or clinical information to staff who only need to process the acknowledgement. Sending the acknowledgement to an unverified recipient can disclose mental health information and weaken evidence that the intended person reviewed it. Failing to capture electronic consent can create uncertainty about whether the signer agreed to receive and sign the department letter electronically. Leaving shared templates or completed letters broadly accessible can permit unauthorized viewing, downloading, forwarding, or alteration of sensitive records.
Risks of mishandling the department letter
Consent dispute
Attribution gap
Audit weakness
Privacy exposure



Business types using this department letter
The form is most useful where a received department letter requires documented review, controlled access, and evidence of completion.
A solo mental health practitioner can upload the received letter, complete the review acknowledgement, and preserve a signed copy without coordinating paper exchanges or separate audit documentation. A clinic administration team can use shared templates, delegated sending, and controlled permissions to route department letters consistently while limiting access to authorized staff handling protected information. An enterprise behavioral-health organization can connect signNow with approved systems, apply stronger signer authentication, and standardize audit-trail retention across multiple departments and locations.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Troubleshooting the department letter workflow
These answers address field detection, signer access, healthcare privacy, electronic-signature evidence, plan selection, and preservation of the completed acknowledgement.
Upload the original PDF again and check whether it is password-protected, image-only, or damaged. signNow can place fields after upload, but an unreadable source may require manual field placement or a clean scanned copy.
Open the recipient’s signNow invitation from the intended email address, then complete any configured authentication step. If SMS OTP is enabled, verify the phone number and request a new code rather than forwarding the invitation.
For mental health information, confirm whether the workflow involves a HIPAA-covered entity or business associate. signNow identifies HIPAA compliance with a BAA requirement; the organization remains responsible for its privacy and access controls.
The Business plan includes legally binding eSignatures, templates, audit trails, and mobile apps at $8 per user per month when billed annually. Business Premium adds bulk send at $15 per user per month annually.
A signer may use a typed or drawn signature if the workflow demonstrates intent and consent. Consumer-facing records may require the ESIGN disclosure, paper-record option, electronic-access confirmation, and withdrawal procedures under 15 U.S.C. §7001(c).
Export the signed PDF and certificate of completion, then preserve the audit trail with the received letter. signNow records signer actions and timestamps, but the organization must select retention based on the record’s actual legal category.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.