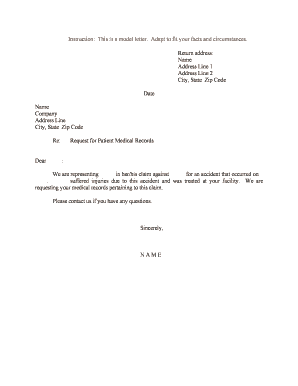
Request For Patient Medical Records Form
Use a Request For Patient Medical Records template to make your document workflow more streamlined.
What this patient records request does
A Request For Patient Medical Records Form authorizes a healthcare provider to release specified medical records to a named recipient. The requester identifies the patient, describes the records and date range, names the recipient, and signs the authorization. The provider uses those details to evaluate and process the disclosure. When protected health information is involved, HIPAA requirements and applicable state law remain relevant. signNow can capture the electronic signature, preserve completion details, and retain an audit trail, but it does not replace the provider’s disclosure review or authorization policy.
Healthcare teams using patient record requests
The form is useful wherever a healthcare organization must document a patient’s authorization before releasing specified medical records to an identified recipient.
Solo medical practices use the form to obtain a patient’s authorization before sending designated records to another physician, insurer, attorney, or the patient’s chosen representative, while keeping the signed request and audit trail together for office records. Hospital release-of-information departments use it to standardize patient identity checks, requested date ranges, recipient details, and authorization signatures before processing disclosures from a larger designated record set. Healthcare networks and telehealth enterprises use shared templates and controlled sending workflows to collect patient authorizations across clinics, while administrators maintain consistent HIPAA documentation and access controls for each participating location.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Who uses this patient records form
Healthcare providers
Clinics and medical-records departments use the authorization to identify the patient, define the requested records, name the recipient, and document the patient’s approval before disclosure.
Patients and representatives
Patients or their authorized representatives review the requested scope, confirm the recipient and delivery details, and sign the authorization before the provider processes the release.
How the patient records request works
The workflow moves from document preparation to authenticated signing and documented storage without changing the request’s medical-record details.
Upload the form: Upload the patient-record request form to signNow. Review detected fields: Auto-detect fillable fields and review every field. Send for signature: Send the authorization to the patient or representative. Archive the record: Store the signed request with its audit trail.
Recommended authorization workflow setup
Configure the Request For Patient Medical Records Form around patient identity, disclosure scope, signer evidence, protected health information, and documented retention.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS OTP |
| Signature type | Electronic patient signature |
| Audit trail | Enabled for every authorization |
| Document retention | 6 years under HIPAA 45 CFR 164.530(j) |
| Encryption | TLS 1.2/1.3 and AES-256 |
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Features for patient record authorizations
The workflow combines patient-specific field capture, electronic signing, audit evidence, and controlled handling of a medical-record disclosure authorization.
Structured details
Capture the patient’s name, birth date, requested records, date range, recipient, and signature in one structured authorization workflow.
Field review
Auto-detected fields help prepare the uploaded request while allowing staff to review and correct every patient-specific field before sending.
Remote signing
Send the authorization to the patient or representative by email, then track completion without requiring paper handling.
Audit trail
Preserve timestamps, signer actions, and completion evidence with the authorization for later disclosure review.
HIPAA controls
Apply signNow’s HIPAA compliance controls with a BAA when the request contains protected health information.
Document retention
Keep the signed authorization available for the provider’s records-management process and applicable retention requirements.
What the audit trail records
For a patient-record authorization, the audit trail preserves technical evidence about identity, actions, timing, document integrity, and later retrieval.
Authenticate signer:
Capture timestamp:
Hash document:
Seal document:
Log activity:
Export audit trail:
Security for patient record requests
HIPAA protection:
Transit encryption:
Stored encryption:
Security certification:
Information security:
Privacy controls:
Platform requirements for signing
Use Chrome, Firefox, Safari, or Edge on Windows or macOS to prepare the Request For Patient Medical Records Form. signNow mobile apps support signing on iOS and Android, subject to the organization’s device and security policies.
Supported browsers Chrome, Firefox, Safari, Edge Operating systems Windows, macOS, iOS, Android Mobile access signNow mobile apps available
Healthcare organizations should use managed devices, controlled access, and approved storage procedures when handling protected health information. Enterprise deployments may also require API access, SSO provisioning, and documented configuration for authentication, retention, and audit-trail retrieval.
Best practices for patient record requests
Accurate patient identifiers, a narrow disclosure scope, and a documented signing history help healthcare organizations process this authorization safely.
Identify the patient and requested records
Define the precise disclosure scope
Verify the recipient securely
Archive the authorization and audit trail
Retention rules to review carefully
Retention depends on the record category and governing rule; a patient-record authorization generally calls for the HIPAA documentation period, while state requirements may extend it.
HIPAA documentation retention
Federal tax records retention
Employment verification records
Payroll record retention
Injury record retention
Privacy pitfalls in patient record requests
Sending records to an unverified email address can disclose protected health information to the wrong recipient and create a reportable privacy incident. A missing patient signature, date, or requested date range can prevent the provider from confirming authorization before releasing records. Including more records than the patient authorized can exceed the documented disclosure scope and conflict with the provider’s HIPAA procedures. Sharing completed authorizations with staff who lack a business need can weaken access controls for sensitive patient information.
Legal standing of the authorization
A signed patient-record authorization can document intent, signer attribution, electronic consent, and a reproducible record under ESIGN and applicable state electronic-transactions law, including UETA or New York ESRA. It does not override HIPAA requirements, state medical-record rules, or exclusions such as wills and court filings.

Troubleshooting patient record requests
Resolve field, authentication, plan, and compliance questions before releasing any patient medical records through the completed authorization.
On signNow’s Business plan, upload the patient-record request, place or review signature and date fields, and send it to the intended signer. Business includes templates and audit trails at $8 per user per month with annual billing; confirm HIPAA requirements and a BAA before processing PHI.
signNow states that HIPAA compliance requires a BAA. Before sending a patient-record authorization containing protected health information, confirm that the organization’s signNow arrangement includes the required BAA and apply internal access, disclosure, and retention policies.
A patient may need stronger authentication than an email link when the request contains sensitive information. signNow’s Enterprise plan adds advanced signer authentication; configure the available method according to organizational policy and the risk of the disclosure.
If auto-detection misses a patient name, date range, recipient, or signature field, inspect the original PDF and add the missing fields manually. Do not send the authorization until every required patient and disclosure detail is present.
The Business plan includes 100 signature invites per user per year, with overage fees applying after that allowance. Business Premium includes bulk send for repeated authorization workflows; select a plan based on actual sending volume rather than assuming unlimited invitations.
Electronic signing can support an authorization when the signer demonstrates intent, consents to electronic records, can be attributed, and the record remains reproducible. ESIGN and applicable state law govern electronic transactions, while HIPAA separately governs protected health information handling.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.