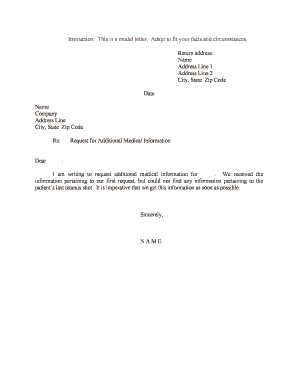
I Am Writing To Request Additional Medical Information For
Use a I Am Writing To Request Additional Medical Information For template to make your document workflow more streamlined.
What this medical information request does
This form asks an authorized person or organization to provide additional medical information for a defined healthcare, insurance, employment, disability, or legal purpose. The requester identifies the information needed, the recipient, the authorization basis, and any applicable limits. With signNow, upload the request, place text and signature fields, send it to the intended signer, and preserve the completed copy with its audit trail. If protected health information is involved, use a HIPAA workflow with a business associate agreement and apply the organization’s privacy and retention policies.
Who uses medical information requests
Healthcare providers
Healthcare providers can request records, treatment details, or supporting information from patients and authorized medical offices. A reusable signNow template keeps required fields consistent, while signer authentication and an audit trail document consent, completion, and delivery history.
Authorized reviewers
Insurance teams, employers, attorneys, and disability reviewers can request narrowly defined medical information from authorized parties. Role-based access, completed copies, and searchable audit records help separate sensitive requests from unrelated case documents.
Which organizations use this request
The form fits organizations that need documented authorization and additional medical details from a specific recipient for a defined purpose.
✓ A solo medical practice can send a defined request to another provider, collect authorization electronically, and retain the signed record with its audit history for later chart review. ✓ A regional healthcare organization can standardize requests across departments using shared templates, delegated sending, and controlled access for protected health information. ✓ An insurer or disability administrator can route medical-information requests to authorized recipients, track completion, and preserve evidence without exchanging unnecessary paper records.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Features for medical information requests
signNow organizes the request from document preparation through authorization, signing, secure storage, and audit review for healthcare-related workflows.
Field placement
Upload the medical information request and place signature, date, initials, and text fields where the requester and authorizing signer must complete them.
Reusable templates
Create a reusable request template so staff use consistent language, authorization fields, and recipient roles for each medical-information workflow.
Remote signing
Send the prepared request by email or signing link, allowing the authorized recipient to review and complete it remotely.
Audit trail
Capture signer identity, timestamps, IP details, and document activity in an audit trail associated with the completed request.
Privacy controls
Protect sensitive medical information with encryption, access controls, and a HIPAA workflow that requires a business associate agreement.
Record storage
Store completed requests and their audit records together, supporting later review of authorization, completion, and document history.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Complete this medical request in signNow
Use the following sequence to prepare, authorize, send, and preserve this specific medical information request.
Upload form:
Upload the medical information request. Check fields:
Review detected fields and add missing authorization fields. Assign roles:
Assign the requester and authorized recipient. Send request:
Send the request by email or signing link. Store record:
Store the signed copy with its audit trail.
How the request audit trail works
The signNow audit trail records technical events around the medical information request, creating a reviewable history separate from the form’s visible answers.
Authenticate signer:
Timestamp actions:
Hash document:
Seal record:
Link events:
Export evidence:
Security for medical information requests
HIPAA safeguards:
Stored encryption:
Transfer encryption:
SOC 2 Type II:
ISO 27001:
Signing records:
Mobile options for medical requests
signNow supports medical information request workflows through its mobile apps on iOS and Android. Use a device camera to capture a paper request, then prepare fields and signing steps in signNow.
iOS app iOS app Android app Android app Offline signing Offline signing
Mobile access helps authorized staff collect signatures during patient or provider interactions without moving sensitive paperwork between offices. Confirm device management, screen-lock, application access, and retention policies with your privacy and security teams before handling protected health information.



Privacy pitfalls in medical requests
Including more medical information than the stated purpose requires can increase privacy exposure and conflict with minimum-necessary handling expectations. Sending a request without documenting the signer’s authorization can make the recipient’s disclosure basis unclear during later review. Granting broad staff access to completed requests can expose protected health information beyond the personnel assigned to the case. Using an unverified email address can disclose a medical request to the wrong recipient before identity checks occur.
Best practices for this medical request
Use precise authorization language, verify fields and recipients, and preserve the signed request with its supporting audit evidence.
Limit the request to its purpose
Review every required field
Preserve the audit evidence
Confirm the HIPAA agreement
Legal standing of the signed request
A signed medical information request can provide evidence of intent, consent, signer attribution, and the requested disclosure scope when those elements are properly documented. ESIGN and UETA generally recognize qualifying electronic signatures and records, while HIPAA obligations still govern protected health information. Wills, court orders, and certain family-law documents remain outside these general electronic-signature rules.

Medical information request troubleshooting
Resolve field, signer, privacy, and retention issues before sending additional medical information requests through signNow.
Upload the original request again and check whether the PDF is password protected, scanned, or missing a selectable text layer. signNow can place fields after upload, but staff should review every detected field before sending a medical-information request.
Use signNow’s SMS authentication or another configured signer-verification method, then confirm the recipient’s identity before disclosure. HIPAA compliance requires a business associate agreement where applicable, but the agreement does not replace authorization or minimum-necessary review.
A completed e-signature can satisfy ESIGN and UETA when intent, consent, attribution, and record retention are established. Consumer-facing healthcare records also require the electronic-record disclosure and access conditions described in 15 U.S.C. §7001(c).
Review the signNow plan before sending. Business includes templates, audit trails, and mobile apps; Business Premium adds bulk send; Enterprise adds advanced signer authentication. The Site License lists HIPAA and 21 CFR Part 11 as add-ons.
If the request contains protected health information, restrict document access, use the required BAA, and retain the record according to the applicable policy. HIPAA’s federal documentation retention rule is six years from creation or last effective date under 45 CFR §164.530(j).
Check the recipient email, signer order, required fields, and authentication settings before resending. Keep the original audit trail, document the correction, and avoid sending medical information to an address that has not been independently confirmed.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.