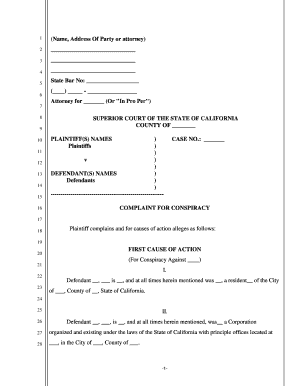
Complaint For Conspiracy Form
Use a COMPLAINT FOR CONSPIRACY template to make your document workflow more streamlined.
What the complaint for conspiracy form does
The Complaint For Conspiracy Form records allegations that two or more parties coordinated to pursue an unlawful objective or cause an actionable injury. It is not a universal federal filing with one standardized layout, deadline, or issuing agency; required allegations and signature rules depend on the court, jurisdiction, and underlying claim. A filer generally identifies the parties, states the agreement and overt acts, explains the resulting harm, and specifies requested relief. signNow can upload the prepared document, detect fields, collect signatures, and preserve an audit trail, but it does not determine legal sufficiency or filing venue.
Who uses this complaint form
Solo legal practice
A solo attorney can prepare allegations, identify respondents, and route the complaint for client or co-counsel signatures while preserving a connected audit trail.
Litigation department
A litigation department can use a controlled template to collect multiple signatures, maintain role-based access, and store the completed complaint with supporting records.
Complete the complaint for conspiracy form
Prepare the allegations and signature requirements before sending this legal document through signNow.
Upload the form:
Upload the completed complaint and verify every allegation, party name, and requested remedy. Check detected fields:
Use auto-detection to place signature, date, and initials fields accurately. Assign signers:
Add each required signer in the order established by the complaint. Complete and store:
Send the complaint, collect signatures, and download the completed record.
Recommended complaint workflow setup
Configure the complaint workflow around verified signer identity, document integrity, controlled access, and the retention rule governing the matter.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Electronic signature with signer intent |
| Audit trail | Enable completion certificate and history |
| Document retention | Apply the governing state-law schedule |
| Encryption | TLS 1.2/1.3 and AES-256 |
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
How signNow records the complaint audit trail
The audit trail connects signer activity and document history, giving the completed complaint a reviewable record of execution.
Authenticate signer:
Capture timestamps:
Hash document:
Seal record:
Record actions:
Export audit trail:
Preserve complaint records and audit evidence
Retention depends on the record’s legal and business context, so pair the signed complaint with its audit evidence and governing rule.
Identify the applicable retention rule
Export the audit trail with signatures
Archive the complaint securely
Document the disposal decision
Legal standing and electronic signatures
An electronically signed complaint may be admissible when the signer’s intent, consent, attribution, and reliable record retention can be shown under ESIGN and applicable state law, including UETA or New York ESRA. Court orders, official court filings, wills, and family-law decrees fall within ESIGN exceptions and may require court-specific procedures.

Risks requiring legal review
Missing signer intent
Unclear signer identity
Altered complaint
Incomplete audit trail
Protect complaint disclosures and consent
Personal addresses, contact details, or allegations may be exposed when a completed complaint is sent to unintended recipients or stored without access restrictions. A signer may complete the document without clear electronic-consent language, creating questions about whether the person intended to sign this complaint electronically. Shared links can be forwarded beyond the intended parties, allowing an unauthorized person to access allegations or sign without appropriate identity controls. Separating the signed complaint from its audit trail can make later review difficult because timestamps, authentication events, and document history are no longer connected.
Security controls for complaint records
TLS 1.2/1.3 protects transit:
AES-256 protects stored data:
SOC 2 Type II certified:
ISO 27001 certified:
ESIGN and UETA compliant:
HIPAA compliant with BAA:
Platform requirements for completing the complaint
Complete the Complaint For Conspiracy Form in Chrome, Firefox, Safari, or Edge on Windows or macOS. signNow also provides mobile apps for iOS and Android, allowing authorized users to review and sign the complaint from supported phones or tablets.
Browser support Chrome, Firefox, Safari, and Edge Desktop systems Windows and macOS desktops Mobile access iOS and Android mobile apps
Organizations handling sensitive allegations should use managed devices, role-based access, and approved storage policies. Teams can connect signNow through its API or named integrations, including Microsoft 365, Google Drive, Box, Egnyte, Salesforce, and NetSuite, where their document-control procedures permit it.



Complaint form troubleshooting questions
These answers address document preparation, electronic signatures, court procedures, plan capabilities, and preservation of the completed complaint.
Upload the prepared complaint as a PDF, then review signNow’s detected fields. Auto-detection can place fields, but counsel should confirm every signature, date, and initials field matches the court or matter requirements before sending.
Business includes legally binding eSignatures, templates, and audit trails at $8 per user per month when billed annually. Confirm that the complaint’s signer count and workflow fit the selected plan before sending.
Business Premium adds bulk send at $15 per user per month billed annually. It may help when substantially identical complaints require separate signer groups, but each complaint still requires accurate party-specific information.
signNow is ESIGN and UETA compliant, but compliance does not establish that a particular court accepts electronic filing or signatures. Verify the court’s local rules and any required filing portal or notarization.
Use signNow authentication options such as email verification or SMS OTP, and preserve the completion certificate. Stronger authentication helps attribution, but it does not replace legal advice about identity or service.
Export the signed complaint and audit trail together, restrict access, and apply the matter’s governing retention rule. If PHI is involved, HIPAA compliance requires a BAA and six-year retention under 45 CFR §164.530(j).
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.