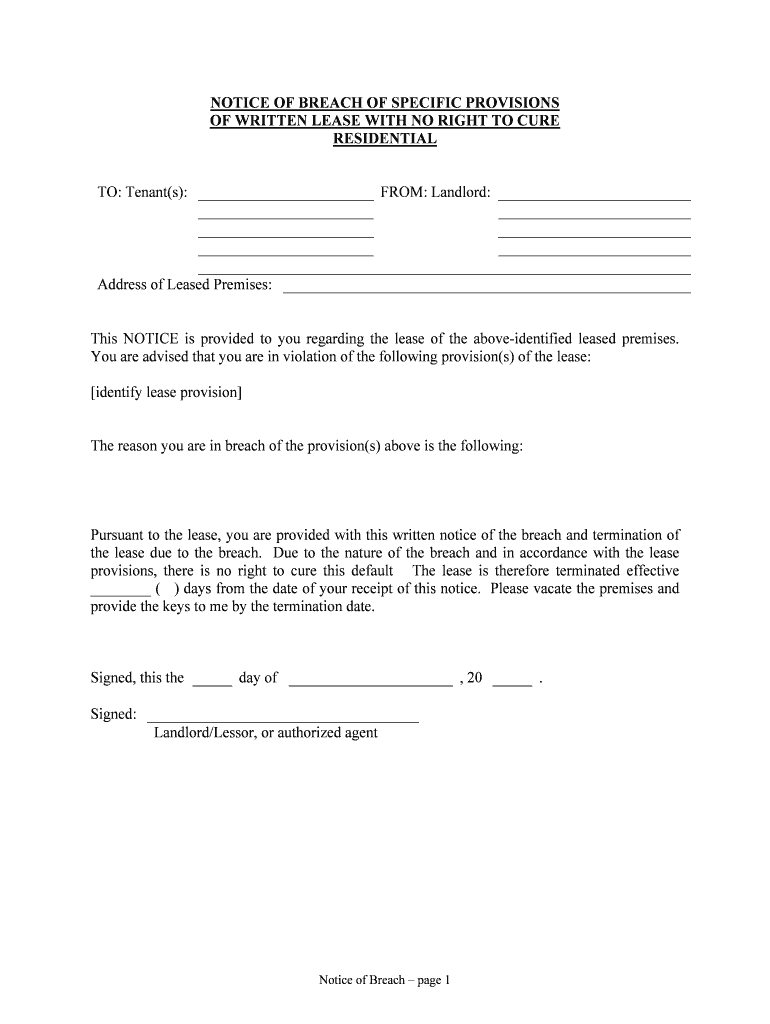
Notice Of Breach Page 1 Form
Use a Notice Of Breach Page 1 template to make your document workflow more streamlined.
What Notice Of Breach Page 1 Form does
Notice Of Breach Page 1 Form is a document used to communicate a specific breach notice and capture the recipient’s review or acknowledgment. In signNow, upload the form, let the platform detect fillable areas, check the notice details, assign recipients, and send it for electronic signature or acknowledgment. The completed PDF can be stored with its audit trail, which records signing activity and completion details. Legal sufficiency depends on the incident, applicable federal or state privacy law, required disclosures, recipient identity, and any consent needed for electronic records under ESIGN or UETA.
Features for Notice Of Breach Page 1 Form
signNow connects preparation, recipient routing, signing evidence, and controlled storage for teams handling Notice Of Breach Page 1 Form.
Field detection
Upload the Notice Of Breach Page 1 Form and inspect detected fields before adding recipients, reducing manual preparation while keeping the notice text under human review.
Recipient routing
Assign signature, acknowledgment, and date fields to named recipients so each person sees only the actions intended for that Notice Of Breach Page 1 Form.
Signing links
Send individual invitations or use a signing link when the approved distribution method requires flexible access to the breach notice.
Audit trail
Capture timestamps, signer actions, and completion details in an audit trail that stays associated with the executed notice.
Access controls
Use role-based access and connected storage to limit exposure of sensitive breach information after the form is completed.
Mobile signing
Review and sign from supported desktop browsers or signNow mobile apps when incident-response work occurs away from a central office.
Complete Notice Of Breach Page 1 Form
Prepare the notice in signNow, verify every required entry, obtain signatures, and preserve the completed record with its audit trail.
Upload form:
Upload the Notice Of Breach Page 1 Form PDF. Check fields:
Review detected fields and add missing recipient fields. Send document:
Send the notice to each designated signer. Archive record:
Store the signed copy with its audit trail.
Choose a signing method for this notice
- Use the signNow web app when preparing Notice Of Breach Page 1 Form on a desktop, placing fields, reviewing recipients, and sending the completed document by email.
- Use the signNow mobile app when collecting or reviewing Notice Of Breach Page 1 Form signatures from a phone or tablet during field or office work.
- Use kiosk mode when a staff member supervises signing on a shared device, such as an intake desk handling a Notice Of Breach Page 1 Form.
- Use a shareable signing link when multiple intended recipients need convenient access without creating separate email invitations for each Notice Of Breach Page 1 Form signer.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Platform requirements for this form
Notice Of Breach Page 1 Form can be prepared in Chrome, Firefox, Safari, or Edge on Windows 11 and macOS. Signers can review the document through supported desktop browsers or signNow mobile apps on iOS and Android, provided the device has a current internet connection when the signing session begins.
Browser support Chrome, Firefox, Safari, and Edge Operating systems Windows 11, macOS, iOS, and Android Access options Desktop browsers and signNow mobile apps
Organizations handling sensitive breach information should use managed Windows 11, macOS, iOS, or Android devices, apply current security updates, and restrict downloaded copies. Teams can connect signNow with identity, storage, and workflow systems, while administrators should configure access, authentication, and retention according to the applicable state privacy law and internal incident-response policy.
Recommended setup for this notice
Configure Notice Of Breach Page 1 Form around recipient identity, signing evidence, protected information, and controlled access.
| Setting | Recommendation |
|---|---|
| Authentication method | Email invitation with SMS verification |
| Signature type | Typed or drawn electronic signature |
| Audit trail and encryption | Audit trail with TLS and AES-256 |
| Document retention | Six years for PHI records under 45 CFR §164.530(j) |
| User provisioning | Role-based access for incident-response staff |



Best practices for breach notice records
Preserve the exact notice, signing evidence, recipient access, and retention decision so the completed record remains understandable and defensible.
Apply the retention rule matching the record
Export the audit trail with the notice
Restrict access to breach records
Document disposal and exceptions
Privacy pitfalls when sending breach notices
Including unnecessary names, account details, or medical information can expose personal data beyond the recipients who need the notice. Sending the completed notice before capturing required consent or acknowledgment can weaken evidence that the recipient reviewed the disclosure. Granting broad template or download access can let unauthorized users view breach details or create inaccurate copies. Failing to preserve the signed document and audit trail can make it harder to demonstrate delivery, timing, and signer identity.
Risks of mishandling breach notices
Electronic delivery questioned
Unauthorized disclosure
Required information omitted
Evidence becomes weaker
How the audit trail records this notice
The audit trail documents the technical events connecting Notice Of Breach Page 1 Form access, review, signature, completion, and later evidence retrieval.
Authenticate signer:
Capture timestamp:
Hash document:
Seal record:
Log activity:
Export evidence:
Troubleshooting Notice Of Breach Page 1 Form
These answers address field preparation, signer access, privacy controls, evidence, and plan limits for Notice Of Breach Page 1 Form workflows.
Upload the Notice Of Breach Page 1 Form as a PDF, then use signNow’s field detection and manually verify every field before sending. The Business plan includes templates and audit trails, helping preserve the prepared version and signing history without changing the notice’s substantive language.
A recipient can usually sign through the email invitation or signing link without maintaining a signNow account. If stronger attribution is required, configure available authentication options, such as SMS verification, and preserve the resulting audit trail with the completed notice.
Business Premium includes bulk send, which can help distribute individually addressed notices at scale. Do not use bulk send to disclose another recipient’s information; review each recipient and document before release under the applicable privacy policy.
signNow provides audit trails, timestamps, document history, and completion records. Under ESIGN and UETA, enforceability still depends on intent, consent, attribution, and record retention; the platform does not determine whether a specific notice satisfies state law.
For consumer-facing electronic records, ESIGN 15 U.S.C. §7001(c) requires disclosure of paper-record rights, electronic access, and withdrawal procedures. Configure the notice workflow and disclosures to match the recipient relationship and applicable law before sending.
The Business plan is listed at $8 per user per month when billed annually and includes 100 signature invites per user per year. Overages may apply; Business Premium adds bulk send, while Enterprise adds advanced signer authentication.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.