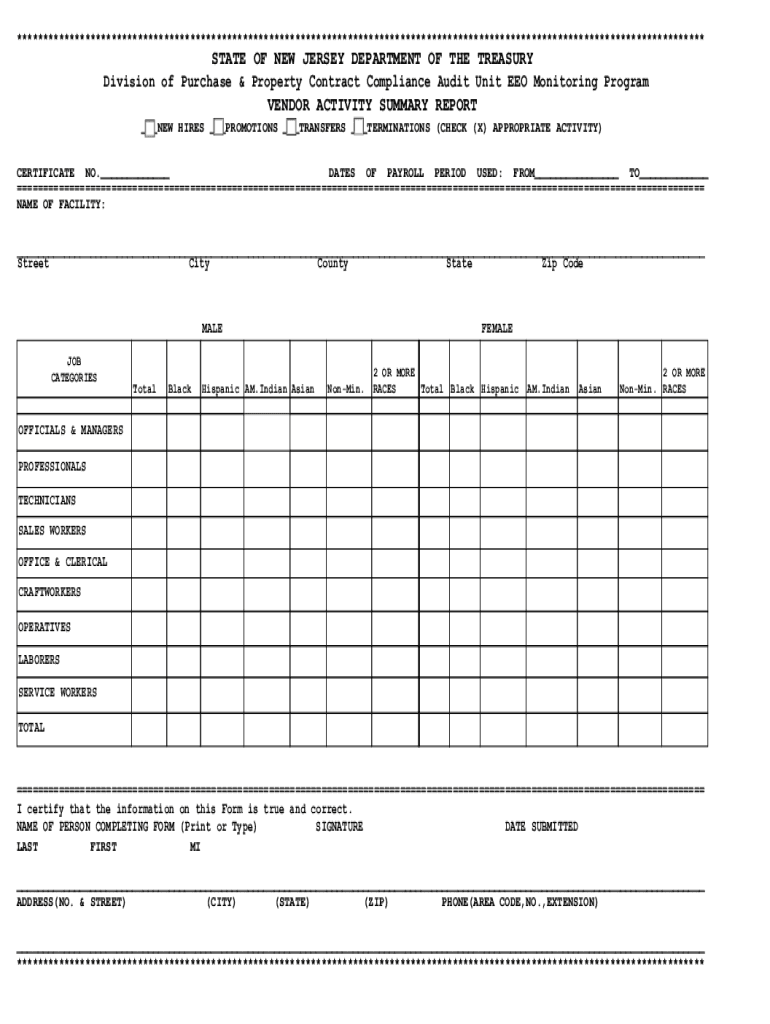
Vendor Activity Summary Report Forms
Get started with a Vendor Activity Summary Report Forms 0, complete it in a few clicks, and submit it securely.
Vendor Activity Summary Report Forms explained
Vendor Activity Summary Report Forms record what a vendor did, when the activity occurred, who reviewed it, and whether required approval was completed. Organizations usually adapt the report to their own vendor fields, status definitions, and retention policy because this name does not identify a single federally issued form. In signNow, upload the report template, review detected fields, add vendor-specific inputs and signature assignments, then send it for completion. The completed document and audit trail can be retained as evidence of the recorded workflow.
Who benefits from vendor activity reports
Vendor Activity Summary Report Forms help procurement, operations, and compliance teams document vendor activity consistently across U.S. business workflows.
Solo procurement consultants can use Vendor Activity Summary Report Forms to collect vendor names, activity dates, review notes, and approvals without maintaining paper files. Regional operations teams can standardize vendor reporting through reusable signNow templates, assigned approval fields, and audit trails that connect each completed report to its reviewers. Enterprise procurement departments can route reports across business units, control access, and retain signed activity records alongside vendor governance documentation.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Who uses vendor activity reports
Procurement teams
Procurement teams use Vendor Activity Summary Report Forms for vendor onboarding records, service reviews, approval histories, and contract-related documentation. They can upload a report template to signNow, assign fields to reviewers, and preserve the completed record with its audit trail for internal governance.
Operations and compliance
Operations and compliance groups use the form to document vendor activity across departments, including review dates, responsible contacts, status changes, and approval outcomes. Access controls, signer authentication, and audit-trail export help support controlled handling of sensitive business records.
Complete a vendor activity report
Use this sequence to prepare, route, sign, and retain a Vendor Activity Summary Report in signNow.
Upload template:
Upload the completed vendor report template to signNow. Check fields:
Review detected fields and add missing vendor details. Assign signers:
Assign approval and signature fields to recipients. Send report:
Send the report and monitor completion status.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended report workflow settings
Configure Vendor Activity Summary Report Forms around signer identity, evidentiary records, protected data, and your organization’s approved retention policy.
| Setting | Recommendation |
|---|---|
| Authentication method | SMS OTP with administrator-managed users |
| Signature type | Electronic signature with signer intent |
| Audit trail | Capture timestamps, IP addresses, and actions |
| Document retention | Apply the organization’s approved retention schedule |
| Encryption | AES-256 at rest and TLS 1.2/1.3 in transit |
How the vendor report audit trail works
A signNow audit trail connects the vendor report to signer identity, document events, integrity evidence, and later retrieval.
Authenticate signer:
Capture timestamp:
Hash document:
Seal record:
Log activity:
Export trail:
Security controls for vendor reports
Transport encryption:
Storage encryption:
Security certification:
Information security:
Health data controls:
Signer authentication:
Vendor report preparation challenges
Vendor names entered inconsistently can prevent reliable grouping, approval routing, and later reconciliation across Vendor Activity Summary Report Forms. Missing activity dates, status values, or approval fields can leave a report incomplete and weaken its usefulness for vendor oversight. Sending reports without assigned recipients may produce unsigned records that cannot demonstrate approval or confirm the responsible vendor contact. Storing signed reports outside controlled repositories can separate the document from its signNow audit trail and complicate later evidence review.
Risks of incomplete vendor reports
Missing approval history
Unclear signer identity
Inconsistent vendor fields
Uncontrolled report sharing
Legal standing of vendor activity reports
A completed Vendor Activity Summary Report may support business evidence when the signer intended to sign, consented to electronic records, can be attributed, and the record remains reproducible. ESIGN, 15 U.S.C. chapter 96, and UETA recognize qualifying electronic signatures, but they do not make every business record accurate or admissible automatically. Wills, certain court filings, family-law decrees, and other statutory exclusions remain outside that framework.

Troubleshooting vendor activity reports
Resolve field, authentication, plan, privacy, and electronic-signature questions before sending Vendor Activity Summary Report Forms through signNow.
signNow can accept a PDF or uploaded report template, but automatic field detection may miss custom vendor columns. Add signature, date, initials, and required text fields manually before sending.
The signNow Business plan includes templates and audit trails, while Business Premium adds bulk send. Select Business Premium when distributing the same vendor activity report to many recipients.
For consumer-facing vendor records, ESIGN requires disclosure of the right to receive paper records and access electronic copies. Capture consent before sending through signNow.
Use signNow SMS authentication or stronger signer authentication where identity risk warrants it. The audit trail records authentication events, timestamps, actions, and document history for review.
signNow supports TLS 1.2/1.3 in transit and AES-256 at rest. HIPAA workflows require a business associate agreement when vendor reports contain protected health information.
Electronic signatures generally receive legal recognition under ESIGN and UETA when intent, consent, attribution, and record reproducibility are established. Those laws do not determine the report’s business retention policy.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.