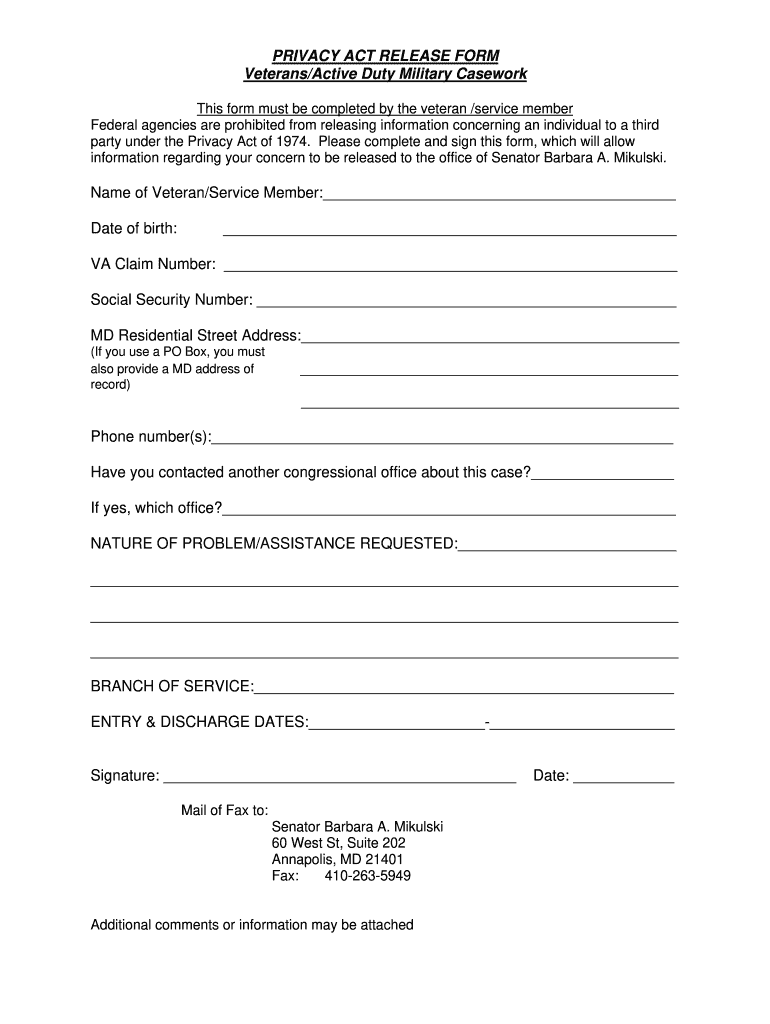
Barbara Mikulski Privacy Release Form
Use the Barbara Mikulski Privacy Release Form 0 template to simplify high-volume document management.
What the Barbara Mikulski Privacy Release Form does
The Barbara Mikulski Privacy Release Form is a written authorization allowing a constituent to permit congressional casework staff to request or discuss specified records with an agency or other organization. It identifies the constituent, describes the matter and authorized disclosure, and records the constituent’s signature and date. Staff should limit requests to the scope stated in the release and follow the receiving agency’s requirements. A completed electronic record may be signed through signNow when applicable law and the agency accept electronic signatures; ESIGN and UETA provide the relevant U.S. framework.
Users who rely on this release
Congressional casework staff use the release to document constituent authorization before contacting federal agencies about benefits, immigration, veterans’ services, or other matters. Staff can preserve the signed form and audit trail with the case file while limiting requests to the authorization’s stated scope and recipient. As Director of NetSuite Operations, Kodi-Marie Evans describes signNow’s role in getting the right signatures in the right formats through an integration workflow, a model relevant to structured case administration. Constituents completing sensitive casework authorizations can review the requested disclosure, sign from a desktop or mobile device, and receive a completed copy. The form is especially useful when a constituent cannot visit a congressional office, provided the receiving agency accepts the electronic record and the release meets its own requirements.
How this privacy release workflow works
The signNow workflow turns the Barbara Mikulski Privacy Release Form into a controlled electronic signing record.
Upload form: Upload the Barbara Mikulski Privacy Release Form to signNow. Check fields: Review detected fields and add constituent information. Send securely: Send the release to the authorized signer. Retain records: Store the signed release with its audit trail.
Steps to complete the privacy release
Use these steps to prepare, sign, and retain the Barbara Mikulski Privacy Release Form accurately.
Upload form:
Upload the completed release template. Check details:
Confirm the constituent and agency fields. Add signer:
Add the signer’s email address. Finish record:
Send, sign, and download the record.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
What the audit trail records
The audit trail links the constituent’s signing activity to the completed Barbara Mikulski Privacy Release Form and supports later review.
Authenticate signer:
Timestamp action:
Track activity:
Protect integrity:
Seal record:
Export evidence:
Processing stages for the privacy release
Processing depends on accurate case information and signer availability; the release is complete after the required signature is recorded.
Prepare the release
Deliver to signer
Complete signature
Archive the record
Risks of incomplete release execution
Narrow authorization
Privacy complaint
Weak audit record
Enforceability dispute
Privacy challenges in release processing
Leaving the authorized agency, record category, or case subject vague can cause staff to request information outside the constituent’s intended permission. Sending an unprotected signed PDF by ordinary email can expose personal information to recipients who were not approved for case access. Failing to capture the signer’s consent and signature date can make the release difficult to authenticate during an agency review. Allowing broad internal access to completed releases can disclose constituent information beyond staff assigned to the specific case.
Best practices for completing the release
Accurate scope, documented consent, controlled access, and reproducible records reduce disputes about the Barbara Mikulski Privacy Release Form.
Define the authorization scope
Capture signer intent
Limit record access
Preserve the case record
Recommended release workflow setup
Configure the Barbara Mikulski Privacy Release Form around verified signer identity, limited disclosure, audit evidence, and the office’s records policy.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Electronic signature with recorded intent |
| Audit trail | Capture timestamps, actions, and signer identity |
| Document retention | Follow the office records schedule |
| Encryption | TLS 1.2 or 1.3 in transit |
Security for privacy release records
Transport encryption:
Stored data encryption:
Security reporting:
Information security:
Privacy management:
Electronic signatures:
Key performance indicators that demonstrate SignNow's proven track record.
Troubleshooting the privacy release workflow
These answers address field setup, signature evidence, privacy scope, and signNow plan questions for this release form.
Upload the original PDF again and use signNow’s field editor to review detected fields. Confirm that the constituent’s name, agency, authorization scope, signature, and date fields are present before sending the Barbara Mikulski Privacy Release Form.
The Business plan includes legally binding eSignatures, templates, audit trails, and mobile apps at $8/user/month when billed annually. Business Premium is $15/user/month annually and adds bulk send and kiosk mode; choose based on the office’s workflow.
signNow states that its electronic-signature service is compliant with ESIGN and UETA. Those laws support electronic records when intent, consent, attribution, and retention requirements are met, but the receiving agency may impose additional acceptance rules.
Use signNow’s audit trail to preserve the signing event, timestamps, actions, and signer information with the completed form. If an agency requires a particular release format or wet signature, follow that agency’s instruction instead.
HIPAA applies when a workflow handles protected health information for a covered entity or business associate; a congressional release is not automatically a HIPAA record. If PHI is involved, confirm the office’s legal role, agency requirements, and BAA needs.
For a consumer-facing electronic record, ESIGN requires disclosure of the right to receive paper, access to the electronic format, and a method to withdraw consent under 15 U.S.C. §7001(c). Apply those requirements when the signer is a consumer.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.