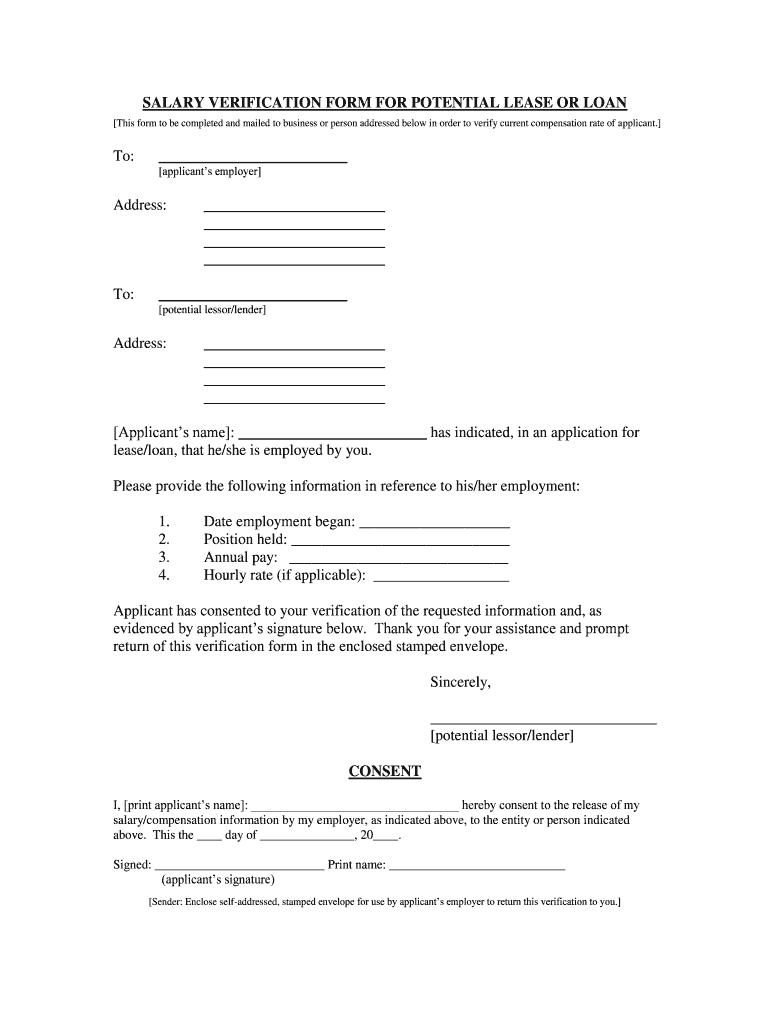
Applicant Has Consented To Your Verification Of The Requested Information And, As
Use a Applicant Has Consented To Your Verification Of The Requested Information And, As template to make your document workflow more streamlined.
What this applicant consent form does
Applicant Has Consented To Your Verification Of The Requested Information And, As is a written authorization allowing an applicant to permit verification of information identified in the form. The applicant reviews the requested information, confirms consent, and signs the authorization. The requesting organization then uses the completed record to support its stated verification process. With signNow, a sender uploads the form, reviews automatically detected fields, assigns applicant and verifier roles, and sends it for signature. The completed document and audit trail preserve the signing event, timestamps, and document history.
How this consent form works
The applicant reviews the requested verification, gives informed consent, signs electronically, and receives a record of the completed authorization.
Upload the form: Upload the applicant consent form and let signNow detect fillable fields automatically. Review fields: Review detected fields, then add applicant and verifier signature or date fields. Send for signature: Send the completed consent form to the applicant through email or a signing link. Store records: Store the signed authorization with its audit trail for later verification.
Complete this consent form online
Follow these steps to prepare the applicant’s authorization, collect signatures, and preserve the completed verification record.
Upload form:
Upload the Applicant Has Consented To Your Verification Of The Requested Information And, As form. Check fields:
Confirm names, consent language, signature fields, and verification details. Assign roles:
Assign the applicant and authorized recipient to required fields. Send document:
Send the authorization and monitor the signing status. Save evidence:
Download the signed form and retain its audit trail.
Features for applicant verification consent
signNow connects form preparation, applicant signing, routing, and record preservation in one workflow for verification authorizations.
Form preparation
Upload the exact consent document and preserve its wording while preparing applicant and verifier fields for completion.
Field detection
Automatically detected fields help identify signature, date, and text areas before the sender reviews the authorization.
Role assignment
Assigning roles keeps the applicant’s consent separate from the organization’s verification and recordkeeping responsibilities.
Remote signing
Email delivery and signing links let applicants review the authorization without requiring an in-person exchange.
Audit trail
Audit trails record signing actions, timestamps, and document history supporting later review of the authorization.
Reusable template
Templates help teams reuse an approved consent form without repeatedly rebuilding its fields and routing.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Security for consent records
Data encryption:
Electronic records:
Security assurance:
Information security:
Health information:
Signer authentication:
How the audit trail supports consent
The audit trail separates the applicant’s consent from the underlying verification and documents the events surrounding electronic execution.
Authenticate signer:
Capture timestamp:
Track document history:
Seal evidence:
Review activity:
Export trail:
Recommended consent workflow setup
Configure the Applicant Has Consented To Your Verification Of The Requested Information And, As workflow around signer identity, approved language, audit evidence, and applicable retention obligations.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Retain signed document and event history |
| Document retention | Follow the applicable federal and state rule |
| Encryption | TLS in transit and AES-256 at rest |



Consent and privacy pitfalls
The form may expose sensitive applicant information when copied into email or downloaded without access controls, increasing unauthorized-disclosure risk during verification review. Consent language that does not identify the requested information, recipient, or purpose can create uncertainty about whether the applicant authorized the specific verification. Sending the authorization to the wrong applicant or verifier can attach personal information to the wrong record and undermine attribution of the signed consent. A missing date, signature, or audit trail can make it harder to demonstrate when the applicant consented and which document version they reviewed.
Important exclusions and state rules
Notarization rules
Wills and codicils
Family law documents
Real-estate deeds
Best practices for this authorization
Accurate consent language, controlled access, and preserved signing evidence make the completed verification authorization easier to review.
Use approved consent language
Capture informed electronic consent
Restrict access by role
Preserve the completed record
Troubleshooting this consent workflow
Use these answers to resolve field, consent, security, and legal-scope questions before relying on the completed authorization.
Upload the original Applicant Has Consented To Your Verification Of The Requested Information And, As file again, then review signNow’s detected fields manually. Confirm that the applicant’s authorization language, signature field, and date field appear before sending the document.
The signNow Business plan includes templates and audit trails, while Business Premium adds bulk send. Select the plan based on whether this authorization is sent individually or to multiple applicants.
For consumer-facing electronic records, provide the disclosure required by 15 U.S.C. §7001(c), including paper-record rights and electronic-access procedures. signNow can preserve the disclosure and signing event, but your organization must supply compliant language.
If verification involves protected health information, confirm that your signNow arrangement includes the required BAA. HIPAA compliance does not replace your organization’s obligation to limit disclosure and retain the authorization appropriately.
Use signNow’s audit trail to review signer identity, timestamps, IP details, and document history. If a dispute concerns the authorization’s wording, compare the signed document with the approved template version.
ESIGN and UETA generally recognize electronic signatures when intent, consent, attribution, and record retention requirements are satisfied. Wills, family law decrees, certain court filings, and other statutory exclusions require separate handling.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.