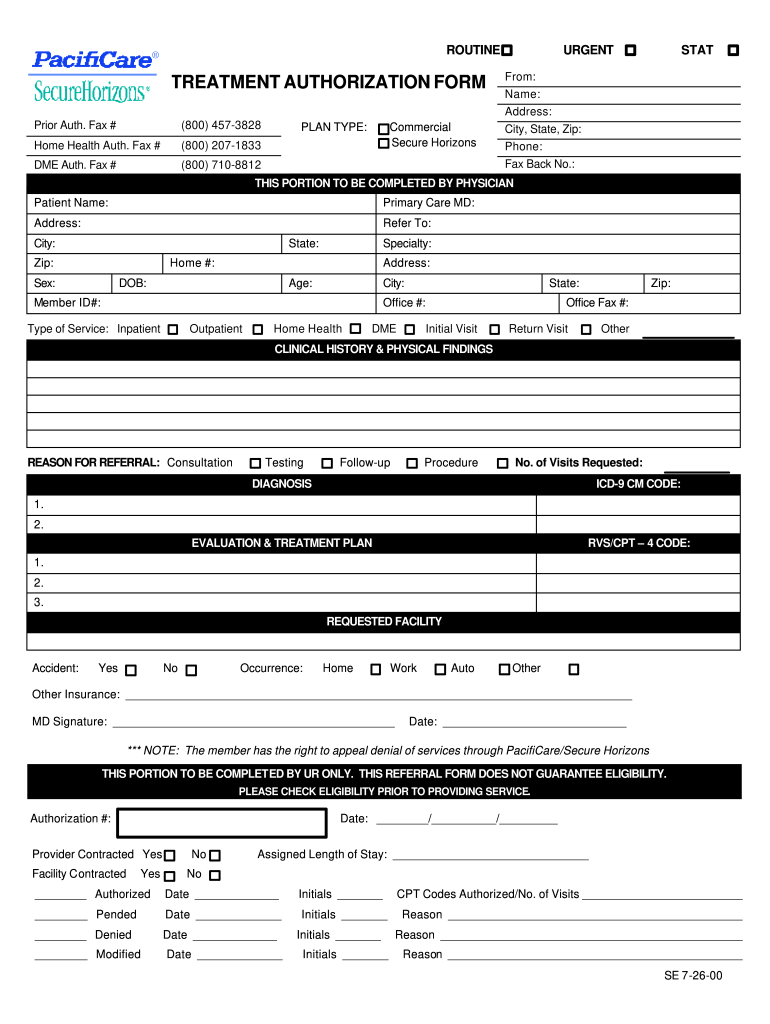
Pacificare Prior Authorization Form
Create a custom Pacificare Prior Authorization Form 2000 that meets your industry’s specifications.
What the Pacificare Prior Authorization Form does
The Pacificare Prior Authorization Form records a healthcare provider’s request for payer approval before a planned service, treatment, medication, or procedure. The requesting office supplies patient identifiers, clinical justification, provider information, requested service details, and supporting documentation required for review. The payer or utilization-management team evaluates the request and returns an approval, denial, or request for more information. With signNow, staff can upload the form, identify fillable fields, route it to authorized signers, and preserve the signed request with its audit trail. HIPAA obligations and payer-specific submission rules still apply.
Who uses the Pacificare Prior Authorization Form
Healthcare providers
Healthcare providers use the Pacificare Prior Authorization Form to request approval before delivering covered services, medications, or procedures. Staff can prepare clinical details, attach supporting records, route the request to authorized reviewers, and preserve the completed form for patient and payer records.
Review teams
Utilization review teams and payer-facing administrators use the form to coordinate clinical documentation, signatures, and status tracking. A controlled workflow helps separate patient information from unrelated records while keeping the authorization request available to people responsible for review and follow-up.
Users who manage Pacificare requests
A prior-authorization coordinator at a healthcare practice can upload the Pacificare form, complete provider and patient fields, route clinical approval signatures, and track whether the request is ready for payer review. The workflow keeps preparation, signing, and document history together for follow-up and recordkeeping. A utilization-management administrator can use controlled templates and delegated sending to manage recurring Pacificare requests across departments. Role-based access helps limit patient information to staff assigned to preparation, clinical review, authorization tracking, or records management.
How the authorization workflow works
Follow the Pacificare request from document preparation through authenticated signing and payer-ready record storage.
Upload documents: Upload the Pacificare form and supporting clinical documents. Complete fields: Review detected fields and add missing patient or provider details. Assign signers: Assign provider, patient, or reviewer signing responsibilities. Send request: Send the authorization packet and monitor completion status.
What the Pacificare audit trail records
The signNow audit trail preserves technical evidence around the Pacificare form’s signing events without replacing clinical review or payer authorization rules.
Authenticate signer:
Capture timestamp:
Track document history:
Seal record:
Connect events:
Retrieve audit trail:
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended authorization workflow setup
Configure the Pacificare Prior Authorization Form workflow around authenticated signers, protected health information, and a reproducible record of authorization activity.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Click-to-sign with signer intent |
| Audit trail | Capture timestamps, IP addresses, and actions |
| Document retention | Retain six years for HIPAA records |
| Encryption | TLS 1.2/1.3 and AES-256 at rest |
Key features for Pacificare authorization requests
signNow connects the Pacificare Prior Authorization Form’s clinical, signer, and recordkeeping steps in one auditable electronic workflow.
Field detection
Auto-detected fields help staff identify patient, provider, service, and signature areas after uploading the Pacificare Prior Authorization Form, reducing manual placement before the request is routed for review.
Role-based routing
Assigned roles keep provider signatures, patient acknowledgments, and reviewer actions connected to the correct Pacificare authorization request without sending unrelated clinical records.
Audit trail
The audit trail records signing events, timestamps, signer activity, and document history, creating a reviewable record for authorization administration and internal compliance checks.
Mobile signing
Mobile access lets authorized healthcare staff review and sign the Pacificare form from supported iOS and Android devices when the workflow permits remote completion.
Reusable templates
Templates preserve recurring Pacificare Prior Authorization Form fields and routing instructions, helping offices prepare repeated requests consistently without recreating the workflow each time.
Protected records
Encrypted storage and HIPAA compliance with a BAA help organizations protect patient information while managing completed authorization documents electronically.
Find and fill out the correct pacificare authorization form
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| *2000 PacifiCare SecureHorizons Treatment Authorization Form [2000-07-26] 2000 | 4.8 Satisfied (4190 Votes) |
Mobile options for Pacificare authorization
Use the signNow mobile app on iOS 16 or later or Android 10 or later to review the Pacificare Prior Authorization Form, capture supporting pages, and sign assigned fields.
iOS app iOS 16 or later with signNow mobile app Android app Android 10 or later with signNow mobile app Document capture Camera capture for supporting documents
Organizations handling protected health information should manage mobile access through approved devices, role-based permissions, and documented security policies. Confirm that each signer can access the required records and that the final authorization packet is retained according to the provider’s and payer’s applicable policies.
Security for authorization records
Data in transit:
Stored documents:
Health information:
Service controls:
Security management:
Electronic signatures:
Recordkeeping practices for Pacificare forms
Use a documented retention and review process so each completed Pacificare authorization remains accurate, accessible, and connected to its audit evidence.
Set retention against the applicable healthcare rule
Export the complete authorization record
Archive records with restricted access
Check clinical and signer completeness
Privacy pitfalls in Pacificare requests
Patient identifiers or clinical details may be exposed when the Pacificare form is emailed to unintended recipients or stored in unapproved locations. A missing consent or acknowledgement can leave the authorization record incomplete even when the provider’s signature is present. Overbroad permissions may allow staff without a care or authorization role to view protected health information. Unclear attachment handling can separate clinical justification from the Pacificare request, delaying payer review or creating an incomplete record.



Pacificare authorization troubleshooting
Resolve field, signer, security, plan, access, and retention questions before submitting a completed Pacificare Prior Authorization Form.
Upload the Pacificare Prior Authorization Form as a PDF, then review signNow’s detected fields before sending. Auto-detection does not replace a staff review: confirm patient identifiers, requested service details, provider information, attachments, and signature fields before routing the request.
Use signNow’s role assignments to separate provider, patient, and reviewer actions. The sender should verify each recipient’s email address and assigned fields, because an incorrect role can leave required clinical attestations or signatures incomplete.
For protected health information, use signNow with the required HIPAA configuration and a business associate agreement. HIPAA compliance does not replace minimum-necessary access controls, authorization procedures, or the healthcare organization’s own privacy policies.
The Business plan includes audit trails and templates, while Business Premium adds bulk send and kiosk mode. Select a plan based on the Pacificare request volume and signing method; verify whether advanced authentication or enterprise controls are required.
If a signer cannot open the request, confirm the email address, resend the invitation, or provide an approved signing link. SMS OTP can add verification when configured, but the organization should follow its patient identity and access procedures.
Export the completed Pacificare form and audit trail after signing, then retain them under the applicable healthcare records policy. HIPAA’s administrative-record rule requires six years from creation or the last effective date under 45 CFR 164.530(j).
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.