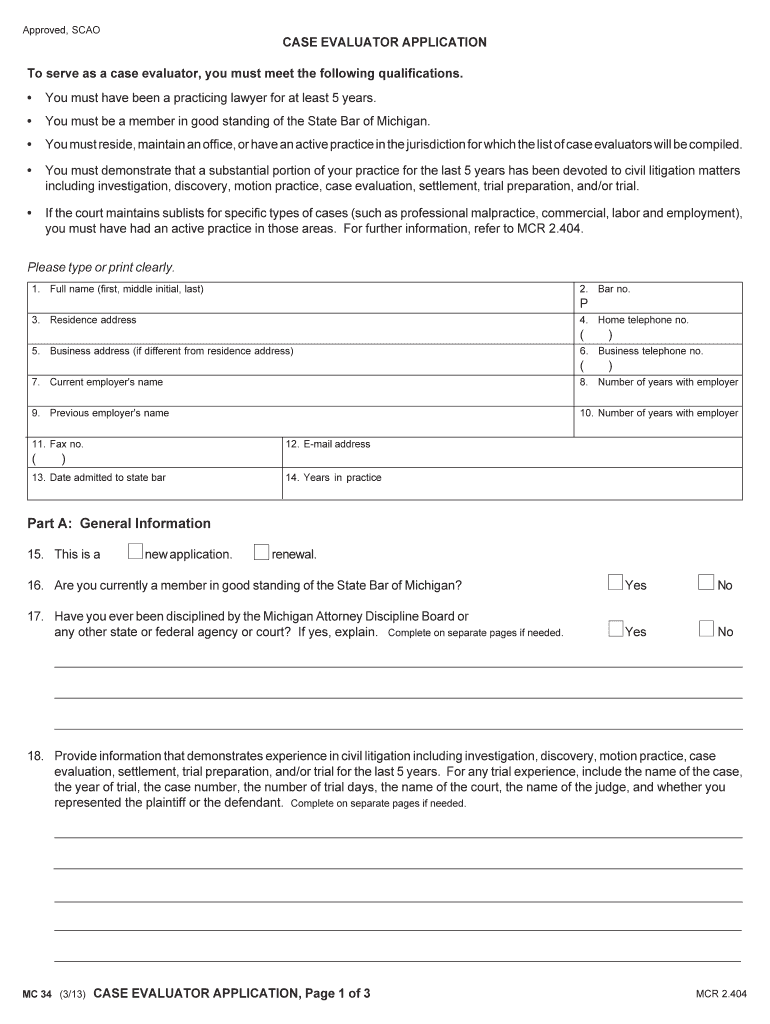
Case Evaluator Application Mc 34PDF Fpdf Docxmichigan Form
Use a Case Evaluator Application MC 34Pdf Fpdf Doc DocxMichigan template to make your document workflow more streamlined.
What this case evaluation application does
The Case Evaluator Application Mc 34PDF Fpdf Docxmichigan Form is an intake document for collecting information used to evaluate a potential legal matter. It can organize an applicant’s identity and contact details, event description, parties involved, supporting records, and requested follow-up. In signNow, a sender uploads the PDF, reviews or adds fillable fields, assigns applicant and reviewer roles, and sends the document for completion or signature. The finished application and audit trail can then be stored for controlled review. Legal staff should verify the form’s actual questions and Michigan-specific requirements before relying on it.
Who uses this case evaluation application
Legal intake
Legal professionals, intake coordinators, and prospective clients use this application to organize case information, contact details, incident facts, supporting documents, and authorization details before review. signNow can help route the completed application for signatures and preserve the executed record with an audit trail.
Review teams
Law offices and claims teams can use the application to collect consistent submissions from prospective clients, reduce missing information, and document consent. Reviewers should confirm every requested fact and attachment before relying on the completed form for case evaluation or representation decisions.
Complete the case evaluation application
Use this sequence to prepare the application, collect the required response, and preserve a reviewable signed record.
Upload form:
Upload the Case Evaluator Application PDF to signNow. Check fields:
Review detected fields and add missing response areas. Assign roles:
Assign applicant, reviewer, and signature responsibilities. Send application:
Send the application and monitor completion status. Archive record:
Store the signed PDF and audit trail securely.
How the audit trail records application activity
The audit trail separates the applicant’s answers from the technical evidence showing who accessed, signed, and completed the application.
Authenticate signer:
Timestamp actions:
Identify document:
Seal completion:
Record activity:
Export evidence:
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Platform requirements for this application
The application can be prepared and signed through signNow using Chrome, Firefox, Safari, or Edge on Windows and macOS. signNow also provides mobile applications for iOS and Android, allowing applicants and reviewers to access the document from supported mobile devices.
Browsers Chrome, Firefox, Safari, and Edge Desktop systems Windows and macOS desktop access Mobile access iOS and Android mobile applications
Organizations should manage access through approved devices, current browser releases, and role-based signNow permissions. Teams handling sensitive case information should also review authentication requirements, audit-trail access, retention rules, and any contractual or state privacy obligations before deploying the application across staff or external applicants.
Security controls for application records
Transport encryption:
Stored data:
Security reporting:
Information security:
Protected health information:
Electronic signatures:
Challenges when completing the application
Applicants may omit incident dates, opposing-party details, or supporting records, leaving reviewers without enough information to evaluate the submitted matter. A scanned PDF may contain labels without usable fields, requiring manual field placement before applicants can complete the application digitally. Sensitive narrative details and attachments can be disclosed to unintended recipients when signer roles, email addresses, or access permissions are assigned incorrectly. A signed application records acceptance of the document, but reviewers must independently validate factual statements, attachments, and any required Michigan-specific legal information.
Best practices for reliable case intake
A controlled template, clear signer roles, factual review, and documented retention make this application easier to evaluate consistently.
Preserve the application’s original question order
Assign applicant and reviewer roles separately
Validate answers before case evaluation
Archive the signed record securely
Rollout and retention for the application
A controlled rollout combines template testing, reviewer onboarding, signed-record export, and retention decisions based on the information this application contains.
Template preparation:
First application:
Team onboarding:
Signed record:
Tax records:
HIPAA records:
State policy:
Free trial:
Risks requiring document review
Incomplete consent
Missing attachments
Misrouted application
Deleted records



Troubleshooting the case evaluation application
Resolve field, authentication, consent, and enforceability questions before sending the completed application for signature.
If fields do not appear after upload, use signNow’s field-detection workflow and review every detected field manually. The Business plan includes templates and audit trails, but field recognition does not determine whether the application’s questions are legally sufficient. Confirm labels, required responses, and attachment areas before sending.
The Business plan provides legally binding eSignatures, templates, and audit trails at $8 per user per month when billed annually. If the application requires bulk sending to many prospective clients, Business Premium adds bulk send at $15 per user per month annually.
For consumer-facing electronic records, ESIGN requires disclosure of the right to receive paper records, access to the electronic format, and procedures for withdrawing consent under 15 U.S.C. §7001(c). Add the required disclosure before requesting a signature when this application is consumer-facing.
Use SMS authentication or another stronger method when the application contains sensitive incident, medical, or identifying information. signNow’s Enterprise plan adds advanced signer authentication, while HIPAA workflows require a business associate agreement when protected health information is involved.
A completed signature does not prove that every answer or attachment is accurate. Review the applicant’s responses, confirm supporting records, and preserve the signNow audit trail showing timestamps, signer activity, and document history before making a case-evaluation decision.
Electronic signatures generally receive legal recognition under ESIGN and applicable state law, including UETA in 49 states plus D.C., Puerto Rico, and the U.S. Virgin Islands. The application must still satisfy any separate state-law, notarization, licensing, or professional-practice requirements.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.