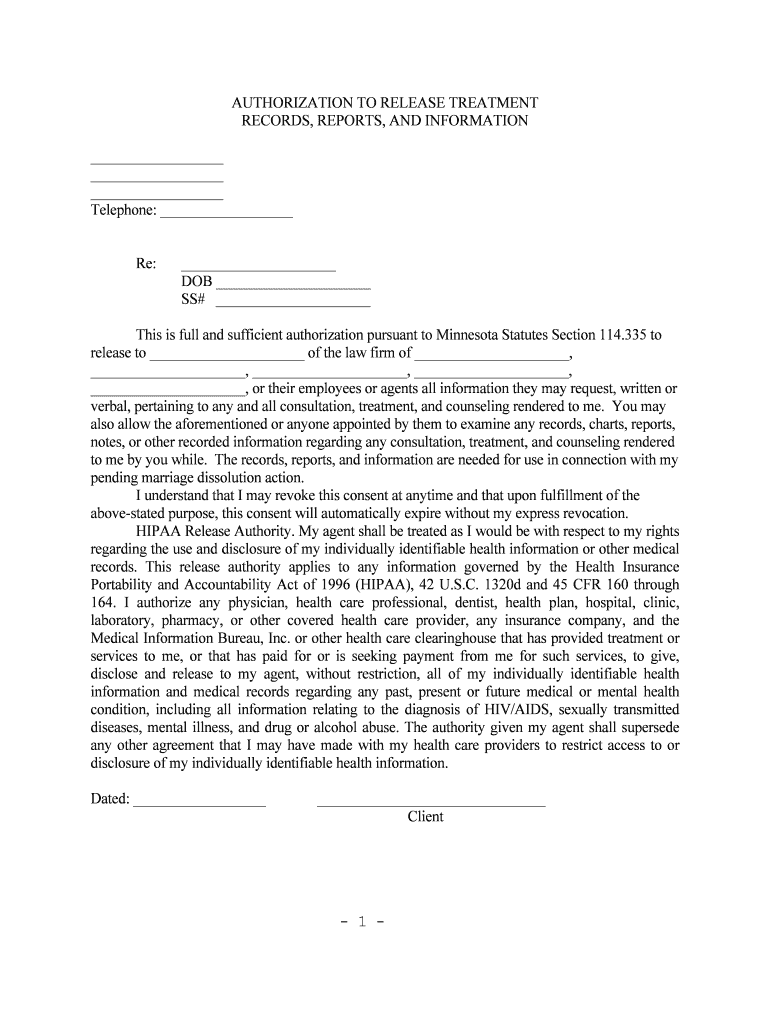
Medical Records Release Request I, Dob Ss# Form
Use a MEDICAL RECORDS RELEASE REQUEST I, DOB SS# template to make your document workflow more streamlined.
What this medical release request does
The Medical Records Release Request I, Dob Ss# Form is an authorization for a patient to identify themselves, specify which medical records may be disclosed, name the recipient, and approve the release. It commonly includes the patient’s name, date of birth, Social Security number, provider details, record categories, purpose, recipient, expiration, and signature. With signNow, the sender uploads the form, reviews detected fields, assigns signature fields, and sends it for completion. The signed PDF and audit trail preserve the authorization event for controlled disclosure and recordkeeping.
Who uses this medical release request
Patients and representatives
Patients use the request to authorize disclosure of defined medical records to a named provider, insurer, attorney, family member, or another recipient. The signer should review every record category, purpose, expiration term, and recipient before approving release.
Healthcare organizations
Healthcare organizations use the completed request to document authorization before releasing protected health information. Administrators can route forms to patients, collect signatures, preserve audit trails, and apply HIPAA access controls to the resulting record.
Businesses that use medical release requests
The form serves patients and healthcare teams wherever authorization must identify the records, recipient, purpose, and duration of disclosure.
Solo practitioners can send a patient-specific release request, collect authorization remotely, and retain the signed PDF without coordinating an in-person appointment. Healthcare clinics can route medical release requests to patients, standardize recipient and expiration fields, and preserve audit evidence alongside HIPAA-controlled records. Enterprise health systems can use shared templates, delegated sending, and role-based access for high-volume release workflows across departments and locations.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
How the medical release request works
The Medical Records Release Request I, Dob Ss# Form moves from patient identification to authorized disclosure through four documented signNow steps.
Upload the form: Upload the medical release request and review detected fields before completing patient and recipient details. Complete details: Enter the patient’s identifying information, requested records, recipient, and authorization details. Request signatures: Send the release request to the required signer through signNow’s email workflow. Store records: Collect the signed authorization and retain the completed PDF with its audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
How to complete the medical release request
Follow these steps to prepare, sign, and preserve the Medical Records Release Request I, Dob Ss# Form in signNow.
Upload form:
Upload the completed medical release PDF. Check fields:
Review detected fields and add missing ones. Assign signer:
Assign the patient as the signer. Complete request:
Send, collect the signature, and download records.
What the medical release audit trail records
The signNow audit trail documents the technical events surrounding the Medical Records Release Request I, Dob Ss# Form without replacing the authorization language itself.
Authenticate signer:
Capture timestamps:
Hash document:
Seal document:
Record activity:
Export evidence:
Recommended medical release workflow setup
Configure the Medical Records Release Request I, Dob Ss# Form around patient identity, protected health information, signer evidence, and controlled retention.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Patient electronic signature |
| Audit trail | Export completion certificate with signed PDF |
| Document retention | 6 years under HIPAA 45 CFR 164.530(j) |
| Encryption | TLS 1.2/1.3 and AES-256 protection |
Signer authentication and certificates
PKI certificates:
X.509 certificates:
Two-factor authentication:
SMS OTP:
ID verification:
Audit evidence:
Privacy pitfalls in medical release requests
Including a full Social Security number in an unrestricted copy can expose identity information beyond the medical disclosure purpose. A missing patient signature or date can leave the provider unable to confirm authorization for releasing the specified records. Naming a recipient broadly instead of specifically can create uncertainty about who may receive protected health information. Granting shared access to completed releases can expose dates of birth, treatment details, and authorization history to unauthorized staff.
Legal value of a signed medical release
A completed Medical Records Release Request I, Dob Ss# Form can document patient intent, consent, signer identity, and disclosure scope when electronic records satisfy ESIGN and applicable state UETA or New York ESRA requirements. Its audit trail supports evidentiary review, but wills, court orders, and family law decrees remain outside ESIGN’s general framework.

Record-keeping practices for medical releases
Use a documented retention and access process because this authorization contains identifying information and may permit disclosure of protected health information.
Apply the HIPAA six-year retention rule
Export the completed audit trail
Restrict sensitive patient information
Archive and dispose securely
Medical release request troubleshooting
Resolve field, signer, privacy, and retention questions before releasing records covered by the Medical Records Release Request I, Dob Ss# Form.
Upload the original PDF again and inspect detected fields before sending. signNow’s Business plan includes templates and audit trails, but field recognition still requires human review for patient identifiers and authorization language.
Confirm the recipient email address, signer role, and required fields before resending. signNow can send a corrected document, while the audit trail preserves the delivery and completion history for the Medical Records Release Request I, Dob Ss# Form.
Use SMS OTP or another available authentication control when the release contains a Social Security number or protected health information. HIPAA compliance requires a BAA with signNow and does not replace your own access policies.
Business Premium includes bulk send, while Business does not. For repeated medical release requests, use Business Premium only when its bulk-send workflow matches your authorization process and each patient receives the correct individualized form.
Electronic signatures generally receive legal recognition under ESIGN and applicable UETA rules when intent, consent, attribution, and record retention are established. Consumer-facing healthcare records also require the disclosures described in 15 U.S.C. §7001(c).
Export the signed PDF and completion certificate after signing, then restrict storage access. HIPAA-covered records require six-year retention from creation or the last effective date under 45 CFR §164.530(j), unless a longer rule applies.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.