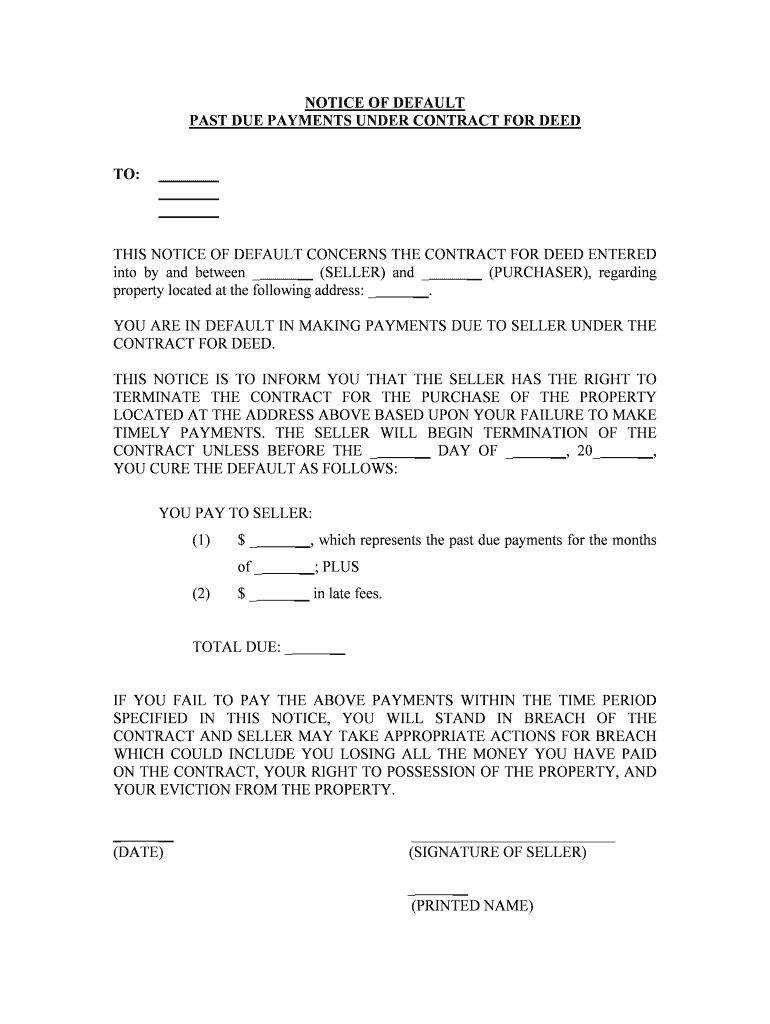
Contract And Seller May Take Appropriate Actions For Breach Form
Use a CONTRACT AND SELLER MAY TAKE APPROPRIATE ACTIONS FOR BREACH template to make your document workflow more streamlined.
What this breach form does
The Contract And Seller May Take Appropriate Actions For Breach Form documents a party’s response when the other party may have failed to perform a contract obligation. It organizes the agreement reference, alleged breach, supporting facts, requested cure or remedy, and authorized approvals into a reviewable record. Upload the form and relevant contract to signNow, place fields for responsible parties, send it for electronic signature, and retain the completed document with its audit trail. ESIGN and UETA generally recognize qualifying electronic signatures in U.S. transactions.
Who uses this breach form
Contract parties
Contract parties, sellers, and business counsel use this form to document breach-related rights, proposed remedies, and communication records before taking action. It supports organized review of the agreement, the alleged breach, notice language, and the requested response.
Business teams
Operations and legal teams use the form to preserve a consistent breach-response workflow, route it for approval, and retain signed records with a clear audit trail.
How the breach form works
The workflow moves from document preparation to authenticated review, signature collection, and preservation of the completed breach record.
Upload documents: Upload the breach form and underlying agreement. Prepare fields: Review detected fields and add signers. Request signatures: Send the form through an email invitation. Preserve evidence: Store the completed record and audit trail.
Complete the breach form in signNow
Use this sequence to prepare the contract-specific facts, obtain authorized signatures, and preserve the resulting evidence.
Upload:
Upload the form and governing agreement. Prepare:
Review detected fields and add missing fields. Route:
Assign each signer and set signing order. Send:
Send invitations and monitor completion. Store:
Download the signed form and audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Key features for breach-response forms
signNow organizes the breach form around accurate document preparation, accountable signing, and evidence preservation rather than informal email exchanges.
Structured fields
Upload the breach form and source agreement, then place signature, date, initials, and text fields where each party must review or approve the document.
Signer routing
Send the completed form to identified parties in sequence or parallel, reducing uncertainty about who must review the alleged breach and proposed response.
Audit trail
Capture timestamps, IP information, and signer actions in an audit trail that remains associated with the completed electronic record.
Reusable templates
Use templates for recurring breach notices while preserving matter-specific facts, agreement references, cure terms, and authorized signers for each transaction.
Mobile access
Give recipients a browser-based signing experience and support mobile signing when parties need to review the form away from the office.
Record preservation
Store the executed form with its completion evidence so legal and operations teams can retrieve the record during contract administration or dispute review.
Recommended breach-form workflow setup
Configure the breach-response document for authenticated signing, traceable review, controlled access, and retention aligned with the governing contract and applicable law.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Capture timestamps, IP address, and actions |
| Document retention | Retain signed record and audit trail per policy |
| Encryption | TLS 1.2/1.3 in transit and AES-256 at rest |



Security for signed breach records
Data in transit:
Data at rest:
Security reporting:
Information security:
U.S. eSignature:
Protected health data:
Best practices for breach documentation
Complete the form from the governing agreement, preserve supporting evidence, and separate documented facts from proposed remedies.
Identify the breached obligation
Match remedies to the contract
Attach supporting evidence
Preserve the signed record
Inside the breach-form audit trail
The audit trail records the technical events that connect the signed breach form to its signers, timeline, document history, and completed record.
Authenticate signer:
Timestamp actions:
Hash document:
Seal record:
Track activity:
Export evidence:
State rules and document exclusions
State execution rules
Wills and codicils
Family law documents
Real-estate deeds
Legal standing and evidentiary value
A completed breach form may support a U.S. business record when the parties demonstrate intent, consent, signer attribution, and reliable retention and reproduction. ESIGN, 15 U.S.C. chapter 96, and UETA generally recognize electronic signatures, but wills, certain court filings, and family-law decrees remain excluded from ESIGN’s coverage.

Troubleshooting the breach-form workflow
Resolve field-detection, signer-authentication, legal-validity, retention, and document-scope questions before distributing the completed form.
Upload the original PDF again and allow signNow to process it before placing fields manually. If text remains unavailable, use positioned text, date, checkbox, and signature fields rather than altering the source agreement. Review the final rendering before sending.
A Business plan includes legally binding eSignatures, templates, and audit trails. Business Premium adds bulk send, kiosk mode, request payments, and quick invite links. Select the plan according to the number of recipients and workflow features required.
For U.S. transactions, ESIGN and applicable state law generally recognize electronic signatures when intent, consent, attribution, and record reproduction are established. Consumer-facing transactions also require the disclosures in 15 U.S.C. §7001(c).
Use signNow’s audit trail to preserve signer identity details, timestamps, IP information, and action history. Keep the completed breach form, source agreement, and audit trail together so the record can be reproduced during a dispute.
If the breach form contains protected health information, configure a HIPAA-compliant workflow and obtain the required business associate agreement. HIPAA’s retention rule is six years from creation or the last effective date under 45 CFR §164.530(j).
Do not use this electronic workflow for wills, codicils, testamentary trusts, court orders, or family-law decrees where ESIGN exceptions apply. Confirm state requirements before relying on electronic execution for notarized documents or deeds.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.