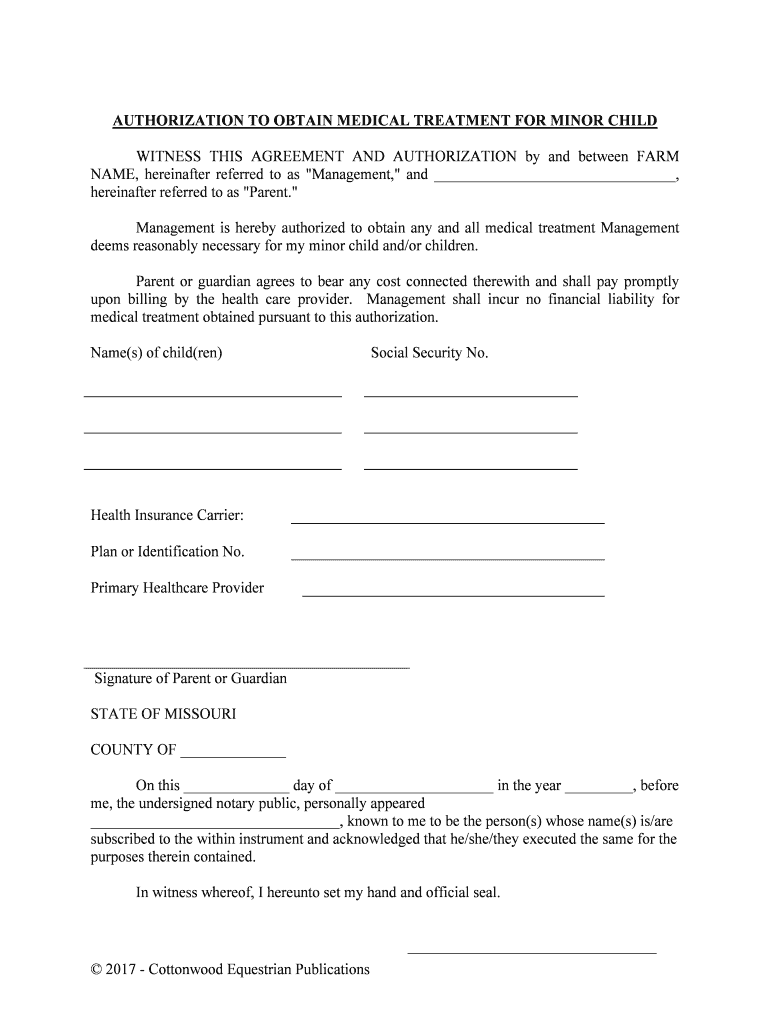
Medical Treatment Obtained Pursuant To This Authorization Form
Use a Medical Treatment Obtained Pursuant To This Authorization template to make your document workflow more streamlined.
What this medical authorization form does
The Medical Treatment Obtained Pursuant To This Authorization Form gives a designated person or organization permission to obtain specified medical treatment or related records for the individual named in the authorization. The signer identifies the patient, authorized recipient, requested treatment or information, purpose, and applicable limits. A healthcare provider may rely on the completed form only within its stated scope and subject to applicable federal and state privacy rules. If protected health information is involved, HIPAA requirements and the provider’s procedures still apply. Keep the signed form and audit trail together.
Organizations using this authorization
The form serves healthcare workflows where a patient’s permission, a defined recipient, and controlled treatment information access must be documented.
Solo medical practices can use a reusable authorization template to capture a patient’s designated recipient, treatment scope, purpose, signature, and date without coordinating paper exchanges. Healthcare groups can route authorizations through role-based staff, apply HIPAA controls, and retain signed records with audit trails for release, care coordination, or approved administrative purposes. Enterprise provider networks can connect signNow with systems such as Salesforce, NetSuite, Google Drive, or Microsoft 365 while central administrators manage permissions and retention policies.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Complete the authorization form online
Use signNow to prepare the medical authorization, capture the required signature, and preserve the completed record.
Upload form:
Upload the authorization form and confirm every patient, provider, and records field. Check fields:
Review detected fields and add missing signature, date, and authorization details. Add signer:
Enter the authorized recipient’s email address and select the required signing order. Store records:
Send the completed authorization, then download the signed copy and audit trail.
How the authorization audit trail works
The audit trail records technical evidence around this authorization, helping show who accessed, completed, and signed the document.
Authenticate signer:
Capture timestamps:
Hash document:
Seal record:
Track actions:
Retrieve evidence:
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended authorization workflow setup
Use controlled authentication, a complete audit trail, and retention aligned with the records handled under this authorization.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Capture timestamps, IP address, and signer actions |
| Document retention | 6 years for HIPAA records (45 CFR 164.530(j)) |
| Encryption | TLS 1.2 or 1.3 in transit and AES-256 at rest |



Platform requirements for signing
Open the Medical Treatment Obtained Pursuant To This Authorization Form in Chrome, Firefox, Safari, or Edge on Windows or macOS. signNow mobile apps support iOS and Android, allowing authorized users to review and sign from a supported mobile device. Use a secure TLS connection when handling patient information.
Browsers Chrome, Firefox, Safari, and Edge Desktop systems Windows and macOS desktops Mobile access iOS and Android mobile apps
Organizations handling protected health information should manage devices, user permissions, and signNow access centrally. Confirm that the workflow includes the required BAA, appropriate authentication, audit-trail access, and retention controls. API or SSO deployment may require a plan with the relevant capability, such as Site License or Enterprise features.
Security for medical authorizations
HIPAA protection:
Data in transit:
Stored data:
Security assurance:
Security management:
Regulated records:
Privacy and disclosure pitfalls
Including unrelated treatment details can disclose more protected health information than the stated authorization purpose requires. Leaving the authorized recipient, purpose, or expiration information unclear can delay provider review or narrow the authorization’s usable scope. Sending the completed form to an unverified email address can expose patient information outside the intended recipient’s control. Failing to retain the signed form and audit trail can make it difficult to demonstrate consent, scope, and signer attribution later.
Retention periods for authorization records
Choose the retention period based on the record’s actual purpose, the presence of PHI, and applicable federal and state requirements.
Six years for HIPAA records
Three years for tax records
Six years for major understatement
Indefinite for fraud cases
Longer period under state law
Best practices for retaining authorizations
Retention should preserve the authorization’s scope, signer evidence, and privacy controls throughout the record’s required life.
Keep the signed form with evidence
Export the audit trail promptly
Restrict access to PHI
Match disclosure to stated purpose
Key performance indicators that demonstrate SignNow's proven track record.
Troubleshooting authorization workflows
These answers address field detection, signer access, HIPAA handling, plan features, legal validity, and retrieval of completed authorization records.
On signNow’s Business plan, upload the Medical Treatment Obtained Pursuant To This Authorization Form as a PDF and use fields for the patient, authorized recipient, scope, purpose, signature, and date. If auto-detection misses a field, add it manually before sending.
The Business plan includes legally binding eSignatures and audit trails. For patient-facing records, signNow lists HIPAA compliance as available with a BAA requirement. Confirm that the organization has executed the BAA and configured access controls before processing PHI.
A signer can often open the request without a signNow account, depending on the sender’s workflow. If identity assurance is required, use SMS OTP or an Enterprise authentication option, then verify the signer’s identity before accepting the authorization.
Business Premium is the signNow plan that includes bulk send. Use it only when the same authorization template is sent to multiple recipients with appropriate individualized patient and scope information; never reuse another patient’s completed data.
Electronic signatures generally receive legal recognition under ESIGN, 15 U.S.C. ch. 96, and UETA, but the authorization must show intent, consent, attribution, and record reproducibility. State healthcare rules, provider policy, and HIPAA obligations may impose additional requirements.
If a completed form cannot be located, search the signNow document history and export the audit trail with the signed PDF. Retain both together, restrict access to authorized personnel, and apply the organization’s HIPAA retention policy where applicable.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.