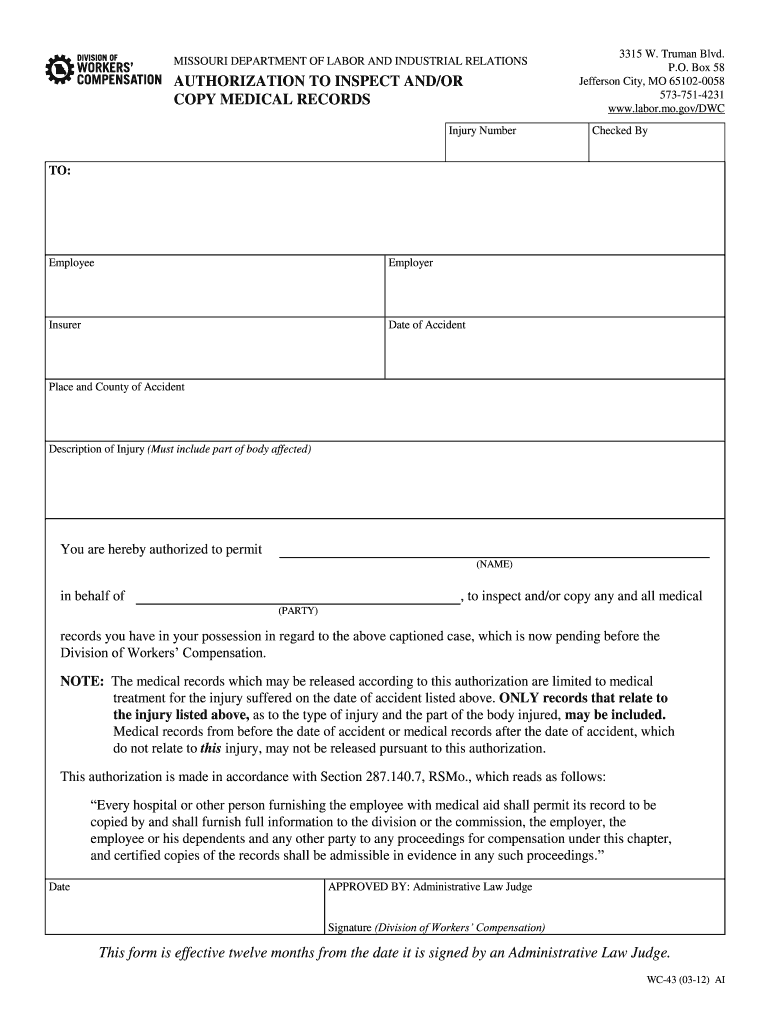
Authorization To Inspect Andor Copy Medical Records Form
Use a Authorization To Inspect Andor Copy Medical Records template to make your document workflow more streamlined.
What this medical records authorization does
The Authorization To Inspect Andor Copy Medical Records Form gives a named person or organization permission to inspect or obtain specified medical records. It identifies the patient, authorized recipient, records covered, purpose, expiration, and required signatures. The healthcare provider uses those limits when responding to a request. A completed electronic version can be signed through signNow when the parties consent and applicable law permits electronic records. HIPAA authorization requirements under 45 CFR 164.508 and state privacy rules still govern the disclosure; signing software does not replace them.
Organizations using medical authorizations
Medical practices, records departments, and health systems use this authorization to document permission for defined inspection or copying of medical records.
A solo medical practice can send a patient authorization for inspection or copying, capture the patient’s signature, and retain the completed record with an audit trail without coordinating paper exchanges across the office and records department. A regional healthcare provider can standardize authorization templates, assign administrative roles, and route requests to records staff while limiting access to protected health information through controlled signNow workspaces and documented procedures. An enterprise health system can connect authorization workflows to systems such as Microsoft 365, Salesforce, or cloud storage, while administrators manage provisioning, delegated sending, templates, and HIPAA-related controls across locations.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Key features for medical authorizations
signNow supports the document-specific workflow from uploading this authorization through field review, signature collection, audit-trail capture, and controlled storage.
Field preparation
Upload the authorization, review auto-detected fields, and add patient, recipient, purpose, expiration, and signature fields before sending.
Signer routing
Route the form to a patient or authorized representative by email or signing link, reducing manual handoffs for defined medical-record requests.
Audit trail
Capture signature events, timestamps, and document history so records staff can connect the completed authorization with its signing process.
Reusable templates
Use templates for stable authorization language while reviewing patient-specific record scope and recipient information before every request.
HIPAA workflow
Apply signNow’s HIPAA workflow with a BAA required, alongside access controls and procedures for protected health information.
Secure storage
Complete the authorization on desktop or mobile devices, then preserve the signed document and audit evidence in the approved records repository.
How to complete this authorization
Prepare the exact medical-record scope and recipient before sending the authorization through signNow.
Upload form:
Upload the blank authorization to signNow. Check fields:
Review detected fields and add missing patient, recipient, purpose, and signature fields. Assign signer:
Assign the patient or representative as signer. Send request:
Send the authorization by email or signing link. Archive record:
Store the signed form and audit trail securely.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
How the authorization process works
The form connects the patient’s permission to a defined medical-record request, signer evidence, and the provider’s controlled disclosure process.
Define scope: Patient identifies the requested records and recipient. Review terms: Provider or representative reviews authorization details. Sign form: Signer completes fields and confirms consent. Release records: Records team releases only authorized copies.
Recommended authorization workflow setup
Configure the authorization around patient identity, limited disclosure, signer evidence, protected storage, and controlled access for records staff.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Electronic signature with signer consent |
| Audit trail | Enable completion certificate and event history |
| Document retention | Six years for HIPAA documentation under 45 CFR 164.530(j) |
| Encryption and provisioning | AES-256 storage with administrator-controlled users |
Audit trail evidence for medical authorizations
The signNow audit trail records technical events that help connect this medical-record authorization to its signer, timing, document, and completion history.
Signer authentication:
Timestamp capture:
Document hashing:
Tamper-evident sealing:
Event logging:
Audit export:
Security for medical record authorizations
Transit encryption:
Storage encryption:
Healthcare compliance:
Control assurance:
Security management:
Signer verification:
Mobile signing for medical authorizations
Use the signNow mobile app on iOS 15 or later or Android 9 or later, with TLS 1.2 or 1.3 protecting browser and app connections.
iPhone app iOS 15 or later Android app Android 9 or later Document capture Camera capture for scans
A healthcare office can capture a paper authorization with the device camera, review fields, and route it for signature. Confirm device management, screen locks, permitted storage, and HIPAA safeguards before handling protected health information. Offline availability should be confirmed for the selected workflow and account configuration.
Medical records authorization retention periods
Retention depends on the record category and applicable rule; confirm state requirements before setting a final schedule.
6 years from creation or last effective date
3 years after hire or one year after termination
6 years under SEC Rule 17a-4
3 years under FLSA 29 CFR 516.5
30 years under OSHA 29 CFR 1910.1020
Record-keeping practices for authorizations
Use a precise authorization, preserve evidence of signing, and align storage with HIPAA, state privacy rules, and the records department’s approved schedule.
Define the permitted records and disclosure purpose
Export the audit trail with the signed authorization
Review every patient-specific field before sending
Restrict access to protected health information
Risks of incomplete medical authorization
PHI exposure
Missing consent
Vague authorization
Incomplete audit trail
Medical records authorization troubleshooting
Resolve the form’s legal and workflow issues by checking authorization scope, signer identity, plan capabilities, and HIPAA safeguards together.
Business includes legally binding eSignatures, templates, and audit trails. Upload the authorization, place fields over the patient, representative, provider, and date areas, then send it. HIPAA workflows require a BAA with signNow and appropriate administrative safeguards; the signature platform does not replace authorization requirements.
Business Premium adds bulk send, but each authorization still needs accurate patient and recipient data. Use a reusable template only for stable language; personalize patient identifiers, permitted records, recipient, purpose, expiration, and revocation instructions before sending.
If the authorization is consumer-facing, ESIGN requires disclosure of the right to paper, electronic-access capability, and withdrawal procedures under 15 U.S.C. §7001(c). Obtain consent before relying on electronic delivery, and retain a reproducible copy of the signed record.
Use signNow’s signer authentication options, including SMS verification where configured, to strengthen attribution. Authentication does not cure a missing purpose, overbroad records scope, absent expiration, or state-law requirement for a particular authorization format.
The Business plan includes audit trails and templates. If your process requires advanced signer authentication or conditional fields, Enterprise adds those capabilities. Review the plan configuration before sending sensitive medical-record authorizations.
HIPAA compliance is listed for signNow with a BAA required. Configure access controls, limit recipients, protect downloaded copies, and verify state privacy rules. HIPAA compliance by the platform does not authorize disclosure without a valid patient authorization.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.