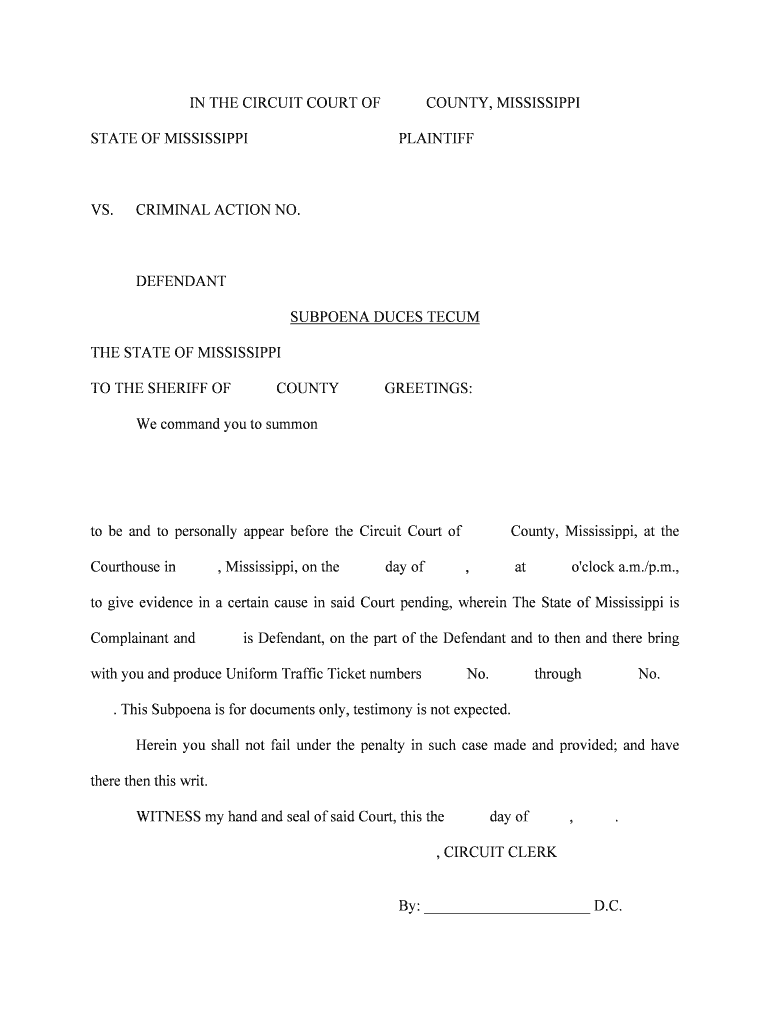
We Command You To Summon Form
Use a We Command You To Summon template to make your document workflow more streamlined.
What this form is and how it works
The We Command You To Summon Form is a document identified by its supplied name, but no issuing agency, statutory purpose, required fields, filing deadline, or official instructions are provided. In signNow, a sender uploads the source file, reviews any automatically detected fillable fields, adds signer roles, and sends the document for completion. Signers review the contents, demonstrate intent, and apply an electronic signature. signNow then retains the completed document and audit trail. Confirm the form’s legal purpose and required execution method before relying on it.
Legal standing depends on execution
A completed We Command You To Summon Form may support a U.S. business transaction when the signer demonstrates intent, consents to electronic records, can be identified, and the record remains reproducible under ESIGN, 15 U.S.C. chapter 96, and applicable UETA or New York ESRA rules. Wills, court orders, and certain family-law documents are excluded.

Businesses that may use this form
The form name does not identify an issuing agency, filing obligation, or industry-specific audience, so use depends on the underlying transaction.
A solo consultant can use the We Command You To Summon Form to collect a client’s completed information and signature without coordinating an in-person exchange, provided the document’s underlying transaction permits electronic execution. A legal-services practice can route the We Command You To Summon Form through designated reviewers, capture signer consent, and preserve the completed record for a matter file without treating signNow as the source of legal requirements. An enterprise compliance team can standardize the We Command You To Summon Form through shared templates, delegated sending, and controlled permissions while applying its own retention and approval policies across departments.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Platform requirements for completing this form
Complete the We Command You To Summon Form in Chrome, Firefox, Safari, or Edge on Windows or macOS. signNow protects data in transit with TLS 1.2 or TLS 1.3, and mobile apps are available for iOS and Android.
Browsers Chrome, Firefox, Safari, Edge Operating systems Windows, macOS, iOS, Android Secure connection TLS 1.2 or TLS 1.3
Organizations should use managed Windows, macOS, iOS, or Android devices when the form contains confidential information. Enterprise deployments may also require API access, SSO provisioning, and certificate or long-term validation settings selected according to the organization’s security policy.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
How this form works in signNow
The signNow workflow converts the source document into a controlled signing request while preserving the completed form and its audit evidence.
Upload: Upload the source document Prepare fields: Review detected fillable fields Assign signers: Add signers and delivery order Complete: Collect signatures and save records
Steps to complete this form
Prepare the supplied We Command You To Summon Form in signNow, verify every field, and preserve the completed document with its audit evidence.
Upload:
Upload the source file Review:
Check detected fields and labels Assign:
Add signer emails and order Send:
Send the signing request Store:
Download the signed form and audit trail
What the audit trail records
The audit trail provides evidence about who interacted with the We Command You To Summon Form, when actions occurred, and whether the final record was changed.
Authenticate signer:
Capture timestamp:
Hash document:
Seal record:
Log activity:
Export evidence:
Recommended setup for this form
Use a controlled signing workflow that preserves the completed We Command You To Summon Form, signer evidence, and the policy governing its underlying transaction.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS verification |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Export with the completed PDF |
| Document retention | Apply the underlying transaction rule |
| Encryption | TLS 1.2 or TLS 1.3 in transit |
Record-keeping practices for this form
Because this form has no identified issuing agency or statutory retention period, retain it according to the underlying transaction, contract, or organizational policy.
Set the governing retention period
Export the audit trail
Limit access to signed records
Archive immutable final copies
Signer authentication and certificates
Signer authentication:
Two-factor authentication:
Identity verification:
Digital certificates:
Certificate identity:
Audit evidence:
Risks when execution is incomplete
Weak execution
Attribution dispute
Integrity challenge
Evidence gap
Privacy and disclosure pitfalls
Personal information may be exposed when the completed We Command You To Summon Form is emailed to unintended recipients or stored in an uncontrolled location. A signer may complete the document without a clear electronic-record consent process when the transaction is consumer-facing under 15 U.S.C. §7001(c). Shared accounts can weaken attribution because the audit trail may not clearly connect each action with one authorized individual. Unrestricted downloads can create conflicting copies of the completed form and make it difficult to identify the authoritative record.
Troubleshooting this form workflow
Resolve the issue by checking the source document, signer requirements, electronic-signature rules, and the retention policy for the underlying transaction.
The supplied name does not identify required fields, an issuing agency, or an official filing purpose. Upload the source document, inspect signNow’s detected fields, and confirm missing requirements against the form owner’s instructions before sending.
signNow Business includes templates, audit trails, and legally binding eSignatures at $8 per user per month when billed annually. Verify that the document owner permits electronic completion before relying on the signature.
A sender can add signer email addresses, assign roles, and set signing order before delivery. If the form requires stronger attribution, configure SMS authentication or another available signer-verification method.
ESIGN and UETA generally recognize electronic signatures when intent, consent, attribution, and record reproducibility are established. Consumer-facing records may also require the disclosure and access procedures in 15 U.S.C. §7001(c).
The form’s name provides no retention period. Apply the rule governing its underlying transaction, export the completed PDF and audit trail, and preserve both in a controlled repository.
Business Premium costs $15 per user per month when billed annually and includes bulk send. Business Premium does not establish that this particular form may be distributed in bulk; confirm the form owner’s instructions first.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.