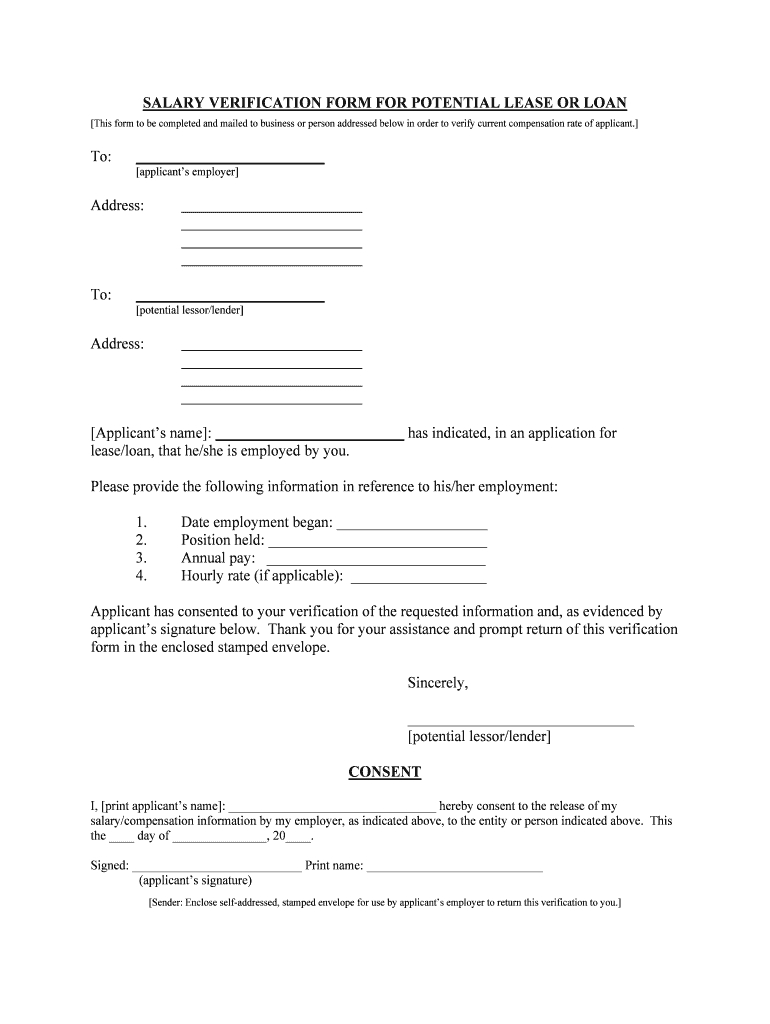
Applicant Has Consented To Your Verification Of The Requested Information And, As Evidenced By
Use a Applicant Has Consented To Your Verification Of The Requested Information And, As Evidenced By template to make your document workflow more streamlined.
What this applicant consent form does
This form records an applicant’s permission for a named party to verify specified information. It should identify the applicant, describe the requested information or verification scope, and capture the applicant’s intent to authorize that review. With signNow, the sender uploads the authorization, reviews detected fillable fields, assigns applicant and verifier fields, sends the document, and stores the completed form with its audit trail. ESIGN and UETA can recognize electronic signatures when consent, intent, attribution, and record retention are established, subject to statutory exclusions.
Who uses this verification authorization
Employment screening
Hiring teams and background-screening coordinators use the authorization to document an applicant’s permission before contacting listed sources or reviewing specified records. They can route the form for signature, preserve the signed copy, and retain the audit trail with the applicant’s verification file.
Applicant verification
Lenders, property managers, insurers, and regulated service providers use the form when an applicant authorizes verification of stated information. The workflow helps separate the applicant’s consent from later verification results and keeps the signed authorization available for review.
How the applicant authorization works
The workflow turns the applicant’s verification permission into a signed, traceable record without changing the authorization’s stated scope.
Upload document: Upload the applicant authorization to signNow. Review fields: Confirm detected applicant, consent, date, and signature fields. Assign roles: Assign fields to the applicant and verifier. Complete record: Send, sign, and retain the completed authorization.
Complete and sign the authorization
Use signNow to prepare the applicant’s verification authorization, capture consent, and preserve the completed record with its audit trail.
Upload form:
Upload the applicant consent document. Check fields:
Review detected names, dates, and signature fields. Add signers:
Add the verifier and applicant recipients. Send form:
Send for consent and signature. Store evidence:
Download the signed record and audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended consent workflow setup
Configure the authorization around identifiable applicants, limited verification scope, documented consent, and secure retention of the completed record.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS OTP |
| Signature type | Typed or drawn eSignature |
| Audit trail | Enable complete document history |
| Document retention | Follow applicable state policy |
| Encryption | TLS 1.2/1.3 and AES-256 |
Audit trail evidence for applicant consent
The audit trail connects the applicant’s authorization to signer activity, timestamps, document history, and the retained completion record.
Signer authentication:
Timestamp capture:
Document integrity:
Audit sealing:
Activity history:
Export evidence:
Best practices for verification consent records
A precise scope, traceable signer identity, preserved audit evidence, and documented retention policy make this authorization easier to review and administer.
Define the verification scope before sending
Connect the applicant to the authorization
Export the audit trail with the signed form
Apply a documented retention policy
Legal standing of applicant verification consent
This authorization documents the applicant’s intent to permit verification of specified information. Under ESIGN, 15 U.S.C. ch. 96, and UETA, an electronic record and signature can be recognized when consent, intent, attribution, and reliable retention are demonstrated; excluded records, including wills and certain court filings, require separate legal handling.

Security controls for consent records
Transport encryption:
Stored-data encryption:
Security certification:
Information security:
Privacy compliance:
Healthcare protection:
Privacy pitfalls in verification consent
Failing to identify the exact information the applicant authorizes can make later verification evidence ambiguous. Collecting a signature without recording consent to electronic records may weaken the authorization file. Sharing the completed consent form with unauthorized recipients can expose personal verification information. Using one unrestricted template can let staff request information beyond the applicant’s stated authorization.
Transactions requiring special handling
May require in-person acknowledgment
Excluded from ESIGN
Certain decrees excluded
Official filing rules apply
Troubleshooting consent verification forms
Resolve field, authentication, retention, and electronic-signature questions before sending the applicant’s verification authorization.
Upload the completed consent document to signNow and confirm that signature, date, applicant identity, and authorization fields were detected correctly. The Business plan includes templates and audit trails; review every field before sending because signNow cannot determine whether the requested verification scope is legally sufficient.
Use a clear electronic-record disclosure and confirm the applicant can access the document before signing. ESIGN, 15 U.S.C. §7001(c), requires consumer consent procedures when applicable, including paper-record rights and withdrawal procedures. Preserve the disclosure and consent evidence with the signed authorization.
Choose email authentication for routine business workflows or add SMS OTP and ID verification when stronger attribution is needed. signNow supports two-factor authentication, while Enterprise adds advanced signer authentication. Select controls proportionate to the sensitivity of the requested verification information.
The Business plan is listed at $8 per user per month with annual billing and includes audit trails and templates. It does not include every advanced control; Business Premium adds bulk send, while Enterprise adds advanced signer authentication.
Export the completed document and audit trail after signing, then store them under your organization’s retention policy. signNow provides document history and audit-trail records, but the applicable retention period depends on the transaction, industry, and state requirements governing this authorization.
Electronic signatures generally receive legal recognition under ESIGN and UETA when intent, consent, attribution, and record retention are demonstrated. Those laws exclude wills, codicils, certain court filings, and other listed records, so confirm that this authorization is not being used for an excluded transaction.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.