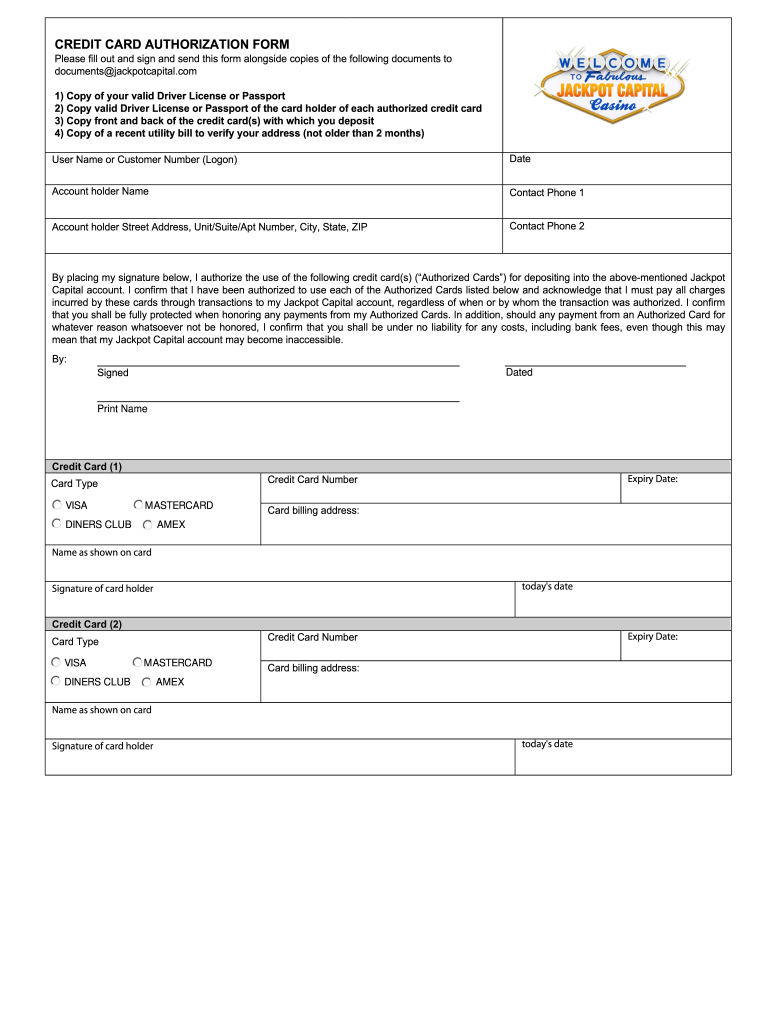
Capital Hotel Credit Card Authorization Form
Create a custom Capital Hotel Credit Card Authorization Form Pdf 0 that meets your industry’s specifications.
What this hotel authorization form does
The Capital Hotel Credit Card Authorization Form records a cardholder’s permission for a hotel to charge an identified card for stated lodging-related expenses. It commonly connects the cardholder, guest or reservation, approved charges, amount, and signature in one record. The form is not a substitute for the hotel’s processor rules, PCI DSS controls, or state requirements. In signNow, staff upload the template, verify detected fields, send it to the cardholder, collect an electronic signature, and retain the signed PDF with its audit trail.
Who uses this hotel authorization form
Hotels
Hotels and lodging groups use the form to obtain cardholder permission for room charges, deposits, incidentals, and approved reservation payments. Staff can send a prepared authorization for electronic signature, retain the signed record, and connect it with the reservation or folio.
Booking teams
Travel coordinators, event planners, and corporate booking teams use it when a cardholder authorizes charges for another guest or group stay. The form should identify the authorized traveler, transaction scope, amount, and responsible payer before signature.
How to complete the authorization
Prepare the Capital Hotel Credit Card Authorization Form in signNow, verify the transaction fields, and preserve the completed record after signing.
Upload form:
Upload the hotel’s authorization template to signNow. Check fields:
Let signNow detect fillable fields, then verify each field. Add signer:
Add the verified cardholder as the signer. Send form:
Send the authorization and monitor completion. Store record:
Store the signed PDF with its audit trail.
Recommended setup for hotel authorizations
Use a controlled workflow that identifies the cardholder, records consent, and preserves the completed authorization with its audit evidence.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Typed or drawn eSignature |
| Audit trail | Capture signer actions and timestamps |
| Document retention | Retain records under hotel policy |
| Encryption | TLS 1.2/1.3 and AES-256 |
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
How the authorization audit trail works
The audit trail documents who approved the Capital Hotel Credit Card Authorization Form, when each action occurred, and how the final record can be reviewed.
Authenticate signer:
Capture timestamps:
Hash document:
Seal record:
Log activity:
Retrieve evidence:
Platform requirements for hotel authorizations
The Capital Hotel Credit Card Authorization Form can be completed in Chrome, Firefox, Safari, or Edge on Windows 11 and macOS. Signers can also use signNow mobile apps on iOS and Android. Use an internet connection with TLS-enabled browser access when transmitting cardholder information.
Browser support Chrome, Firefox, Safari, and Edge Operating systems Windows 11, macOS, iOS, and Android Device access Desktop browser and signNow mobile apps
Hotel teams should use managed Windows 11 or macOS devices when preparing authorizations and restrict access to approved staff. Mobile signers can review and complete the form through signNow apps for iOS and Android. Configure account permissions, audit-trail access, and retention procedures before sending payment authorizations.
Processing stages for hotel authorizations
No universal legal turnaround period applies to this private hotel authorization; timing depends on the reservation, cardholder, and hotel’s payment procedures.
Prepare the authorization
Deliver to cardholder
Collect signature
Archive completion
Best practices for hotel card authorizations
Accurate transaction details, verified recipients, restricted access, and complete evidence make this hotel authorization easier to administer and review.
Complete transaction details before sending
Verify the cardholder before signature
Archive evidence under restricted access
Review the template periodically
Security for card authorization records
TLS 1.2/1.3 and AES-256:
PCI DSS certified:
SOC 2 Type II certified:
ISO 27001 certified:
ESIGN and UETA compliant:
Two-factor authentication available:
Privacy and disclosure pitfalls
Including the full card number in the signed PDF increases exposure if the document is emailed or downloaded without access controls. A missing cardholder consent statement can make the authorization harder to defend during a charge dispute or billing inquiry. Sending the form to an unverified guest email can associate approval with the wrong cardholder. Allowing every hotel employee to view completed authorizations creates unnecessary access to payment information.
Legal standing of the authorization
A signed Capital Hotel Credit Card Authorization Form can support a hotel’s records when the cardholder intended to sign, consented to electronic records, can be identified, and the record remains reproducible. ESIGN, 15 U.S.C. ch. 96, and applicable UETA or New York ESRA rules support electronic transactions, but wills, family-law decrees, court filings, and certain notarized documents are excluded.

Troubleshooting hotel card authorizations
These answers address signing, privacy, plan, and evidence questions that arise when hotels use this authorization form.
On the Business plan, the hotel can upload the authorization, add signer fields, send it, and preserve the audit trail. If a required field is missing, reopen the template and place the field before resending. The completed record should identify the cardholder and authorized transaction.
signNow Business includes legally binding eSignatures and audit trails. Under ESIGN and applicable state electronic-transactions law, the record can support attribution when intent, consent, signer identity, and reproducible retention are documented. Confirm the hotel’s state-specific requirements before relying on the form.
Business Premium includes bulk send, while Business does not list bulk send in the supplied plan details. For repeated guest authorizations, use Business Premium or send each authorization individually. Do not treat bulk-send availability as a feature of the Business plan.
For a consumer-facing card authorization, provide an electronic-record disclosure when required by ESIGN, 15 U.S.C. §7001(c). The cardholder must be able to access the record and understand how to withdraw consent. Store evidence of that disclosure with the signed authorization.
signNow supports TLS 1.2/1.3 in transit and AES-256 at rest. PCI DSS certification addresses cardholder-data safeguards, but the hotel remains responsible for limiting card data, configuring access, and following its payment processor’s storage rules.
Use signNow’s audit trail and certificate of completion to review signer actions, timestamps, and delivery history. If a dispute concerns the amount or purpose, compare the signed authorization with the reservation, folio, and processor records rather than relying on the signature alone.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.