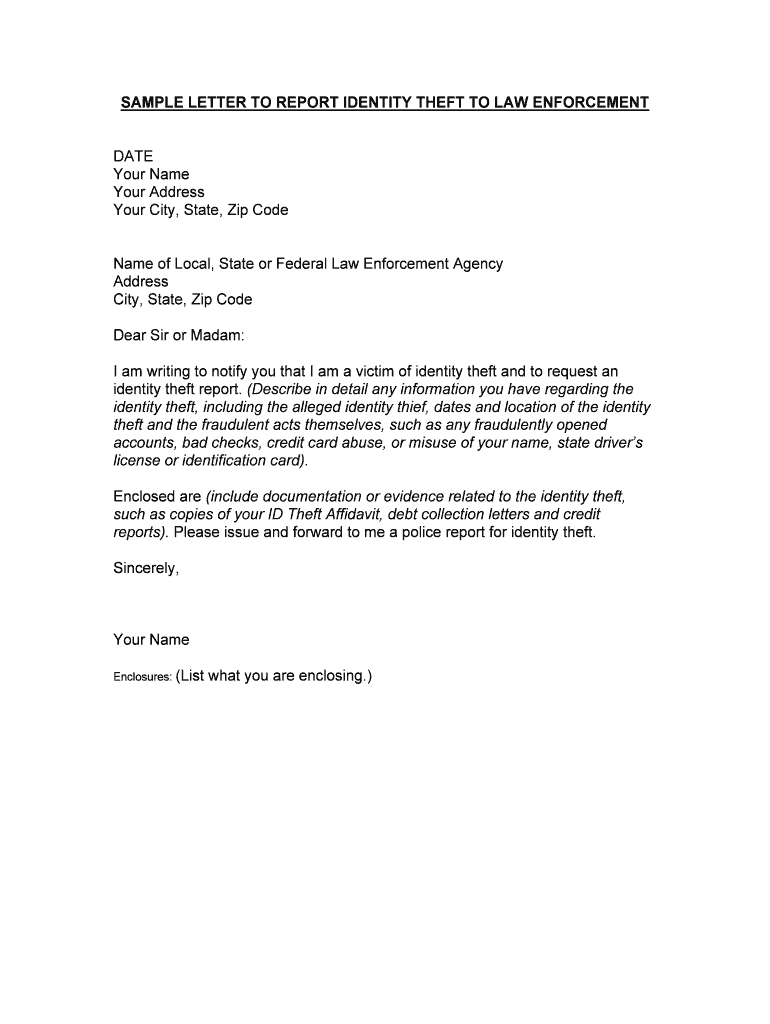
Letter To Report Identity Theft To Law Enforcement Form
Use a SAMPLE LETTER TO REPORT IDENTITY THEFT TO LAW ENFORCEMENT template to make your document workflow more streamlined.
What this identity-theft letter does
A Letter To Report Identity Theft To Law Enforcement Form records a person’s account of suspected identity theft for delivery to a law-enforcement recipient. It can identify the reporting person, describe the incident, list affected accounts or transactions, and provide a signed statement. The form itself does not replace a police department’s reporting procedure or guarantee an investigation. With signNow, upload the letter, review detected fields, add signature and date fields, send it to the intended signer, and preserve the completed document with a certificate of completion and audit trail.
Who uses identity-theft letters
This letter is most useful when a person or organization must document an identity-theft incident clearly, obtain a signature, and preserve the resulting record.
Identity-theft victims use the letter to organize incident details, sign their statement, and provide a traceable copy to a law-enforcement contact or financial institution. Legal-aid clinics prepare client-specific letters, collect signatures remotely, and preserve supporting evidence without asking clients to revisit an office for every revision. Fraud investigators and compliance teams use standardized letters to gather statements, document authorization, and route completed reports through controlled internal review.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Features for this identity-theft letter
signNow connects document preparation, signature collection, and evidence preservation for a Letter To Report Identity Theft To Law Enforcement Form.
Field detection
Upload the identity-theft letter and let signNow detect likely fillable areas before reviewing and correcting each field.
Signature fields
Add the reporting person’s signature, date, and required statement fields without recreating the letter from scratch.
Remote signing
Send the prepared letter by email or signing link to the intended signer and monitor its completion status.
Audit trail
Capture timestamps, signer actions, and document history in a certificate of completion for later review.
Mobile access
Use mobile apps to prepare or sign the letter on iOS and Android devices, including supported offline workflows.
Data protection
Protect sensitive incident information with TLS 1.2/1.3 in transit and AES-256 encryption at rest.
Complete the identity-theft letter
Prepare the letter in signNow by uploading it, checking detected fields, assigning signers, and preserving the completed report with its audit trail.
Upload documents:
Upload the identity-theft letter and supporting evidence to signNow. Check fields:
Review auto-detected fields and add missing names, dates, and signature fields. Assign signers:
Assign the reporting person and any authorized reviewer as signers. Send and monitor:
Send the prepared letter, then monitor completion in signNow. Store evidence:
Download the signed letter and certificate of completion for records.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Review the signNow audit trail
The audit trail shows who handled the identity-theft letter, what happened, and when, creating a reviewable record alongside the completed document.
Authenticate signer:
Capture timestamps:
Hash document:
Seal record:
Build certificate:
Export trail:
Recommended identity-theft workflow setup
Configure the identity-theft letter workflow around recipient verification, a reviewable signing record, and the retention policy governing the agency or organization receiving the report.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS verification |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Enable certificate of completion |
| Document retention | Follow the applicable agency policy |
| Encryption | Use TLS 1.2/1.3 and AES-256 |
Security for identity-theft records
Data in transit:
Stored documents:
Security reporting:
Information security:
U.S. eSignatures:
Protected health information:
Mobile options for identity-theft letters
Use signNow on iOS 15 or later and Android 10 or later through its mobile apps. The workflow can capture a paper identity-theft letter with a device camera, prepare fields, and support offline signing when a document has already been made available.
Mobile apps iOS 15 or later and Android 10 or later support signNow mobile workflows. Camera capture Camera capture imports identity-theft letters and supporting evidence into signNow. Offline signing Offline signing lets authorized users complete prepared documents without connectivity.
For sensitive identity-theft reports, use managed iOS or Android devices, require screen protection, and restrict downloaded copies. Camera capture should be checked against the original letter before sending. Reconnect promptly after offline signing so the completed record and audit trail synchronize with the signNow account.
Privacy pitfalls to avoid
Including a full Social Security number or account number can expose sensitive identity data to unnecessary recipients. Sending the letter before checking names, dates, addresses, and incident details can create an inaccurate law-enforcement record. Failing to capture electronic consent can weaken the record when a consumer signs through a remote workflow. Leaving the completed letter accessible to every team member can disclose personal information beyond the assigned case.
Documents outside this workflow
State rule applies
Excluded from ESIGN
Court rules apply
Notary may be required
Record-keeping practices for this letter
Protect the identity-theft report by validating its contents, limiting disclosure, exporting the audit record, and applying the retention rule that actually governs the recipient’s records.
Verify every incident detail
Minimize exposed personal data
Export the evidence package
Apply the correct retention policy
Key performance indicators that demonstrate SignNow's proven track record.
Troubleshooting identity-theft letters
Use these answers to resolve signing, submission, plan-limit, and compliance questions specific to a Letter To Report Identity Theft To Law Enforcement Form.
Upload the letter again as a clear PDF or image, then check every auto-detected field manually. signNow’s Business plan includes templates and audit trails, but field recognition still requires human review for names, dates, and incident details.
Open the recipient’s signing link again and confirm the email address or SMS number. If stronger authentication is required, Business Premium supports request workflows, while Enterprise adds advanced signer authentication options.
Use signNow’s audit trail and certificate of completion to show intent, attribution, timestamps, and document history. ESIGN and UETA recognize electronic signatures when those elements and record reproduction requirements are satisfied.
Do not assume the signed letter was filed with police or another agency. signNow completes the signing workflow; the reporting person must follow the receiving agency’s submission instructions and preserve any confirmation separately.
Business is priced at $8 per user per month when billed annually and includes 100 signature invites per user per year. Additional invites can create overage charges, so review plan usage before sending many letters.
For identity-theft letters containing health information, signNow states that HIPAA compliance requires a BAA. Apply HIPAA’s six-year retention rule only when the record is maintained as a HIPAA-covered record under 45 CFR 164.530(j).
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.