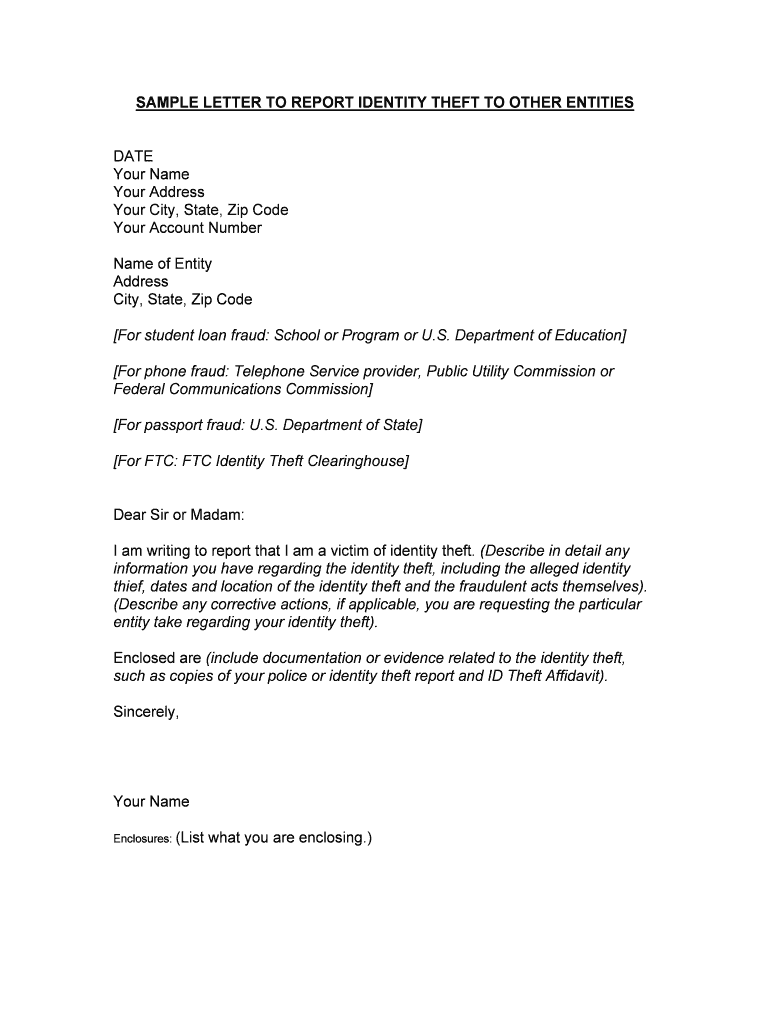
Letter To Report Identity Theft To Other Entities Form
Use a SAMPLE LETTER TO REPORT IDENTITY THEFT TO OTHER ENTITIES template to make your document workflow more streamlined.
What this identity theft letter does
A Letter To Report Identity Theft To Other Entities Form is a written notice that tells a creditor, bank, insurer, lender, or service provider that identity theft affected an account or transaction. The sender identifies the disputed activity, explains the requested correction, and supplies relevant evidence. It does not replace an agency-specific dispute process, police report, fraud affidavit, or state-required notice. In signNow, the sender uploads the letter, reviews detected fields, adds recipients, signs electronically, and retains the completed record and audit trail.
Who uses this identity theft letter
Identity theft victims
Individuals report identity theft to banks, lenders, insurers, creditors, and service providers using documented facts and supporting records.
Advocacy and legal teams
Consumer advocates and legal teams prepare consistent notices, route them for signature, and retain delivery evidence for follow-up.
How the identity theft letter works
The letter creates a documented notice that connects the identity theft facts, requested remedy, recipient, and supporting evidence.
Describe the incident: State the identity theft incident and affected account details. Identify the recipient: Name each recipient and specify the requested corrective action. Add supporting records: Attach relevant evidence and obtain the sender’s signature. Send and retain: Deliver the signed letter and preserve delivery evidence.
Steps to complete the identity theft letter
Use signNow to prepare the letter, confirm its details, collect the signature, and preserve the resulting evidence.
Upload letter:
Upload the identity theft letter to signNow. Check fields:
Review auto-detected fields and add missing details. Set recipients:
Add the recipient and signature request. Complete workflow:
Sign, send, and store the completed record.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended setup for identity theft letters
Use a controlled workflow that verifies the sender, records each signature event, and preserves the completed identity theft report.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS verification |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Capture timestamps, IP address, and actions |
| Document retention | Retain signed letter and certificate securely |
| Encryption | Use TLS 1.2/1.3 and AES-256 |
Authentication options for identity theft letters
Signer authentication:
SMS verification:
Identity questions:
ID verification:
Digital certificates:
Signing record:
Risks of an incomplete report
Evidence dispute
Incomplete details
Privacy breach
Missing signature
Best practices for identity theft reports
Accurate facts, controlled disclosure, and a complete signing record make this letter easier for recipients to investigate and act on.
List affected accounts and requested actions
Use the recipient’s designated reporting channel
Minimize sensitive information in attachments
Preserve the signed reporting record
Identity theft letter processing timeline
Use this sequence to prepare, sign, deliver, and preserve a Letter To Report Identity Theft To Other Entities Form.
Prepare the letter
Deliver to recipient
Track recipient response
Archive the record
Legal standing of the signed letter
For a business recipient, an electronically signed identity theft letter can be retained as evidence when the signer shows intent, consents to electronic records, can be identified, and the record remains reproducible under ESIGN and applicable UETA or New York ESRA rules. Wills, court orders, and family-law decrees remain excluded from ESIGN’s coverage.

Privacy pitfalls in identity theft reports
Including full account numbers or unrelated personal data can expose information beyond what the recipient needs to investigate the identity theft report. Sending without documented electronic-record consent can create uncertainty about whether the recipient may rely on the signed notice. Sharing the completed letter through an unrestricted link can expose identity theft details to unintended viewers. Giving every team member editing access can alter recipient details, requested remedies, or supporting evidence before delivery.
Key performance indicators that demonstrate SignNow's proven track record.
Troubleshooting identity theft letter workflows
Resolve field, consent, authentication, delivery, and retention questions before relying on a signed identity theft report.
Upload the original PDF again and inspect auto-detected fields before sending. If a field is misplaced, edit its position and confirm the recipient assignment. The Business plan includes templates and audit trails, but field detection still requires human review for this identity theft letter.
Business includes legally binding eSignatures and audit trails at $8 per user per month when billed annually. The plan includes 100 signature invites per user per year; additional usage may incur overage fees, so review account usage before repeated reporting workflows.
Use signNow’s audit trail to document the signer, timestamps, IP address, and actions. For consumer-facing records, provide the ESIGN disclosure, explain the right to paper records, and maintain procedures for withdrawing electronic consent under 15 U.S.C. §7001(c).
Use a recipient-specific signing order when the sender must sign before another reviewer. signNow supports role-based routing and audit trails; verify the recipient’s required fraud affidavit, dispute form, or delivery channel separately because this letter does not replace those requirements.
Enable stronger authentication when the letter contains sensitive account details. Business Premium adds bulk send and kiosk mode, while Enterprise adds advanced signer authentication. Select controls based on the recipient’s security requirements and the information disclosed.
Export the signed PDF and certificate of completion after signing, then restrict access to the case team. signNow supports encrypted data protection, ISO 27001 certification, SOC 2 Type II certification, and ESIGN/UETA compliance; recipient retention rules still apply.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.