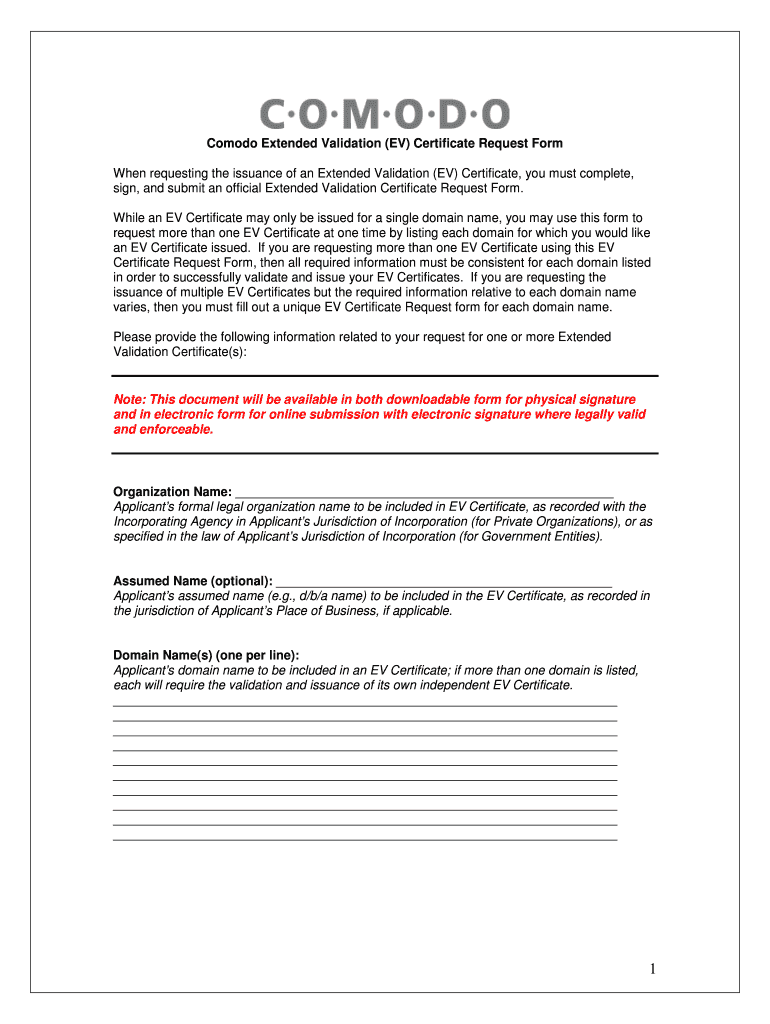
Comodo Extended Validation Ev Certificate Request Form When En Gandi
Get a Comodo Extended Validation EV Certificate Request Form When En Gandi 0 template with airSlate SignNow and complete it in a few simple clicks.
Comodo Extended Validation certificate request overview
The Comodo Extended Validation Ev Certificate Request Form When En Gandi is a request document used to organize information needed for an Extended Validation certificate workflow involving Gandi. It identifies the organization, domain, administrative contacts, and authorization details that the certificate process requires. With signNow, a sender uploads the request, reviews automatically detected fillable fields, adds or corrects fields, routes the document to the authorized signer, and stores the completed request with its audit trail. The form itself does not replace Gandi’s validation or issuance decision.
Features for certificate request preparation
signNow organizes the Comodo Extended Validation certificate request from field preparation through approval, signing, audit review, and retention.
Structured preparation
Upload the Comodo Extended Validation certificate request form, then prepare its organization, domain, contact, and validation details in one controlled document workflow.
Reusable templates
Reusable templates preserve recurring certificate-request fields and reduce retyping when Gandi account or organization information remains unchanged.
Signer routing
Assigned signer fields direct approvals to the right Gandi or organizational contact without relying on email-only document circulation.
Audit visibility
The completed request remains linked to its audit trail, supporting review of signer identity, timestamps, document activity, and final record status.
Mobile access
Mobile apps let authorized users review or sign the request when certificate administration occurs away from a desktop workstation.
Controlled access
Role-based access and shared workspaces help certificate teams separate preparation, approval, and administrative responsibilities for the request.
Teams that manage certificate requests
A certificate administrator can upload the Comodo Extended Validation request, assign organization and domain fields, and route the completed form to an authorized Gandi contact. Workspace roles limit who may edit templates, send requests, or access finished audit records. A security or IT team can maintain a shared request template while delegating individual sends. Admin controls, signer permissions, and audit-trail access keep certificate requests separated from unrelated business documents and provide a repeatable approval record.
Business types using certificate requests
The form is most useful where certificate ownership, domain authorization, and signer accountability must be documented consistently.
Solo IT consultants can prepare and route one Gandi certificate request while keeping signer correspondence and the completed audit record together in signNow. Security departments can standardize organization and domain validation requests through shared templates, controlled permissions, and documented approval responsibilities. Enterprise infrastructure teams can connect certificate paperwork with Salesforce, NetSuite, Google Drive, or AWS records while preserving an auditable signing workflow.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
How to complete the certificate request
Prepare the Comodo Extended Validation request in signNow, verify its certificate data, and preserve the completed record.
Upload:
Upload the request PDF. Check fields:
Review detected certificate fields. Assign signer:
Assign the authorized signer. Send:
Send through signNow. Archive:
Store the signed request.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Ways to send and sign the request
- Use the signNow web app when preparing the Comodo Extended Validation request, placing fields, checking domain and organization information, and routing the document from a desktop workflow.
- Use the signNow mobile app when an authorized certificate contact must review or sign the request from an iOS or Android device.
- Use kiosk mode when a supervised administrator needs an authorized person to complete the request on a controlled shared device.
- Use a shareable signing link when the designated Gandi contact should open the prepared request directly without receiving a separate multi-step email workflow.
What the audit trail records
The audit trail documents how the Comodo Extended Validation request moved from signer authentication to a retrievable completed record.
Authenticate signer:
Capture timestamp:
Record document hash:
Seal evidence:
Link activity:
Export records:
Recommended request workflow setup
Configure the certificate request around signer attribution, document integrity, controlled access, and the retention rules that apply to your Gandi workflow.
| Setting | Recommendation |
|---|---|
| Authentication method | Email authentication with SMS OTP when required |
| Signature type | Electronic signature with signer intent |
| Audit trail | Enable completion history and export |
| Document retention | Follow Gandi and organizational policy |
| Encryption | TLS in transit and AES-256 at rest |
Security controls for certificate requests
PKI:
X.509 certificates:
Two-factor authentication:
SMS OTP:
ID verification:
Audit trail:
Platform requirements for the request
Complete the Comodo Extended Validation certificate request in Chrome, Firefox, Safari, or Edge on Windows 10, Windows 11, or macOS. signNow also provides iOS and Android apps for review and signing. Use an encrypted TLS connection and an up-to-date supported browser.
Browser support Chrome, Firefox, Safari, and Edge Desktop systems Windows 10, Windows 11, and macOS Mobile access iOS and Android signNow apps
Certificate teams should use managed Windows, macOS, iOS, or Android devices when the request contains organization or domain information. Enterprise deployments may add SSO provisioning, API access, and controlled workspace permissions. Configure retention and audit-record export according to Gandi requirements and the organization’s records policy.



Record-keeping practices for certificate requests
Accurate certificate data, controlled access, and linked audit records make the completed request easier to review and defend.
Export the request and audit trail
Preserve an immutable final record
Document the applicable retention rule
Verify certificate data before sending
Processing stages for certificate requests
Processing depends on accurate certificate information and signer availability; signNow separates preparation, delivery, signing, and archival.
Prepare the document
Deliver to signer
Complete signer review
Archive completed records
Challenges when preparing certificate requests
Entering an organization name that differs from Gandi’s account or registration records can delay validation and require a corrected certificate request. Sending the request before confirming the authorized signer may produce a signed document that does not establish the intended organizational approval. Including unnecessary personal data in the request increases disclosure exposure when the document is shared with certificate administrators or external contacts. Failing to export the audit trail with the signed request leaves reviewers without the complete record of signer actions and completion history.
Troubleshooting certificate request workflows
These answers address field detection, signer access, plan selection, security controls, legal context, and record handling for this certificate request.
Upload the original Comodo Extended Validation request as a PDF or supported document, then confirm that signNow’s detected fields match the form. If fields are missing, add them manually before sending; do not rely on a visual signature alone for required certificate-request information.
The Business plan provides legally binding eSignatures, audit trails, templates, and mobile apps at $8/user/month when billed annually. Business Premium adds bulk send at $15/user/month; choose it only when the same request must be sent repeatedly.
A signer may review and sign without a full signNow account when the invitation permits guest signing. If stronger attribution is required, configure available authentication controls, document the signer’s role, and preserve the resulting audit trail with the completed request.
signNow states that ESIGN and UETA compliance supports electronic signatures in U.S. transactions. That does not replace Gandi’s certificate-validation requirements or prove that every request detail is accurate; the organization must verify identity, authority, and domain information separately.
If a request contains personal or organizational information, restrict workspace access and send it only to the designated certificate contact. signNow provides audit trails and role-based workflow controls, while the sender remains responsible for consent, disclosure, and least-privilege configuration.
Export the signed request and its audit trail after completion, then store both together under the organization’s records policy. signNow’s audit trail preserves signing activity, while Gandi-specific renewal or certificate records may require additional retention instructions from Gandi or the customer’s security team.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.