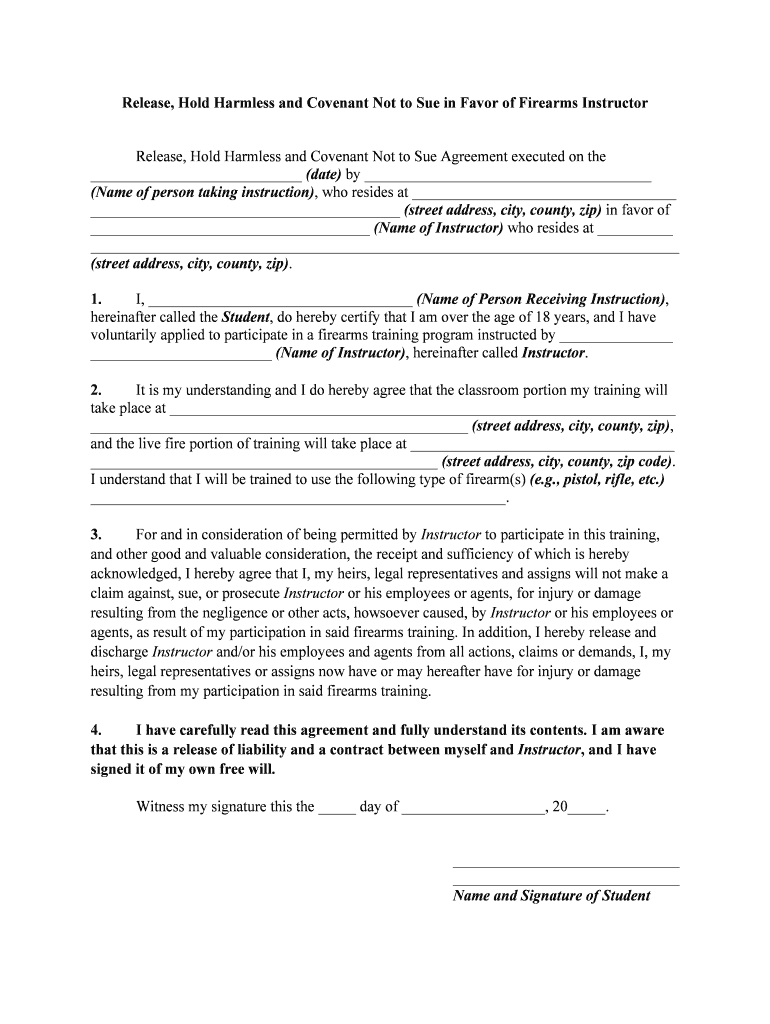
Covenant Not To Sue And Agreement To Hold Harmless Tamu Form
Use a Covenant Not To Sue And Agreement To Hold Harmless TAMU template to make your document workflow more streamlined.
What this covenant form does
This form is a written agreement in which a participant acknowledges specified risks, promises not to sue for covered matters, and agrees to hold another party harmless to the extent the wording and applicable law allow. The signer should review the activity, released claims, assumptions, exclusions, party names, dates, and signature requirements before execution. Electronic signing may be legally recognized under ESIGN and applicable state law, but those statutes do not validate unclear terms or override exclusions for wills, court orders, family-law decrees, and other protected records.
Who uses this covenant form
Event and recreation operators
Event organizers and recreational operators use the covenant to document participant acknowledgment of activity risks, release language, and signature consent before attendance or participation.
Construction and property businesses
Construction and property businesses use it for site access, contractor acknowledgments, and activity-specific releases, while legal teams review state-law requirements and exceptions.
Features that support this covenant workflow
signNow connects document preparation, signer routing, authentication, audit evidence, and controlled storage for a repeatable covenant-signing process.
Field placement
Upload the covenant as a PDF and review automatically detected fields before assigning signatures, dates, initials, or acknowledgments to the correct participants.
Signer routing
Route the same covenant to participants, representatives, witnesses, or notaries in a defined order when the document requires separate execution roles.
Audit evidence
Capture timestamps, participant actions, and completion evidence through signNow’s audit trail, supporting later review of how the covenant was executed.
Signer verification
Use email delivery, SMS authentication, or signing links according to the identity and privacy risks associated with the activity described in the covenant.
Secure archival
Keep the signed covenant and completion certificate together in a controlled repository, applying the retention rule for the underlying record category.
Controlled templates
Use templates for recurring versions while limiting editing rights so approved hold-harmless language is not changed during routine preparation.
How to complete this covenant online
Prepare the covenant’s legal terms first, then use signNow to place fields, route signatures, and preserve evidence of completion.
Upload the form:
Upload the completed covenant PDF to signNow and confirm the correct version. Place required fields:
Review detected fields and add signature, initials, date, and acknowledgment fields. Assign signer roles:
Assign each field to the participant, organization representative, witness, or notary. Complete and archive:
Send the covenant, collect signatures, and download the signed file with its audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended setup for this covenant form
Configure the covenant workflow around signer identity, informed consent, audit evidence, and the retention rule applicable to the underlying activity.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Export certificate of completion |
| Document retention | Apply the governing record rule |
| Encryption | TLS 1.2 or 1.3 and AES-256 at rest (GDPR) |
What the covenant audit trail records
The audit trail documents execution evidence for this covenant, from signer access through completion and export of the final record.
Authenticate signer:
Timestamp actions:
Link signature:
Seal document:
Log consent:
Retrieve evidence:
Security controls for signed covenants
Encryption at rest:
Encrypted transmission:
Security certification:
Information security:
Electronic signature compliance:
Protected health information:
State-law risks and exclusions
State law limits
Consent dispute
Execution defect
Recording rejection
Retention periods for signed waiver records
Use the applicable period only when the signed covenant also belongs to the regulated record class described below.
Six years for HIPAA records
Three years for federal tax records
Five years for OSHA injury records
Thirty years for exposure records
Seven years for SOX records
Best practices for covenant recordkeeping
Accurate field placement, controlled access, complete audit evidence, and a documented retention decision help preserve this covenant’s evidentiary value.
Review the covenant’s substantive terms
Assign every required signer precisely
Export the complete audit record
Archive records under the governing rule
Covenant form troubleshooting and answers
These answers address signing, consent, authentication, plan limits, and recordkeeping issues specific to this covenant and hold-harmless workflow.
Upload the original Covenant Not To Sue And Agreement To Hold Harmless Tamu Form to signNow and check detected fields before sending. Business includes templates and audit trails; verify every signer role manually because field detection does not interpret legal meaning.
Business provides legally binding eSignatures, templates, audit trails, and mobile apps at $8 per user per month annually. Business Premium adds bulk send and kiosk mode at $15 per user per month annually when multiple participants need the same waiver.
Use SMS authentication or stronger signer verification when identity risk warrants it. signNow supports advanced signer authentication on Enterprise, while ESIGN and UETA require intent, consent, attribution, and retained reproducible records—not a particular authentication method.
For consumer-facing electronic records, provide the ESIGN disclosure, explain the right to paper records, confirm electronic access, and explain withdrawal procedures under 15 U.S.C. §7001(c). Store the disclosure and completed covenant together with the audit trail.
If the covenant requires notarization, signNow can capture signatures, but notarization requirements depend on state law and the document purpose. Confirm whether remote or in-person notarization is authorized before treating the completed file as sufficient.
Business plans include 100 signature invites per user each year; additional invites incur overage fees. Site License uses $1.50 per signature invite and supports unlimited users. Select the plan based on the number of covenant recipients and sending volume.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.