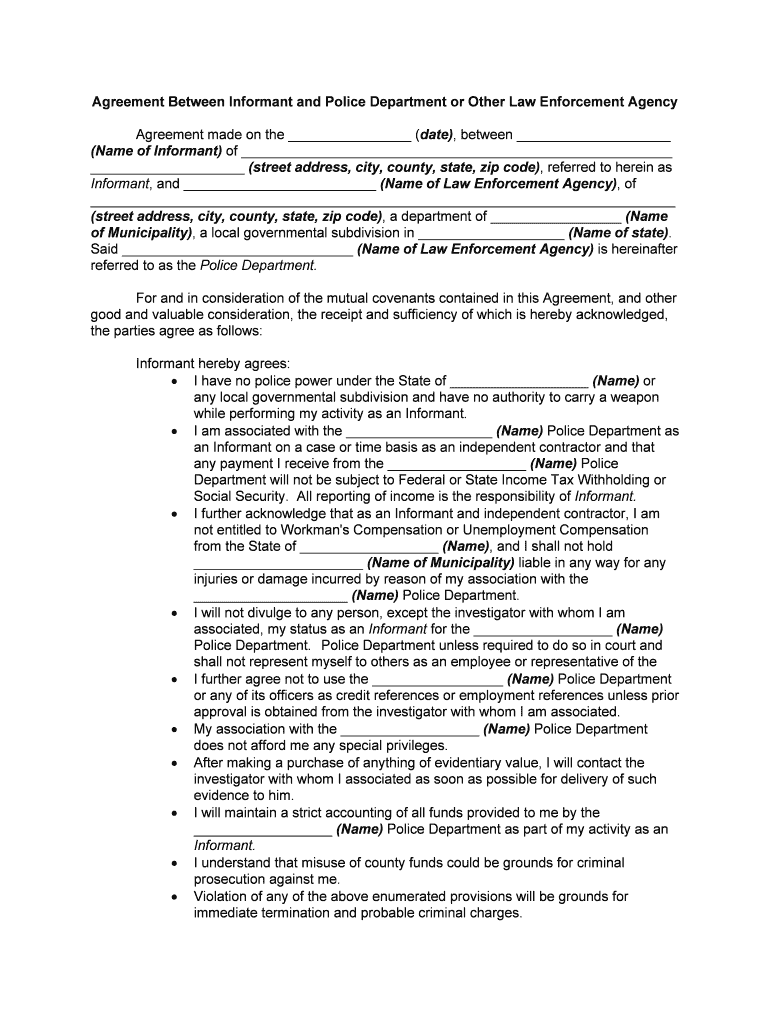
Confidential Informant Management And Control Procedures
Use a Confidential Informant Management And Control Procedures template to make your document workflow more streamlined.
What these procedures document
Confidential Informant Management And Control Procedures document how an organization authorizes, supervises, communicates with, and reviews a confidential informant relationship. The form typically captures responsible personnel, approval dates, handling restrictions, contact rules, risk controls, and signatures, but the exact fields depend on the issuing agency or organization. Upload the approved document to signNow, review its fillable fields, assign authorized recipients, and collect signatures with an audit trail. ESIGN and UETA can support electronic signatures for eligible business records, but agency policy, state law, and document-specific exclusions still control.
Who benefits from controlled procedures
The right workflow depends on who authorizes, handles, reviews, and preserves confidential informant records.
A solo investigator or attorney can use a restricted template to collect approvals, preserve signer evidence, and keep confidential procedures separate from ordinary client correspondence. A public-sector investigative unit can route handler certifications and supervisory approvals through controlled recipient roles, limiting access while preserving a complete audit trail for internal review. An enterprise compliance team can standardize confidential-procedure templates across departments, apply role-based permissions, and retain signed records under its approved information-governance policy.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Features for confidential procedures
signNow provides the document workflow, routing, and evidence controls needed to handle this procedure while organizational policy governs the underlying investigation.
Field review
Upload the approved Confidential Informant Management And Control Procedures PDF and review detected fields before assigning recipients, reducing missed signature, date, and approval fields.
Role routing
Route the document to handlers, supervisors, and authorized signers in a defined order, helping preserve separation between preparation, review, and approval responsibilities.
Audit evidence
Capture signer actions, timestamps, recipient activity, and completion evidence in an audit trail tied to the confidential procedure.
Mobile access
Use signNow’s mobile apps when authorized personnel must review or sign the procedure away from a desk, subject to agency security policy.
Record preservation
Keep the completed PDF and audit trail together so reviewers can examine the signed procedure and its transaction history as one evidence package.
Data protection
Apply signNow’s encryption and compliance controls to the workflow while separately confirming the agency’s confidentiality, retention, and access requirements.
How controlled procedures work
The workflow moves the Confidential Informant Management And Control Procedures document from controlled preparation through approval and evidence preservation.
Prepare document: Upload the controlled procedure and review its fields. Set recipient roles: Assign handlers, supervisors, and authorized signers. Route for approval: Collect signatures and approval evidence in sequence. Archive evidence: Preserve the completed record and audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Complete the procedure in signNow
Use this workflow to prepare, route, sign, and preserve the Confidential Informant Management And Control Procedures document without losing its approval history.
Upload form:
Upload the approved procedure PDF. Check fields:
Review detected fields and add missing signature dates. Assign recipients:
Assign each signer and approval role. Send document:
Send the controlled procedure through signNow. Archive record:
Store the signed PDF with its audit trail.
How the audit trail protects records
The audit trail records who handled the confidential procedure, what changed, when it happened, and how the completed evidence can be retrieved.
Authenticate signer:
Timestamp actions:
Hash document:
Seal record:
Log activity:
Retrieve evidence:
Recommended workflow configuration
Configure the confidential procedure around verified identities, restricted access, complete evidence, and the governing records schedule.
| Setting | Recommendation |
|---|---|
| Authentication and provisioning | Named users with two-factor authentication |
| Signature type | Intent-based electronic signature |
| Audit trail | Enabled with completion certificate |
| Document retention | Agency-approved records schedule |
| Encryption | TLS 1.2/1.3 and AES-256 |
Privacy and disclosure controls
Sensitive informant identifiers can appear in attachments or signature fields, exposing protected information to unauthorized recipients. Missing consent records can weaken proof that an informant understood electronic disclosures before signing controlled procedures. Broad workspace permissions may let staff download confidential procedures without a documented operational need. Forwarded signing links can expose confidential procedures when recipient identity is not independently verified.
Best practices for controlled procedures
A controlled workflow should preserve confidentiality, prove authorization, and keep every completed procedure understandable to an independent reviewer.
Separate identity from operational details
Document supervisory approval
Verify every authorized signer
Archive the complete evidence package
Document exclusions and state rules
Execution defect
Invalid electronic record
Filing rejection
Recording delay
Examples of controlled document workflows
These examples show how restricted routing and audit evidence can support confidential procedures without attributing unsupported outcomes to a named customer.
Investigative unit
A public-sector investigative unit needs signed handler certifications and supervisory approvals without circulating confidential procedures through ordinary email.
- Restricted recipients receive only assigned sections.
- Audit trail preserves approval sequence and timestamps.
The unit can keep the completed procedure, signer evidence, and review history together. Because no customer story identifies this exact confidential-informant form, the example remains an anonymized workflow rather than an attributed performance claim.
Legal services
A legal-services team coordinates sensitive authorization documents across attorneys, reviewers, and designated signers while limiting unnecessary exposure of informant information.
- Role-based routing separates preparation from approval.
- Signed records remain available for controlled review.
The team gains a repeatable way to route the document and preserve evidence of intent. Counsel should still confirm agency requirements, state-law obligations, and whether any underlying record requires wet-ink execution or an in-person notarization.
Security controls for sensitive records
Transport encryption:
Storage encryption:
Security certification:
Information security:
Health data controls:
Signer authentication:
Key performance indicators that demonstrate SignNow's proven track record.
Questions about completing this procedure
These answers address field preparation, authorization, electronic-signature eligibility, security, retention, and signNow plan considerations for this confidential document.
Upload the approved Confidential Informant Management And Control Procedures PDF, then use signNow’s field tools to review or add signature, date, initials, and approval fields. A completed audit trail supports evidence, but the agency must confirm the template is the authorized version.
Use signNow recipient roles and a controlled sending order to distinguish handler, supervisor, and signer actions. Business includes templates and audit trails; higher plans add capabilities such as advanced signer authentication, subject to plan configuration.
SignNow supports ESIGN and UETA-compliant electronic signatures, but those laws do not override agency policy, state requirements, or excluded records. Confirm that this procedure is eligible for electronic execution before sending it.
For sensitive records, require two-factor authentication where available and restrict workspace permissions to assigned personnel. HIPAA compliance requires a BAA when protected health information is involved; confidentiality alone does not make a record HIPAA-covered.
Export the signed document and audit trail together from the completed transaction. Preserve the files under the applicable agency schedule, litigation hold, or state requirement; signNow cannot determine the retention period for an investigative record.
The Business plan is listed at $8 per user per month with annual billing and includes legally binding eSignatures, audit trails, and templates. Confirm plan limits and invite usage before routing a high-volume confidential procedure.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.