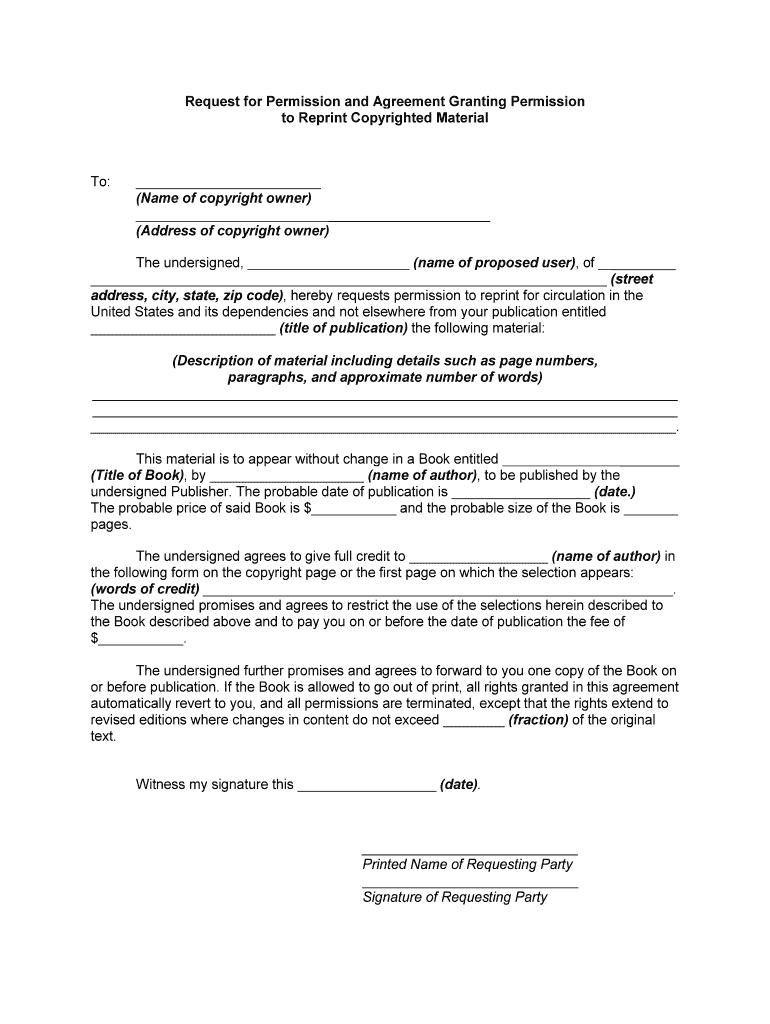
Request For Permission And Agreement Granting Permission Form
Use a Request For Permission And Agreement Granting Permission template to make your document workflow more streamlined.
What this permission agreement does
A Request For Permission And Agreement Granting Permission Form records a person’s authorization for a defined action, disclosure, access, or use. The sender should identify the parties, describe exactly what permission covers, state any limits or expiration, and obtain the signer’s consent. In signNow, upload the document, review or add fillable fields, assign recipients, and send it for signature. The completed agreement and audit trail preserve evidence of intent, signer activity, timestamps, and document completion. ESIGN and UETA may support electronic execution when applicable requirements are met, but exclusions and state rules still require review.
How this permission agreement works
A sender prepares the permission agreement in signNow, assigns its consent and signature fields, routes it to the named recipient, and preserves the completed record.
Prepare document: The sender uploads the permission agreement and checks its scope. Add fields: SignNow identifies fillable areas; the sender adds assigned fields. Collect consent: Recipients receive the agreement and authenticate before signing. Preserve evidence: The completed record and audit trail remain available for review.
Complete the permission agreement in signNow
Use this sequence to prepare the permission agreement, route it to the correct signer, and preserve evidence of completion.
Upload document:
Upload the permission agreement. Check fields:
Review detected fields and add missing signature, date, and consent fields. Assign recipients:
Assign each field to the correct recipient and set signing order. Send request:
Send the agreement through email or a signing link. Store evidence:
Review the signed document, certificate, and audit trail.
How the audit trail protects permission records
After the permission agreement is signed, signNow preserves technical evidence showing who acted, when they acted, and whether the record changed.
Authenticate signer:
Capture timestamps:
Hash document:
Seal record:
Log activity:
Retrieve audit trail:
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended permission agreement setup
Configure the agreement around signer identity, clear intent, documented activity, secure storage, and the retention rule applicable to its underlying transaction.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS OTP |
| Signature type | Intent-based electronic signature |
| Audit trail | Capture timestamps and signer actions |
| Document retention | Six years for PHI records under 45 CFR 164.530(j) |
| Encryption | TLS 1.2/1.3 and AES-256 protection |
Features for permission agreements
SignNow connects the permission agreement’s fields, recipients, authentication, signatures, and evidence in one documented workflow.
Reusable template
Upload this permission agreement, place signature and date fields, and reuse the prepared template without recreating the document for each recipient.
Audit trail
Capture signer identity, actions, timestamps, and completion evidence in one audit trail tied to the permission agreement.
Flexible delivery
Send the agreement by email or signing link when recipients are outside the organization and do not need a signNow account.
Mobile signing
Collect signatures from desktop or mobile devices when permission must be granted during a site visit, appointment, or remote review.
Signer verification
Use SMS authentication or other configured verification when the permission involves sensitive personal information or controlled disclosure.
Document history
Keep the signed agreement and completion certificate available for later authorization, compliance, or record-management review.
Platform requirements for signing
Use signNow with Chrome, Firefox, Safari, or Edge on Windows or macOS. Mobile access is available through iOS and Android apps, while TLS 1.2/1.3 protects data in transit.
Browser support Chrome, Firefox, Safari, and Edge Operating systems Windows, macOS, iOS, and Android Secure connection TLS 1.2/1.3 protects data in transit
Organizations handling permission agreements should manage access on approved devices and preserve exported records in controlled storage. Enterprise deployments may configure API access, SSO provisioning, and stronger signer authentication according to internal policy and the sensitivity of the permission being granted.
Signer authentication and certificates
PKI:
X.509 certificates:
Two-factor authentication:
SMS OTP:
ID verification:
Signer attribution:
Retention practices for permission agreements
Retain the signed permission agreement and its evidence according to the transaction, industry rule, state law, and any stated expiration date.
Apply the correct retention rule
Export the audit trail
Archive securely
Track scope and expiration changes
Risks of incomplete permission records
Intent dispute
Identity dispute
Evidence gap
Privacy exposure
Privacy and disclosure pitfalls
Leaving recipient names, disclosure scope, or expiration dates unclear can undermine proof that the signer authorized this specific permission request. Including unnecessary health, financial, or identifying information increases exposure if the signed agreement is shared beyond its intended recipient. Sending the agreement to an unverified email address can connect the permission to the wrong person and weaken signer attribution. Failing to preserve the completed agreement and audit trail makes later review of consent, timing, and document integrity more difficult.
Troubleshooting permission agreements
Resolve field, authentication, consent, compliance, and retention questions before sending this permission agreement for signature.
Upload the completed permission agreement to signNow, place required fields, and confirm each recipient before sending. Business includes templates and audit trails; Business Premium adds bulk send. Review consent language before requesting signatures.
A permission agreement can generally use an electronic signature when the signer demonstrates intent, consents to electronic records, and the record remains reproducible. ESIGN, 15 U.S.C. chapter 96, and applicable UETA rules govern the electronic transaction; state exclusions still apply.
Business costs $8 per user monthly when billed annually and includes legally binding eSignatures, templates, audit trails, and mobile apps. Paid plans include 100 signature invites per user annually; overage fees can apply.
For PHI, select a signNow plan with HIPAA coverage and execute the required business associate agreement. HIPAA compliance does not replace obtaining valid permission, limiting disclosure, or following the covered entity’s privacy procedures.
If a signer cannot open the request, verify the email address, resend the invitation, or use a controlled signing link. SMS authentication is available for stronger verification; the audit trail records delivery, authentication, signing, and completion events.
SignNow records the signed agreement, completion certificate, timestamps, signer activity, and audit trail. Export the completed record and preserve it under the organization’s retention policy; the platform’s storage period does not determine a legal retention period.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.