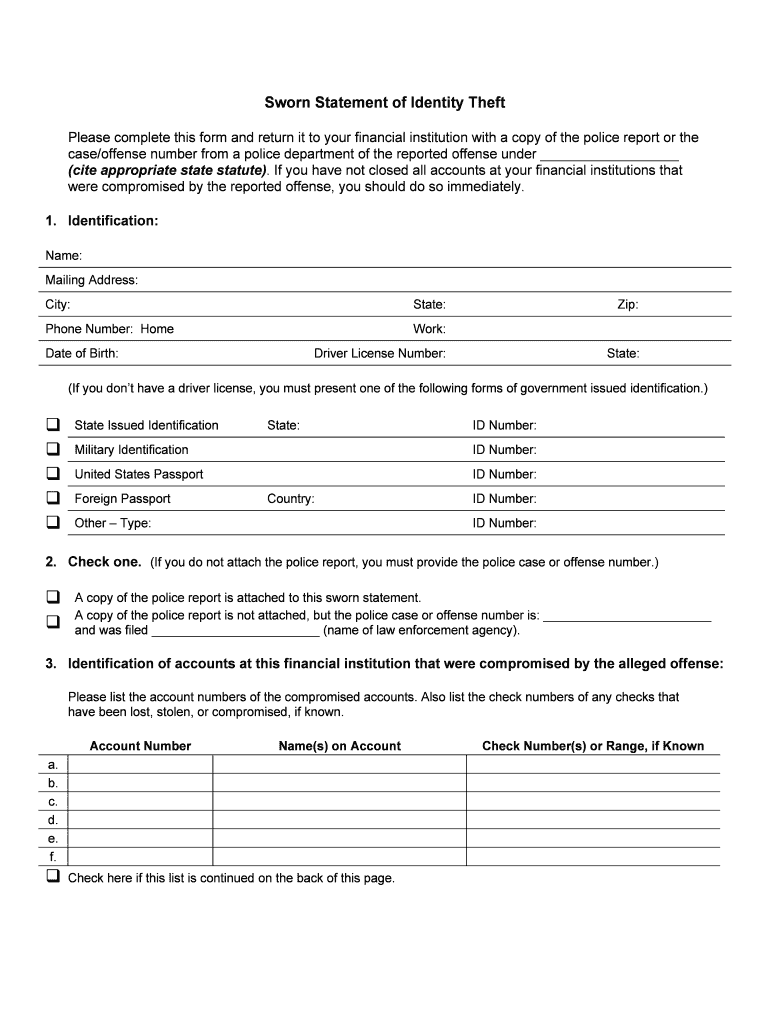
Sworn Statement Of Identity Theft Financial Institutions Form
Use a Sworn Statement Of Identity Theft Financial Institutions template to make your document workflow more streamlined.
What this identity theft statement does
A Sworn Statement Of Identity Theft Financial Institutions Form records a person's formal declaration that identity theft affected a financial account or transaction. The signer identifies themselves, describes the suspected misuse, lists affected institutions or accounts, and confirms the facts under oath or certification. Financial institutions may use the statement when investigating unauthorized activity, reviewing liability, or requesting supporting records. The exact wording, notarization requirement, and submission method depend on the institution and applicable state law. signNow can organize the document, collect signatures, and preserve its completion history.
Legal standing of the signed statement
A signed Sworn Statement Of Identity Theft Financial Institutions Form can provide evidence of the declarant’s account and intent when the signer consents, the record is attributable, and the completed document remains reproducible. ESIGN and applicable UETA provisions support electronic records, but they do not override notarization, institutional, state-law, or excluded-document requirements.

Complete the identity theft statement online
Use this focused workflow to prepare, sign, and preserve a Sworn Statement Of Identity Theft Financial Institutions Form in signNow.
Upload form:
Upload the completed identity-theft statement. Check fields:
Review detected fields and add missing signer fields. Send statement:
Send the statement to the required signer. Store record:
Collect signatures and download the completed record.
What the audit trail records
The signNow audit trail documents the events connecting the signer, the identity-theft statement, and the completed electronic record.
Authenticate signer:
Capture timestamp:
Track document history:
Record attribution:
Retrieve audit trail:
Export evidence:
Choose a signing method for this statement
- Use the web app to upload the Sworn Statement Of Identity Theft Financial Institutions Form, place fields, and send it when preparing a controlled investigation workflow from a desktop browser.
- Use the signNow mobile app when investigators or account holders need to review and sign the statement from an iOS or Android device away from the office.
- Use kiosk mode for supervised signing at a branch or service desk when one device is shared and each signer must complete a separate statement.
- Generate a shareable signing link when a financial institution needs a controlled link for repeated statement intake, while verifying the recipient before distributing sensitive information.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Features for identity theft statements
signNow combines field placement, signer routing, authentication, audit trails, and mobile access for financial-institution identity-theft documentation.
Field placement
Upload the statement and place signer, date, initials, and acknowledgment fields without rebuilding the document from scratch.
Remote sending
Send the completed statement to the identified signer by email or a controlled signing link for remote review.
Audit trail
Capture signer actions, timestamps, and document history in an audit trail supporting later investigation and record review.
Signer verification
Use SMS authentication or other configured verification when the institution requires stronger evidence connecting the signer to the statement.
Mobile access
Access the workflow through signNow mobile apps when an account holder or investigator must sign away from a desktop.
Record storage
Store the executed statement with its completion records so investigators can retrieve the evidence package when needed.



Security protections for identity theft forms
Encrypted transmission:
Stored encryption:
Security certification:
Healthcare compliance:
Transport security:
Audit evidence:
Recommended workflow setup
Configure the statement workflow around signer attribution, controlled access, audit evidence, and the financial institution’s retention instructions.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS verification |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Capture timestamps, actions, and signer evidence |
| Document retention | Follow institution and applicable law |
| User provisioning | Assign role-based access to investigators |
Retention rules for related records
No universal federal retention period applies to every identity-theft statement; retain it according to the institution, record category, and applicable authority.
Institution-defined retention period
Three years for tax records
Six years for HIPAA records
Six years for broker records
Longer applicable requirement
Record-keeping practices for identity theft statements
Preserve the statement as an investigative record, with controlled access, a complete audit trail, and retention decisions tied to the underlying financial matter.
Apply the institution’s retention instruction
Export the audit trail
Restrict sensitive account information
Verify every factual assertion
Risks of an incomplete statement
Submission rejection
Incomplete facts
Signer attribution
Lost audit evidence
Privacy and disclosure pitfalls
Unredacted account numbers can expose sensitive financial information when statements are shared with investigators, vendors, or unrelated recipients. Missing consent evidence can complicate electronic delivery when a consumer-facing workflow requires paper-record disclosures under 15 U.S.C. §7001(c). Overbroad permissions can expose identity-theft statements to staff without an investigative or account-servicing need. A statement sent before account details are verified can preserve inaccurate allegations and delay the institution’s investigation.
Troubleshooting identity theft statements
Resolve signer, plan, authentication, and compliance questions before submitting a Sworn Statement Of Identity Theft Financial Institutions Form to a financial institution.
Business includes legally binding eSignatures, templates, audit trails, and mobile apps. Upload the statement, place required signer fields, and send it through the workflow. Confirm whether the receiving institution requires notarization or an original paper record before relying on electronic delivery.
Business includes 100 signature invites per user annually when billed annually, with overage fees applying after the included allotment. Business Premium adds bulk send. Review your expected statement volume before choosing a subscription plan.
Use Business Premium for repeated statement packages because its documented plan features include bulk send. Create one approved template, map signer fields, and send individualized copies. Confirm each recipient's account details before distributing identity-theft records.
signNow identifies completed signing activity through audit trails and timestamps, while ESIGN and UETA establish electronic-signature validity when intent, consent, attribution, and record retention requirements are satisfied. State law and the financial institution's policy may impose additional requirements.
A financial institution may require notarization, identity proofing, or an original document even when electronic signatures are legally recognized. Check the institution's instructions and applicable state law before sending a signed statement through signNow.
HIPAA applies only when the statement or related workflow contains protected health information and the covered entity has an appropriate business associate arrangement. signNow lists HIPAA compliance with a BAA required; unrelated banking records do not become HIPAA records automatically.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.