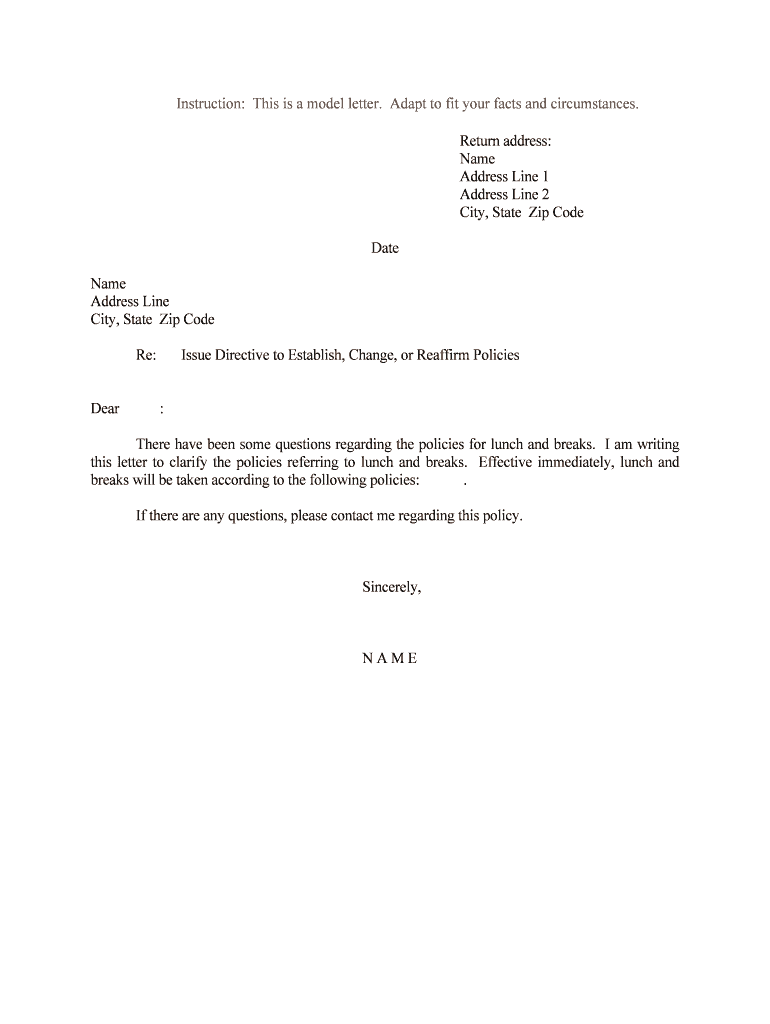
Issue Directive To Establish, Change, Or Reaffirm Policies Form
Use a Issue Directive To Establish, Change, Or Reaffirm Policies template to make your document workflow more streamlined.
What this policy directive form does
The Issue Directive To Establish, Change, Or Reaffirm Policies Form records an organization’s decision to create, revise, or continue a stated policy. The completed document identifies the policy action, supporting rationale, responsible participants, effective details, and approvals supplied by the organization. With signNow, a sender uploads the directive, maps or adds fillable fields, sends it to designated signers, and receives a completed copy with an audit trail. ESIGN and applicable state electronic-transactions law can support electronic records when intent, consent, attribution, and reproducibility are established.
Business types that benefit from this form
The form helps organizations establish, change, or reaffirm written policies with identifiable approvals and a retrievable electronic record.
Solo professional-services firms can use the form to document internal operating policies, obtain owner approval, and preserve a signed record without coordinating a large administrative team. Healthcare practices can issue or reaffirm privacy, consent, and records-handling policies, then route approvals through signNow with authentication and an auditable completion history. Multi-location enterprises can standardize policy directives across departments, use reusable signNow templates, and assign delegated sending while preserving controlled access and consistent approval evidence.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Who can use this form
Business teams
Policy directives, employee acknowledgments, confidentiality agreements, and operating procedures can be routed to staff, managers, contractors, or executives for documented approval.
Regulated industries
Healthcare, finance, legal, construction, and education organizations can adapt the workflow to their policy records, subject to industry rules and state-specific requirements.
Features that clarify policy approval
signNow combines document preparation, controlled approval routing, authentication, and audit evidence for this policy directive workflow.
Reusable templates
Upload the directive, map fields, and create a repeatable signing package so policy approvals use the same document structure each time.
Signer routing
Route the directive to named approvers in the required order, reducing uncertainty about who reviewed or accepted each policy change.
Audit trail
Capture timestamps, signer actions, and completion evidence with the signed policy, supporting later review of how the directive was approved.
Signer verification
Use email links, SMS authentication, or other available signer controls to connect each approval with the intended recipient.
Secure records
Store completed directives with their audit evidence so authorized teams can retrieve the approved policy during audits or internal reviews.
Business integrations
Connect policy approvals with Salesforce, Microsoft 365, NetSuite, or Google Drive to reduce manual copying between business systems.
How the directive workflow works
Use this sequence to turn the policy directive into a controlled, reviewable electronic approval record.
Upload: Upload the completed Issue Directive To Establish, Change, Or Reaffirm Policies Form to signNow. Prepare: Review detected fields and add policy-specific approvals, dates, initials, or signature fields. Route: Send the directive to named approvers in the required organizational sequence. Store: Collect signatures and retain the completed directive with its audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
What the audit trail records
The audit trail documents the approval event itself, giving reviewers evidence beyond the visible signature placed on the policy directive.
Authenticate signer:
Capture timestamp:
Protect document:
Seal record:
Export evidence:
Review history:
Recommended setup for policy approval
Configure the directive around identifiable signers, reproducible records, controlled access, and the retention rule governing the organization’s policy files.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS verification |
| Signature type | Electronic signature with signer intent |
| Audit trail | Retain the completion certificate |
| Document retention | Apply the governing record rule |
| Encryption | TLS 1.2 or TLS 1.3 transmission |
Ways to send and sign the directive
- Use the signNow web app when policy owners need to upload the directive, place fields, review recipients, and monitor completion from a central workspace.
- Use the signNow mobile app when an authorized policy approver must review or sign from an iOS or Android device away from the office.
- Use kiosk mode when multiple people approve a directive at a controlled workstation, with the organization managing the device and signer sequence.
- Use a shareable signing link when a defined policy audience needs access through a controlled distribution channel rather than individually addressed email invitations.



Security controls for signed directives
TLS 1.2 and TLS 1.3:
AES-256 at rest:
SOC 2 Type II:
ISO 27001:
HIPAA with BAA:
ESIGN and UETA:
Privacy pitfalls in policy directives
Including employee names, medical details, or confidential business information exposes data to recipients who may not need access to the directive. Sending the directive before recording electronic consent can weaken evidence that a consumer knowingly accepted electronic delivery or signing. Leaving shared templates open to every user can let unauthorized staff alter policy language or route approvals without administrator review. Using one broad recipient group instead of role-based access can disclose a policy draft before its approval sequence is complete.
Best practices for policy records
Clear versioning, authority-based retention, audit evidence, and controlled archival make signed policy directives easier to review and reproduce.
Identify each policy version before sending
Preserve the audit trail with the directive
Apply the controlling retention rule
Limit access after policy approval
Legal standing for business use
A signed policy directive may provide evidence when the record shows signer intent, electronic consent, attribution, and reliable retention and reproduction under ESIGN, 15 U.S.C. ch. 96, and applicable UETA or New York ESRA rules. Those frameworks exclude wills, certain court orders, and specified family-law documents.

Documents outside this workflow
State acknowledgment
Wills and codicils
Court orders
Real-estate deeds
Troubleshooting policy directive workflows
Resolve field, authentication, consent, plan, and compliance questions before sending this policy directive for approval.
signNow’s Business plan includes templates and audit trails for policy directives. Confirm the uploaded file is readable, then use the editor to add missing signature, date, or approval fields before sending.
The Business plan is listed at $8 per user monthly with annual billing. It includes 100 signature invites per user annually; overage charges can apply, so monitor usage for recurring policy campaigns.
Use signNow’s available signer authentication controls, such as SMS verification where enabled, and retain the completed audit trail. Authentication supports attribution but does not replace required organizational approval procedures.
For consumer-facing electronic records, ESIGN requires disclosure of the right to paper records, electronic-access capability, and procedures for withdrawing consent under 15 U.S.C. §7001(c). Configure and document that process separately.
signNow states that its ESIGN and UETA compliance supports electronic signatures and records. The organization must still confirm that this policy directive is not being used for an excluded document, such as a will or court filing.
If the directive contains protected health information, signNow identifies HIPAA compliance as requiring a business associate agreement. Execute the BAA and limit access before routing the policy to healthcare signers.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.