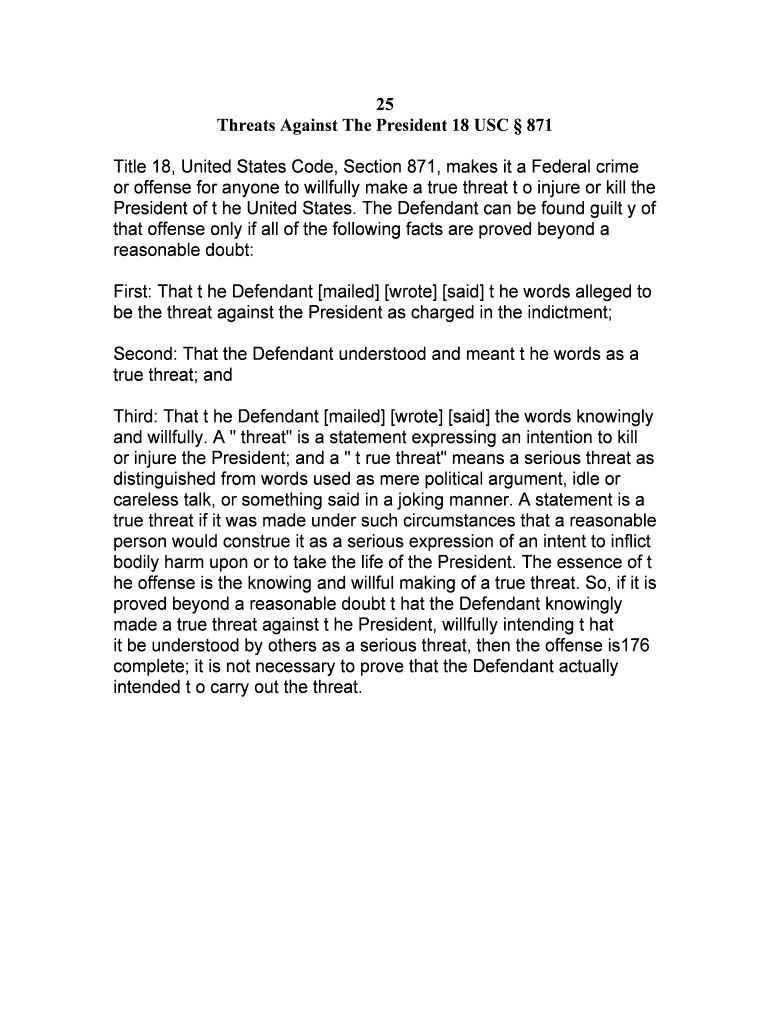
18 U S Code871 Threats Against President And Successors Form
Use a 18 U S Code871 Threats Against President And Successors template to make your document workflow more streamlined.
What this document represents
This title does not identify a verified federal form. In the U.S. Code, 18 U.S.C. §871 addresses threats against the President, the President-elect, and certain successors; it is a criminal statute rather than a standardized form with published fields or a routine filing deadline. Before completing or signing a document using this title, confirm its issuing authority, purpose, required recipients, and submission rules. signNow can upload the supplied file, detect fillable fields, route signatures, and preserve an audit trail, but it cannot establish that the document is an official §871 filing or replace a required government process.
Who should verify and use it
Government offices
Government and law-enforcement offices should first verify whether this document is an internal acknowledgment, an investigative record, or an official submission. The title alone does not establish a required signer, agency, or filing procedure under 18 U.S.C. §871.
Legal services
Legal teams can use signNow to circulate a supplied document for review or acknowledgment when electronic signing is permitted. They should preserve the source, recipient instructions, and audit trail, while confirming that no court or agency filing must occur separately.
Organizations that may handle this document
The document’s title suggests a government or legal context, but its official issuer, required audience, and filing purpose must be confirmed before use.
Federal agencies and law-enforcement offices can use a controlled workflow to collect acknowledgments or internal approvals, but must confirm the document’s official authority and submission channel first. Legal services firms can prepare client-facing acknowledgments or supporting records, using signer assignment and audit trails while avoiding any claim that the file itself replaces a court filing. Security and compliance teams can route sensitive internal records through controlled access, preserving authentication details and completion evidence for authorized review without treating the document as an official statutory form.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
How to prepare this document
Use this workflow only after confirming that the document is authentic, complete, and intended for electronic signature.
Verify source:
Confirm the document’s official source and intended recipient. Upload document:
Upload the provided document to signNow. Check fields:
Review detected fields and add missing fields. Assign signers:
Assign each signature field to the correct signer. Complete record:
Send, complete signing, and download the record.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
What the audit trail records
The audit trail documents who interacted with this file, when actions occurred, and how the completed record can be retrieved.
Signer authentication:
Timestamp capture:
Document hashing:
Tamper evidence:
Action history:
Audit export:
Recommended workflow configuration
Confirm the document’s legal source first, then configure signing and access controls around the issuing authority’s requirements.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS authentication |
| Signature type | Intent-based electronic signature |
| Audit trail | Complete timestamped completion record |
| Document retention | Follow the issuing authority’s written policy |
| Encryption and access | TLS 1.2 or 1.3 with AES-256 |
Features for handling this document
signNow provides a controlled document workflow, while official-source verification and any government or court filing requirements remain separate responsibilities.
Source preservation
Upload the supplied document and preserve its original version before adding fields, creating a clear reference copy for later review or correction.
Field review
Use field detection as a starting point, then check every signature, date, initials, and text field against the provided document.
Signer assignment
Assign each field to a named recipient so the completed record shows who was expected to provide each signature or response.
Audit evidence
Route the document through signNow and capture timestamps, signer actions, delivery events, and completion evidence in the audit trail.
Data protection
Protect the file with TLS 1.2 or 1.3 in transit and AES-256 at rest under signNow’s documented controls.
Controlled export
Download the completed document and audit record, then follow the verified agency or legal recipient’s separate submission instructions.
Security controls for this document workflow
Transport encryption:
Stored encryption:
Security certification:
Information security:
Privacy framework:
Signature compliance:
Platform requirements for document signing
Access the document through Chrome, Firefox, Safari, or Edge on Windows, macOS, iOS, or Android. signNow encrypts transmitted data with TLS 1.2 or 1.3, and mobile apps are available for supported Apple and Android devices.
Supported browsers Chrome, Firefox, Safari, Edge Operating systems Windows, macOS, iOS, Android Supported devices Desktop and mobile browser access
Organizations should use managed devices, approved browsers, and controlled accounts when this document contains sensitive threat-related information. Administrators can also evaluate API access, SSO provisioning, signer authentication, and certificate or long-term-validation requirements before deploying the workflow across teams.
Challenges when preparing this document
The supplied title does not identify an official government form, making the correct source, fields, signer, and submission destination difficult to confirm. 18 U.S.C. §871 describes a criminal offense, not a standard template, so users may mistake a private document for an official filing. Threat-related records can contain sensitive personal information, requiring careful access controls, recipient verification, and secure storage before circulation. An electronic signature may document agreement, but it does not replace any required law-enforcement, court, or agency process.
Risks requiring careful verification
Unverified form source
Misrouted submission
Incomplete audit trail
Improper electronic use
Legal standing and source verification
ESIGN and UETA can support electronic signatures when intent, consent, attribution, and record retention are established. They do not transform 18 U.S.C. §871 into a form or authorize electronic filing. Wills, court filings, and other statutory exclusions require separate legal review and may need paper or in-person procedures.

Troubleshooting this document workflow
These answers address source verification, field setup, electronic-signature limits, security, and signNow plan capabilities for this specific document title.
If the file cannot be matched to an official agency source, do not infer its validity from the title. signNow Business can store the supplied document and audit activity, but source verification must come from the issuing agency or qualified counsel.
If signNow does not detect fields, use the editor to place signature, date, initials, or text fields manually. Confirm every field against the source document before sending, because automatic detection does not determine legal completeness.
If a recipient questions electronic signing, review ESIGN and applicable state law, including UETA or New York ESRA. signNow Business provides audit trails, while the parties must confirm consent and any required paper or in-person process.
If the document contains sensitive threat-related information, restrict recipients and use appropriate authentication. signNow supports encryption in transit and at rest; HIPAA or another specialized framework applies only when the underlying record falls within that framework.
If the completed file must be submitted to an agency or court, download the signed document and completion record, then follow that recipient’s instructions. A signNow workflow does not itself prove that electronic delivery satisfies the agency’s filing rules.
Business Premium includes bulk send, while Enterprise adds advanced signer authentication. Select a plan based on the actual workflow; the plan does not determine whether a document titled under 18 U.S.C. §871 is officially valid.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.