18 U S Code912 Officer Or Employee Of The United States Form
Use a 18 U S Code912 Officer Or Employee Of The United States template to make your document workflow more streamlined.
What this document represents
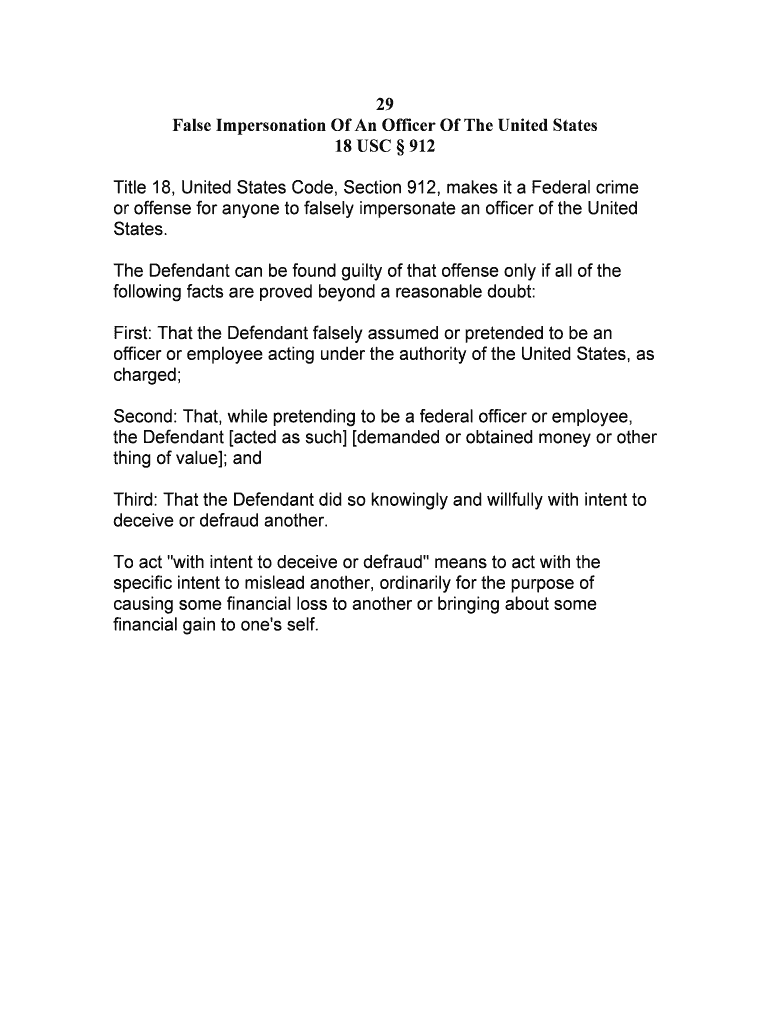
The 18 U S Code912 Officer Or Employee Of The United States Form is not identified in the supplied authorities as a standardized federal form; it is a document label referencing 18 U.S.C. § 912. That statute addresses falsely pretending to be an officer or employee acting under U.S. authority, or demanding or obtaining money, paper, document, or thing of value through that pretense. A signer should verify the document’s issuing source, legal purpose, authority, and required submission method before signing. Electronic signing may be appropriate only when the underlying transaction permits it under ESIGN, UETA, and applicable state law.
Who may handle this document
Government and compliance
Government counsel, inspectors, and compliance teams can use a clearly identified document workflow when an agency-approved record requires signatures, acknowledgments, or controlled distribution.
Legal and business
Legal departments and authorized business representatives can route related acknowledgments, while confirming that no signer misrepresents federal office or authority under 18 U.S.C. § 912.
How to process the document
Use a controlled sequence that separates document preparation, signer verification, execution, and record preservation.
Upload document: Upload the document and inspect its title, authority, and required fields. Add fields: Place fields only for authorized signers and required acknowledgments. Send securely: Send through signNow after confirming recipients and authentication. Archive record: Complete signatures, then preserve the signed file and audit trail.
Privacy and disclosure risks to review
Uploading an unredacted document can expose personal identifiers, addresses, or agency-related details to unintended recipients. Sending without documented electronic consent may weaken evidence that the signer agreed to receive and sign records electronically. Assigning broad workspace permissions can let unauthorized users view, edit, or send the completed document. Using an open signing link without identity checks can make signer attribution harder to establish during a dispute.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
How the audit trail preserves evidence
signNow records identity and document events so the completed file can be reviewed alongside its signing history.
Authenticate signer:
Capture timestamps:
Hash document:
Seal document:
Record activity:
Retrieve evidence:
Recommended workflow controls
Use these controls to document signer intent, protect the file, and preserve evidence without asserting authority the record cannot establish.
| Setting | Recommendation |
|---|---|
| Authentication method | SMS OTP for external signers |
| Signature type | Electronic signature with explicit intent |
| Audit trail | Enabled with completion certificate |
| Document retention | Apply the underlying statutory rule |
| Encryption | TLS 1.2/1.3 and AES-256 at rest |
Signer authentication and certificate options
Email authentication:
SMS two-factor:
Identity verification:
PKI certificates:
X.509 certificates:
Audit trail:
Retention periods for related records
Retention depends on the record’s legal category; apply the rule governing the underlying transaction, not merely the signature date.
Three years after filing
Six years for major understatement
Indefinitely for fraud
Six years for HIPAA records
Three years for payroll records
Record-keeping practices for this document
Use the statutory authority and underlying transaction to determine review, signing, disclosure, and retention controls.
Verify authority before sending
Export the audit trail with the record
Apply the underlying retention rule
Restrict access to authorized personnel
Legal and evidentiary risks
Document rejected
Criminal exposure
Evidence challenged
Privacy complaint
Questions about signing and compliance
These answers distinguish signNow workflow controls from the separate legal question of authority under 18 U.S.C. § 912.
signNow supports audit trails, timestamps, document history, and signer authentication. Those records can help establish intent and attribution under ESIGN and UETA, but they do not prove that a person lawfully held federal authority under 18 U.S.C. § 912.
The Business plan includes legally binding eSignatures, audit trails, templates, mobile apps, ISO 27001, SOC 2, GDPR, and a $8/user/month annual price. Confirm the plan’s current invite allowance before sending repeated document batches.
Use SMS OTP or another available authentication method when email-only access does not adequately identify the signer. Stronger authentication supports attribution, but it cannot cure a false representation of government office or authority.
Consumer-facing electronic records may require disclosure of the right to receive paper, access to the electronic format, and procedures to withdraw consent under 15 U.S.C. §7001(c). Obtain legal review when this document reaches consumers.
A completed signature does not replace a required wet-ink signature, notarization, agency filing, or in-person procedure. Confirm the receiving agency’s instructions before treating a signNow-signed copy as sufficient.
Use role-based access and export the completed document with its audit trail. If the record contains personal information, restrict downloads and disclosures to authorized recipients and retain it under the rule governing the underlying record.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.