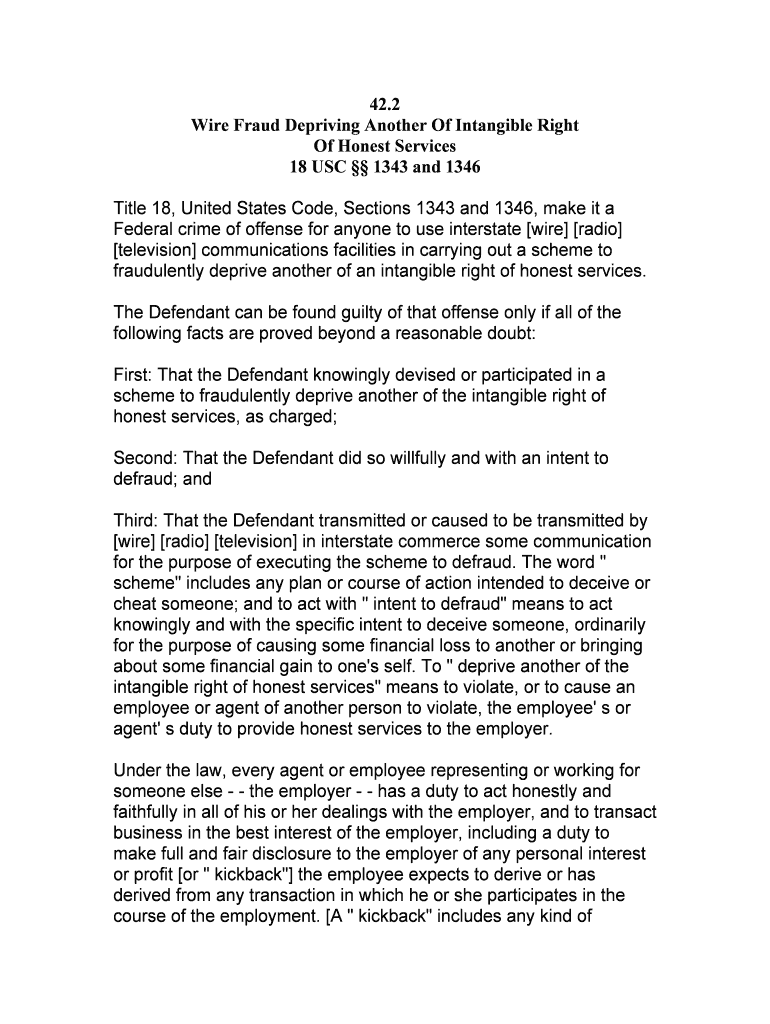
18 U S Code1346 Definition Of Scheme Or Artifice To Form
Use a 18 U S Code1346 Definition Of Scheme Or Artifice To template to make your document workflow more streamlined.
What this statutory definition means
18 U.S. Code § 1346 defines a scheme or artifice to deprive another of the intangible right of honest services. In practice, it applies to certain fraud prosecutions involving an employee, agent, or official who breaches a duty of loyalty through bribery or kickbacks. The definition expands the mail- and wire-fraud statutes; it does not create a standalone form or filing deadline. Courts interpret the provision with related federal fraud statutes, while prosecutors must establish the charged scheme and the required federal jurisdictional elements.
Who uses documents about this statute
Legal teams
Counsel can organize memoranda, acknowledgments, and engagement documents while preserving signer identity, timestamps, and the completed record.
Compliance teams
Compliance departments can document approvals, certifications, and internal reviews connected to anti-bribery and fiduciary-duty controls.
How to prepare and sign the document
Use this workflow for the specific agreement, acknowledgment, or compliance record associated with 18 U.S. Code § 1346.
Upload document:
Upload the relevant document to signNow. Check fields:
Review auto-detected fields and add missing signers, dates, or acknowledgments. Send for signature:
Send the document by email or a signing link. Preserve record:
Store the signed document with its audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Security controls for this legal document
Transport encryption:
Storage encryption:
Independent assurance:
Security certification:
Signature compliance:
Privacy frameworks:
Recommended signing workflow settings
Use identifiable signers, documented intent, controlled access, and a preserved audit trail for records concerning 18 U.S. Code § 1346.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Intent-based electronic signature |
| Audit trail | Capture IP, timestamps, and action history |
| Document retention | Follow the underlying record schedule |
| Encryption and provisioning | AES-256 with role-based access |
What the signNow audit trail records
The audit trail links signer actions, timestamps, document integrity, and the completed record for later review.
Authenticate signer:
Capture timestamp:
Hash document:
Seal record:
Attach certificate:
Export audit trail:
Best practices for documenting this matter
Accurate identity, clear authority, and an intact audit trail matter when documents may later be reviewed by counsel, auditors, investigators, or a court.
Document the transaction’s purpose and authority
Assign signer roles before sending
Capture informed electronic consent
Preserve the record and audit trail
Risks from incomplete documentation
Signer identity
Electronic consent
Record integrity
Approval authority
Challenges when documenting section 1346
Confusing the statutory definition with an official government form can lead to incorrect fields, unsupported filing assumptions, and incomplete legal documentation. Using a shared inbox or account can weaken attribution when several employees review or sign records concerning fiduciary duties. Sending a document without recording signer authority may leave later reviewers unable to connect the approval to the responsible person. Keeping only the signed PDF while losing its audit trail can make later verification of intent, timing, and document history more difficult.
Questions about preparing and signing this document
These answers distinguish the statutory concept from the documents used to record approvals, acknowledgments, investigations, or related business transactions.
18 U.S. Code § 1346 is a statutory definition, not an issued government form. Upload the actual agreement, acknowledgment, investigative record, or compliance document requiring signatures. signNow can detect fillable fields, route the document, and retain the completed record, but it does not determine whether conduct satisfies the statute.
Use signNow’s field editor to add the signer’s name, date, acknowledgment, and signature fields to the uploaded document. Review every field before sending. The Business plan includes templates and audit trails, while Business Premium adds bulk send for repeated document packages.
A signNow audit trail records signing events, timestamps, IP information, and document history. Under ESIGN and UETA, those records can help demonstrate intent, attribution, and record integrity. Legal admissibility remains a question for the applicable court and surrounding evidence.
For sensitive compliance records, use stronger signer authentication such as SMS OTP or available identity verification. signNow supports encrypted transmission with TLS 1.2/1.3 and encrypted storage with AES-256. Select controls based on the risk and the organization’s documented policy.
Consumer-facing electronic records may require an ESIGN disclosure explaining paper-record rights, electronic access, and withdrawal procedures under 15 U.S.C. § 7001(c). Add that language before sending and retain evidence of consent with the signed document and audit trail.
Business is listed at $8/user/month when billed annually, with a seven-day free trial and no credit card required. Business Premium is $15/user/month annually and includes bulk send. Plans include 100 signature invites per user per year, with overage fees.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.