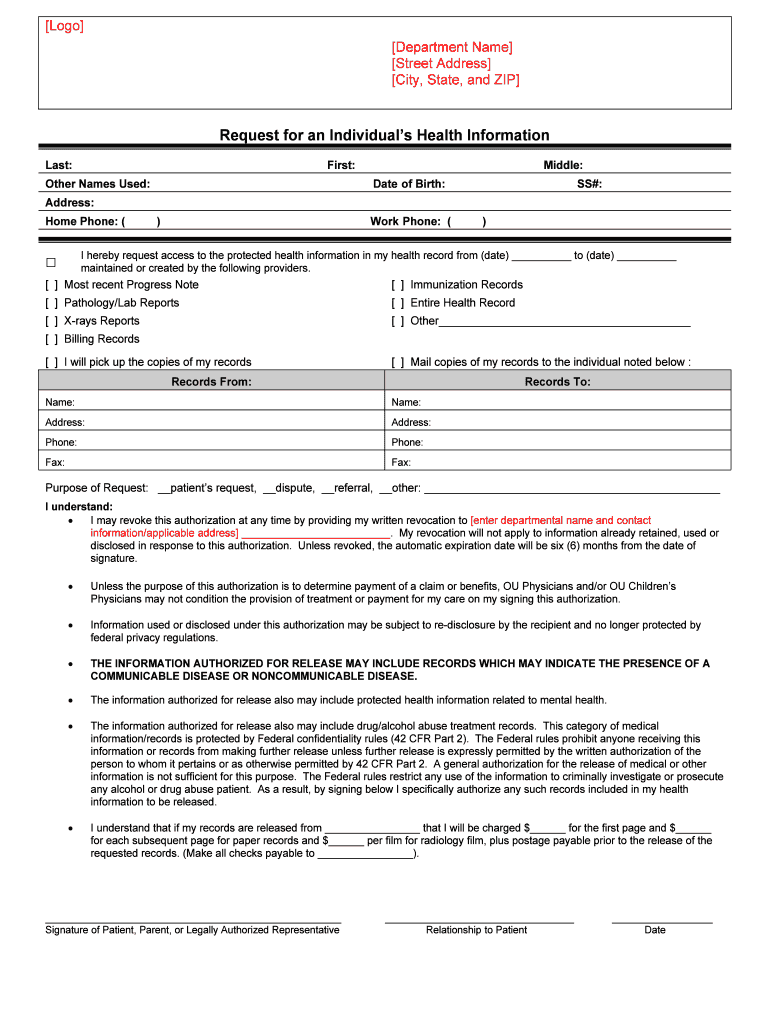
Protected Health Information Phi Arizona Department Of
Use a Protected Health Information PHI Arizona Department Of template to make your document workflow more streamlined.
What this protected information form does
Protected Health Information Phi Arizona Department Of is a health-information record used to document protected information and authorized handling or acknowledgment. In a signNow workflow, the sender uploads the form, reviews automatically detected fillable fields, assigns them to authorized recipients, and sends a secure signing request. Signers review the record, provide consent and an electronic signature, and receive a completed copy. signNow records timestamps, signer actions, and audit evidence. HIPAA-covered documentation generally requires six-year retention under 45 CFR 164.530(j).
Business types using this form
Healthcare organizations use Protected Health Information Phi Arizona Department Of when patient-facing records require controlled completion, electronic consent, and retained evidence.
Solo healthcare practices use Protected Health Information Phi Arizona Department Of to collect patient signatures without requiring every patient to return for an in-person appointment, while retaining a documented electronic record for authorized staff. Regional clinics route patient authorizations and administrative acknowledgments across locations, using role-based access and audit trails to show who signed each Protected Health Information Phi Arizona Department Of record. Enterprise healthcare systems connect high-volume form workflows to approved storage and business applications, supporting centralized permission management, retention controls, and consistent signer authentication across departments.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Legal standing and document limits
Protected Health Information Phi Arizona Department Of may be admissible when the signer’s intent, consent, identity, and record integrity are demonstrable through a reliable audit trail. ESIGN and UETA generally support electronic records, but wills, codicils, testamentary trusts, court orders, and official court filings remain excluded.

Features for protected health information
signNow combines field preparation, signer routing, authentication, audit evidence, and controlled storage for Protected Health Information Phi Arizona Department Of workflows.
Field detection
Upload Protected Health Information Phi Arizona Department Of and let signNow identify fillable areas before you review assignments and required fields.
Signer routing
Send the form to authorized recipients by email or signing link, reducing manual coordination while preserving the document’s intended signer order.
Audit evidence
Capture timestamps, authentication events, and activity history alongside the completed form for review of the signing process.
Signer verification
Use two-factor authentication and SMS OTP when stronger signer verification is required for health-information workflows.
Record retention
Keep the signed record and audit trail together so authorized teams can retrieve readable evidence during compliance reviews.
System integrations
Connect workflows with systems such as Google Drive, Box, Egnyte, Salesforce, NetSuite, or Microsoft 365 when approved by your organization.
Complete this form in signNow
Use a controlled workflow to prepare Protected Health Information Phi Arizona Department Of, route it to authorized signers, and preserve evidence of completion.
Upload:
Upload the Protected Health Information Phi Arizona Department Of file. Detect fields:
Let signNow detect fillable fields automatically. Assign signers:
Review fields and assign each authorized signer. Send:
Send the document for electronic signature. Store:
Store the completed form with its audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended protected information setup
Configure authentication, signatures, evidence, retention, and encryption before routing Protected Health Information Phi Arizona Department Of.
| Setting | Recommendation |
|---|---|
| Authentication method | Two-factor authentication with SMS OTP |
| Signature type | Intent-based electronic signature |
| Audit trail | Export with the completed record |
| Document retention | 6 years under HIPAA 45 CFR 164.530(j) |
| Encryption | TLS in transit and AES-256 at rest |
How the audit trail records each action
The signNow audit trail connects signer authentication, document integrity, timestamps, and retrieval evidence for Protected Health Information Phi Arizona Department Of.
Signer authentication:
Timestamp capture:
Document hashing:
Tamper-evident sealing:
Activity history:
Audit export:
Security controls for protected information
Health information protection:
At-rest encryption:
In-transit encryption:
Control assurance:
Security certification:
Signer verification:
Privacy and disclosure pitfalls
Sending Protected Health Information Phi Arizona Department Of to the wrong recipient can expose sensitive data and create an unauthorized disclosure event. Missing electronic-consent evidence may weaken proof that a patient or authorized representative agreed to receive and sign records electronically. Overbroad workspace permissions can let users view, download, or forward Protected Health Information Phi Arizona Department Of without a documented business need. A completed document without its audit trail may provide weaker evidence of signer identity, timing, and record integrity during a dispute.
Record retention and handling practices
Protect the completed form, its audit evidence, and its availability for the full period required by the applicable health-information rule.
Retain records for six years under HIPAA
Export the audit trail with each record
Use controlled archival storage for completed forms
Review access after every personnel change
Retention periods for related records
Apply the six-year HIPAA period when this record is documentation maintained by a covered entity or business associate; avoid importing unrelated retention rules.
Six years for HIPAA records
Three years for tax records
Not applicable to this form
Not applicable to this form
Not applicable to this form
Risks from incomplete handling
HIPAA exposure
Consent dispute
Integrity challenge
Proof limitation



Platform requirements for this form
Complete Protected Health Information Phi Arizona Department Of in signNow through a current desktop browser on Windows or macOS, or through the signNow mobile apps for iOS and Android. Use an encrypted connection and keep the device updated before accessing health information.
Desktop systems Windows and macOS Mobile apps iOS and Android Supported browsers Chrome, Firefox, Safari, Edge
Organizations handling Protected Health Information Phi Arizona Department Of should use managed devices, approved browser sessions, and controlled account provisioning. Confirm API, SSO, storage, and authentication requirements with the organization’s security policy before connecting signNow to systems such as Google Drive, Box, Egnyte, Salesforce, NetSuite, or Microsoft 365.
Key performance indicators that demonstrate SignNow's proven track record.
Protected health information form questions
These answers address field preparation, signer verification, HIPAA handling, retention, access problems, and plan capabilities for this form.
Upload the file again if field detection misses a signature area. Review the detected fields manually, add any missing fields, and assign each field to the authorized signer before sending the Protected Health Information Phi Arizona Department Of record.
A Business plan includes legally binding eSignatures, audit trails, templates, mobile apps, ISO 27001, SOC 2, and GDPR. HIPAA-compliant use requires a business associate agreement and an approved configuration for Protected Health Information Phi Arizona Department Of.
Use two-factor authentication or SMS OTP when email-only access does not provide sufficient assurance for the signer. Review the organization’s policy before sending Protected Health Information Phi Arizona Department Of to an external recipient.
Keep the completed document and its audit trail together. The audit trail helps show timestamps, signer actions, and authentication evidence, while HIPAA documentation retention generally requires six years under 45 CFR 164.530(j).
If a recipient cannot open the signing request, confirm the email address, resend the invitation, or provide a controlled signing link. Do not send Protected Health Information Phi Arizona Department Of as an unprotected email attachment.
Business Premium includes bulk send, while Enterprise adds advanced signer authentication and other capabilities. Select the plan based on the Protected Health Information Phi Arizona Department Of volume, authentication needs, and approved compliance requirements.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.