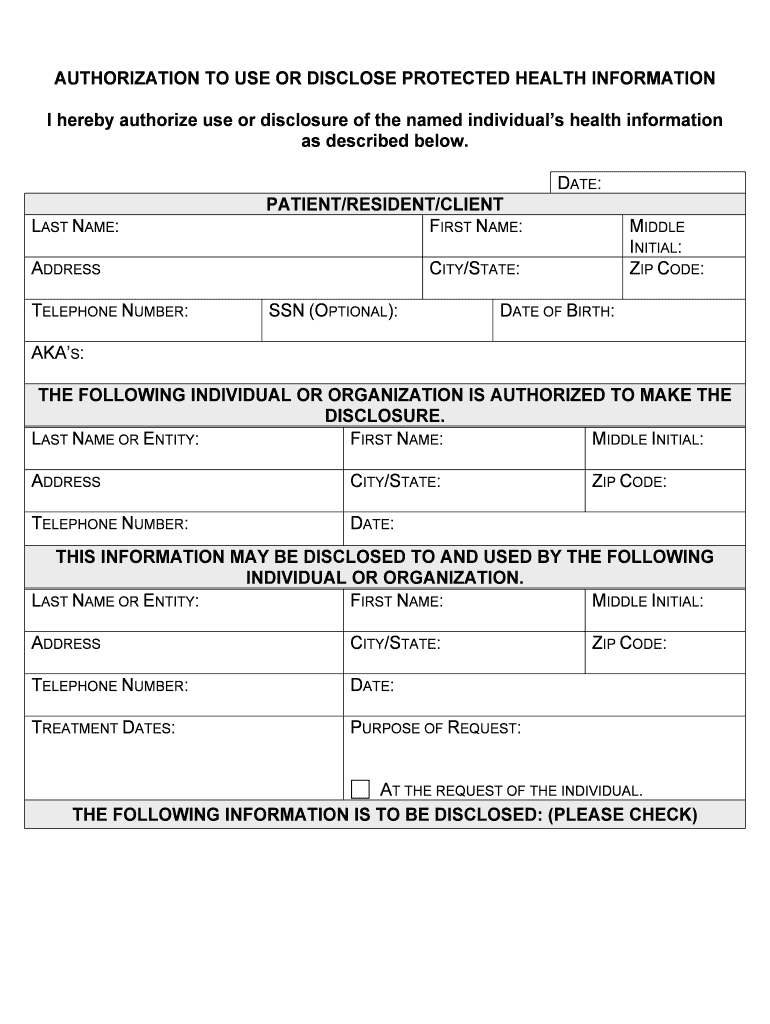
HIPAA Use And Disclose Protected Health Information
Use a HIPAA Use And Disclose Protected Health Information template to make your document workflow more streamlined.
What this HIPAA authorization does
A HIPAA Use And Disclose Protected Health Information form records a person’s permission to use or disclose specified protected health information. It identifies the individual, the information covered, the recipient, the purpose, and expiration or revocation terms. The authorization should be specific enough for the covered entity to determine what may be released and to whom. When completed electronically, signNow can capture the signature, authentication events, timestamps, document history, and Audit Trail. HIPAA requires covered entities to retain related documentation for six years under 45 CFR §164.530(j).
Organizations that use this form
The authorization is most useful where patient permission must precede a defined disclosure of protected health information.
Solo behavioral-health practices can use the authorization to document a patient’s permission before sending defined records to a family member, attorney, insurer, or another named recipient, while keeping the release scope visible to staff. Multi-site medical groups can standardize patient authorization templates, route signatures electronically, and preserve each completed disclosure record with its Audit Trail for records administration and compliance review. Enterprise health systems can connect authorization workflows to controlled repositories and identity processes, helping separate patient permission capture from downstream release review across departments, facilities, and business-associate relationships.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Complete this authorization in signNow
Use the original authorization fields to capture permission, scope, recipient details, signature, and supporting audit evidence.
Upload form:
Upload the authorization PDF. Detect fields:
Let signNow detect fillable fields. Assign roles:
Add the patient and recipient. Send request:
Send the authorization for signature. Archive record:
Store the signed PDF and Audit Trail.
Features for this HIPAA authorization
signNow connects the authorization’s patient-facing fields with signature capture, evidence, and controlled retention for the resulting disclosure record.
Patient consent
Capture the patient’s intent, signature, and authorization date in a structured electronic workflow, making the permission record easier to associate with the requested disclosure.
Defined scope
Specify the information categories, recipient, purpose, and expiration so staff can compare the proposed release against the authorization before sending records.
Field placement
Upload the existing authorization and use signNow’s field tools to add patient, representative, recipient, date, and signature fields without recreating the document.
Signer evidence
Use signer authentication options and event records to connect the completed signature with the patient or authorized representative who signed the form.
Audit evidence
Preserve the signed authorization alongside its Audit Trail, timestamps, and document history for later review of how permission was collected.
HIPAA controls
Use a HIPAA-compliant signNow configuration with a required BAA where applicable; the organization must still validate its own privacy and disclosure procedures.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.



Security for protected health information
HIPAA coverage:
Stored encryption:
Transport encryption:
Security reporting:
Information security:
Event evidence:
Platform requirements for signing
Complete this HIPAA authorization in a current Chrome, Firefox, Safari, or Edge browser using Windows or macOS. signNow also provides iOS and Android mobile apps for reviewing and signing the patient disclosure form.
Supported browsers Chrome, Firefox, Safari, and Edge Desktop systems Windows and macOS desktops Mobile access iOS and Android apps
Healthcare organizations should use managed devices, approved access controls, and appropriate identity procedures when handling this authorization. Enterprise deployments may also configure API access, SSO provisioning, and repository controls so completed forms and Audit Trails remain available only to authorized personnel.
What the authorization Audit Trail records
The Audit Trail supplies technical evidence showing how the patient authorization moved from signature request to completed record.
Authenticate signer:
Capture timestamp:
Hash document:
Seal document:
Record events:
Export evidence:
Retention schedule for this authorization
Use the HIPAA six-year rule as the federal baseline for this authorization and related privacy documentation, then check longer state requirements.
Six years: signed authorization record
Six years: privacy documentation
Six years: disclosure procedures
Six years: documented compliance actions
Six years: authorization audit evidence
Risks of incomplete HIPAA authorization
Unauthorized PHI release
Consent challenge
Evidentiary dispute
Privacy exposure
Key performance indicators that demonstrate SignNow's proven track record.
Troubleshooting this HIPAA authorization
These answers address field setup, patient authentication, HIPAA configuration, retention, and the legal evidence created when this authorization is signed electronically.
The Business plan includes templates and legally binding eSignatures, while HIPAA use requires the applicable signNow HIPAA configuration and a BAA. Confirm the account’s agreement before sending protected health information, rather than treating a signed form alone as proof of coverage.
Upload the original PDF again and use signNow’s field tools to place signature, date, and recipient fields. If auto-detection misses a field, manually position it and test the recipient routing before sending the patient authorization.
Use signNow authentication options such as SMS codes or stronger configured verification when the organization’s risk assessment requires more than an email link. Record the chosen method in the workflow policy and confirm the patient can complete it.
The HIPAA authorization should identify the information, recipient, purpose, and expiration or revocation terms. A generic signature request does not cure missing authorization language; have the covered entity’s privacy or legal team review the template.
Export the signed PDF and Audit Trail together after completion, then store them in an access-controlled repository. HIPAA requires related documentation to be retained for six years under 45 CFR §164.530(j).
Electronic execution can satisfy ESIGN and applicable state electronic-transaction rules when intent, consent, attribution, and record retention are established. HIPAA still controls whether the underlying disclosure is permitted and whether the authorization is valid.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.