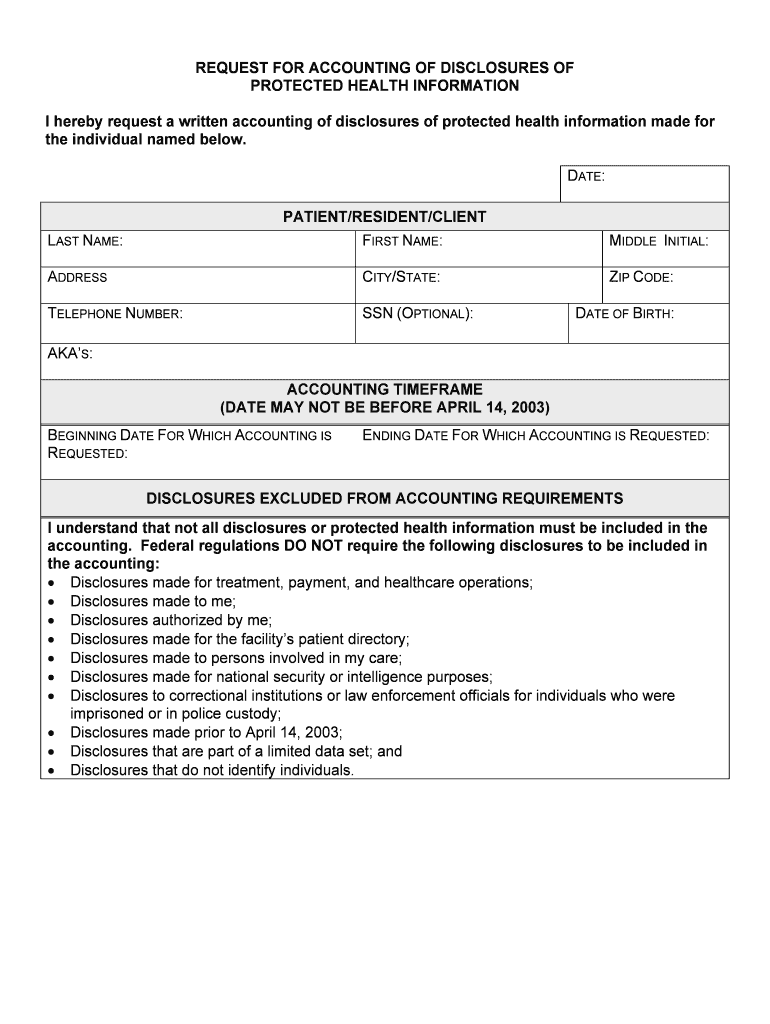
I Hereby Request A Written Accounting Of Disclosures Of Protected Health Information Made For
Use a I Hereby Request A Written Accounting Of Disclosures Of Protected Health Information Made For template to make your document workflow more streamlined.
What this disclosure request does
This form asks a covered entity or business associate to provide a written accounting of specified disclosures of protected health information. The requester should identify the individual, relevant period, disclosure scope, and authorized delivery recipient, then sign or otherwise authenticate the request according to the organization’s procedure. HIPAA’s accounting rules and exclusions determine what must be reported; the form itself does not automatically create a disclosure list. With signNow, staff can upload the document, review detected fields, route it for signature, and retain the completed request with an Audit Trail.
Who benefits from this request workflow
The form is most useful where healthcare records teams must authenticate requesters and preserve evidence for PHI disclosure-accounting duties.
Solo healthcare practices can use the request to collect a patient’s signed accounting inquiry and preserve the response record within one controlled workflow. Regional clinics can route requests among privacy officers, records staff, and authorized representatives while maintaining role-based access to protected health information. Enterprise health systems can standardize templates, authentication, Audit Trails, and retention processes across departments handling disclosure-accounting requests.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Documents and audiences for this request
Healthcare providers
Healthcare providers use this request for patient accounting inquiries, authorization records, and disclosure-related correspondence containing protected health information.
Privacy and records teams
Privacy officers and records teams use it to document scope, approvals, recipient identity, and retention evidence for a completed accounting request.
Features for protected health information requests
This workflow helps healthcare organizations collect, authenticate, document, and retain a request for an accounting of protected health information disclosures.
Structured fields
Upload the request document and place fields for the patient, authorized representative, privacy officer, and completion date so each required response is captured in the correct location.
Directed routing
Send the accounting request to the appropriate healthcare privacy contact or authorized representative without requiring paper delivery, while preserving the document’s signing sequence.
Audit evidence
Capture signer identity, timestamps, IP details, and document activity in an Audit Trail that supports review of how the request was completed.
Signer verification
Use signer authentication options such as SMS OTP when the request contains protected health information and identity verification needs additional assurance.
Controlled storage
Keep the completed request and supporting disclosure accounting in a controlled signNow workspace, with access limited according to the covered entity’s privacy procedures.
Safer delivery
Send the completed request or accounting record to approved recipients through a documented workflow, reducing accidental disclosure of protected health information.
How this disclosure request works
The request moves from document preparation to authenticated completion, with the signed record and Audit Trail retained for authorized healthcare review.
Upload document: Upload the accounting request document. Review fields: Auto-detect fillable fields, then review them. Send request: Send to the authorized signer or recipient. Store evidence: Complete, sign, and retain the record.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended workflow configuration
Configure authentication, evidence capture, retention, and access controls around the PHI disclosure-accounting process.
| Setting | Recommendation |
|---|---|
| Authentication method | SMS OTP for external signers |
| Signature type | Typed or drawn eSignature |
| Audit trail | Export with completed request |
| Document retention | 6 years under HIPAA 45 CFR 164.530(j) |
| Encryption | TLS 1.2/1.3 and AES-256 encryption at rest |
What the signNow Audit Trail records
The Audit Trail documents the technical history of this PHI disclosure request, separate from the form’s preparation and routing steps.
Authenticate signer:
Capture timestamp:
Track document activity:
Seal completion:
Preserve history:
Export audit trail:
Security controls for PHI requests
HIPAA protection:
Independent assurance:
Security certification:
Stored data:
Transport security:
Privacy controls:
Privacy pitfalls in disclosure accounting
Including unnecessary clinical details can expose protected health information beyond the disclosure-accounting scope requested by the patient. Sending the completed accounting to an unverified email address can disclose protected health information to the wrong recipient. Failing to capture authorization or identity evidence can make it difficult to show that the requester was entitled to receive the accounting. Leaving completed requests in shared folders without role-based permissions can expose disclosure histories to unauthorized workforce members.
Risks of mishandling the request
Incomplete accounting
Unauthorized access
Missing evidence
Retention failure
Record-keeping practices for this request
Keep the request, accounting response, and signing evidence together so authorized staff can verify disclosures and meet HIPAA record-retention duties.
Apply the six-year HIPAA retention period
Export the complete audit trail
Restrict access to protected information
Archive originals with dates
Rollout and retention for this request
Use a controlled rollout for this PHI request, then retain the completed record and supporting evidence under the applicable healthcare privacy policy.
Prepare request:
First send:
Team onboarding:
Six-year retention:
Audit export:
Access review:
Policy check:
Final archive:



Relevant signNow customer examples
Healthcare organizations and distributed teams can adapt signNow workflows for controlled requests, while verifying their own HIPAA obligations and authorization rules.
Healthcare provider
Fertility Centers of Illinois needed a responsive way to manage healthcare documents and protected information across its patient workflows.
- Healthcare privacy workflows
Fertility Centers of Illinois selected airSlate SignNow for its responsive API and healthcare-oriented document workflows. The customer story identifies the organization’s satisfaction with the platform, but does not publish a specific accounting-request completion time or disclosure-volume result.
Property management
Martin Properties describes handling documents online and on mobile, a useful model for authorized staff managing requests away from a fixed office.
- Mobile document handling
Martin Properties reports processing and executing documents online, including mobile and offline work, with built-in security and compliance. That story supports flexible document handling, although it does not establish a healthcare disclosure-accounting outcome or authorize transferring its results to HIPAA workflows.
Troubleshooting this disclosure request
Resolve identity, privacy, retention, and plan questions before sending this request or its completed accounting to a recipient.
Business includes legally binding eSignatures, Audit Trails, templates, mobile apps, ISO 27001, SOC 2, and GDPR. HIPAA workflows require signNow’s HIPAA-compliant configuration and a required business associate agreement.
The account administrator should confirm that a business associate agreement is in place before processing protected health information. HIPAA compliance is stated as available with a BAA, not from the signature alone.
Business includes 100 signature invites per user per year, with overage fees. Business Premium adds bulk send, while Enterprise adds advanced signer authentication. Select the plan based on sending volume and identity requirements.
Use signNow’s Audit Trail to review signer identity, timestamps, IP information, and document activity. Export the trail with the completed request and retain it under HIPAA 45 CFR 164.530(j).
If the request contains PHI, verify the recipient before sending and use an approved HIPAA workflow. SMS OTP can add authentication, but it does not replace the organization’s access-control procedures.
A typed or drawn eSignature can support an electronic record when intent, consent, attribution, and retention are established. For U.S. transactions, ESIGN and UETA provide the legal framework; HIPAA privacy duties still apply.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.