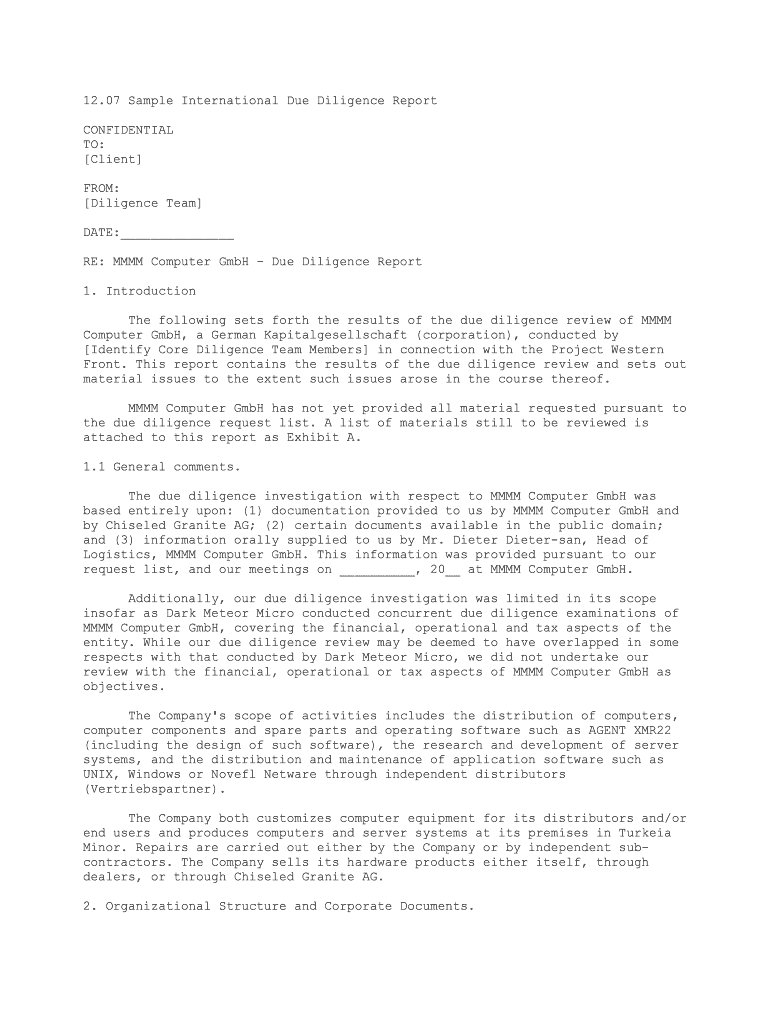
Due Diligence Request Checklist K&l Gates Form
Use a Sample Due Diligence Request Checklist K&L Gates template to make your document workflow more streamlined.
What this due diligence checklist does
The Due Diligence Request Checklist K&l Gates Form is a structured record for requesting, reviewing, and confirming diligence materials in a business transaction or internal review. It helps participants see which information has been requested, who must respond, and whether review is complete. In signNow, upload the checklist, allow the platform to detect fillable areas, add or adjust fields, send it to the responsible signers, and retain the completed document with its audit trail. The form’s specific legal effect depends on the transaction, recipient, and applicable state law.
Who uses this due diligence checklist
Legal teams
Legal and compliance teams use the checklist to organize requested diligence materials, assign review responsibility, and record completion status. It can accompany contracts, NDAs, HR forms, invoices, or consent forms when reviewers need a controlled record of what was requested and supplied.
Business teams
Finance, procurement, and operations teams use the checklist to coordinate counterparties, vendors, and internal approvers. A signNow workflow can collect signatures, preserve the completed checklist, and connect the record with supporting documents without changing the underlying diligence requirements.
Features for completing the checklist
signNow connects document preparation, signer routing, audit evidence, and storage around the Due Diligence Request Checklist K&l Gates Form.
Document control
Upload the exact checklist version and preserve its original layout while preparing the document for review and signature.
Field placement
Place fields for each responsible reviewer and signer without recreating the checklist in a separate system.
Signer routing
Route the checklist in a defined order so requested evidence and approvals reach the appropriate participant.
Audit trail
Capture signer identity, timestamps, and actions in an audit trail connected to the completed checklist.
Reusable template
Use templates for an approved checklist structure while keeping each diligence matter’s completed record separate.
Record storage
Store the signed checklist and completion evidence for later review, subject to the organization’s applicable retention policy.
Complete the checklist in signNow
Use this workflow to prepare, route, sign, and preserve the Due Diligence Request Checklist K&l Gates Form.
Upload checklist:
Upload the checklist PDF to signNow. Prepare fields:
Review detected fields and add missing ones. Assign participants:
Assign each field to the correct reviewer or signer. Send request:
Send the checklist through the selected signing order. Archive record:
Store the signed file with its audit trail.
How the audit trail records checklist activity
The audit trail documents who accessed, reviewed, and signed the Due Diligence Request Checklist K&l Gates Form and when each event occurred.
Authenticate signer:
Capture timestamps:
Hash document:
Seal record:
Link events:
Export evidence:
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.



signNow security and compliance
Data in transit:
Data at rest:
Security reporting:
Security controls:
Privacy framework:
Protected health data:
Teams that complete this checklist
A legal operations coordinator can upload the Due Diligence Request Checklist K&l Gates Form, place review and signature fields, route it to counterparties, and preserve the completion certificate with the transaction file. The workflow keeps the checklist’s requested evidence connected to signer and access records rather than email alone. A procurement or finance manager can use the checklist when onboarding a vendor or reviewing a transaction. signNow supports templates, mobile signing, and audit trails, allowing the manager to send the same approved checklist structure while retaining a separate record for each completed review and counterparty.
Choose a signing method for the checklist
- Upload the Due Diligence Request Checklist K&l Gates Form in the web app when preparing fields, recipients, and signing order from a desktop workflow.
- Use the mobile app when a reviewer or counterparty must inspect and sign the checklist away from the office, including supported mobile signing workflows.
- Use kiosk mode for supervised, in-person completion when a staff member controls the device and needs several people to sign sequentially.
- Create a shareable signing link when the same approved checklist must be distributed through a controlled channel rather than individual email invitations.
Privacy pitfalls in diligence workflows
Personal data copied into the checklist may be exposed when unrestricted recipients receive the completed diligence package. Missing consumer consent disclosures can weaken an electronic-record process when the checklist is used in a consumer-facing transaction. Broad folder permissions can allow people outside the review team to open signed diligence records. Unclear signer identity records can make it harder to connect a completed checklist with the responsible reviewer.
State rules and document exclusions
Notarization
Wills
Family law
Real-estate deeds
Recommended checklist workflow setup
Use a controlled signing configuration that preserves signer identity, document history, access protection, and the retention rule for the underlying diligence record.
| Setting | Recommendation |
|---|---|
| Authentication method | Email authentication with SMS verification |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Capture timestamps, IP, and action history |
| Document retention | Apply the underlying record rule |
| Encryption and provisioning | TLS 1.2/1.3, AES-256, managed users |
Retention periods for related records
Choose a retention period by the underlying record type and applicable rule; the checklist itself does not create a universal retention period.
Three years tax records
Six years substantial understatement
Six years HIPAA records
Three years payroll records
Five years injury records
Compare checklist signing plans
signNow pricing and plan features are shown first; competitor values are marked Not verified where the supplied vendor data does not confirm them.
| Features | signNow | DocuSign | Adobe Sign | PandaDoc | Dropbox Sign |
|---|---|---|---|---|---|
| Starting price | $8/user/month annually | Not verified | Not verified | Not verified | Not verified |
| Free trial | 7 days, no card | Not verified | Not verified | Not verified | Not verified |
| Bulk send | Business Premium included | Not verified | Not verified | Not verified | Not verified |
| Audit trail | Included in Business | Not verified | Not verified | Not verified | Not verified |
| HIPAA compliance | Available with BAA | Not verified | Not verified | Not verified | Not verified |
Key performance indicators that demonstrate SignNow's proven track record.
Troubleshoot checklist signing issues
These answers address signNow setup, delivery, compliance, and record-handling questions for the Due Diligence Request Checklist K&l Gates Form.
Business includes legally binding eSignatures, templates, and audit trails at $8/user/month with annual billing. Upload the checklist, confirm detected fields, assign recipients, and send it through the signing workflow. The plan includes 100 signature invites per user per year; additional invite charges may apply.
A 7-day free trial is available without a credit card. Use it to upload the Due Diligence Request Checklist K&l Gates Form, test field detection, and confirm the signing sequence before selecting a paid plan. Pricing is billed annually for the stated $8/user/month Business rate.
If a signer cannot open the checklist, verify the invitation address, resend the request, and check whether the message was filtered. A shareable signing link can provide another delivery route. Keep the recipient assignment unchanged so the audit trail identifies the intended signer.
Business Premium adds bulk send at $15/user/month with annual billing. It is relevant when the same approved diligence checklist must be sent repeatedly to separate counterparties. Bulk send does not replace reviewing each completed record or confirming each recipient’s identity.
signNow states that HIPAA compliance requires a business associate agreement. If the checklist contains protected health information, obtain the BAA and apply access controls before sending. HIPAA retention requirements come from 45 CFR 164.530(j), not from the signing platform.
For U.S. transactions, ESIGN and UETA recognize electronic signatures when intent, consent, attribution, and record retention requirements are satisfied. Consumer-facing electronic records may require the disclosure described in 15 U.S.C. §7001(c). Review state and transaction-specific exclusions before relying on the checklist.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.