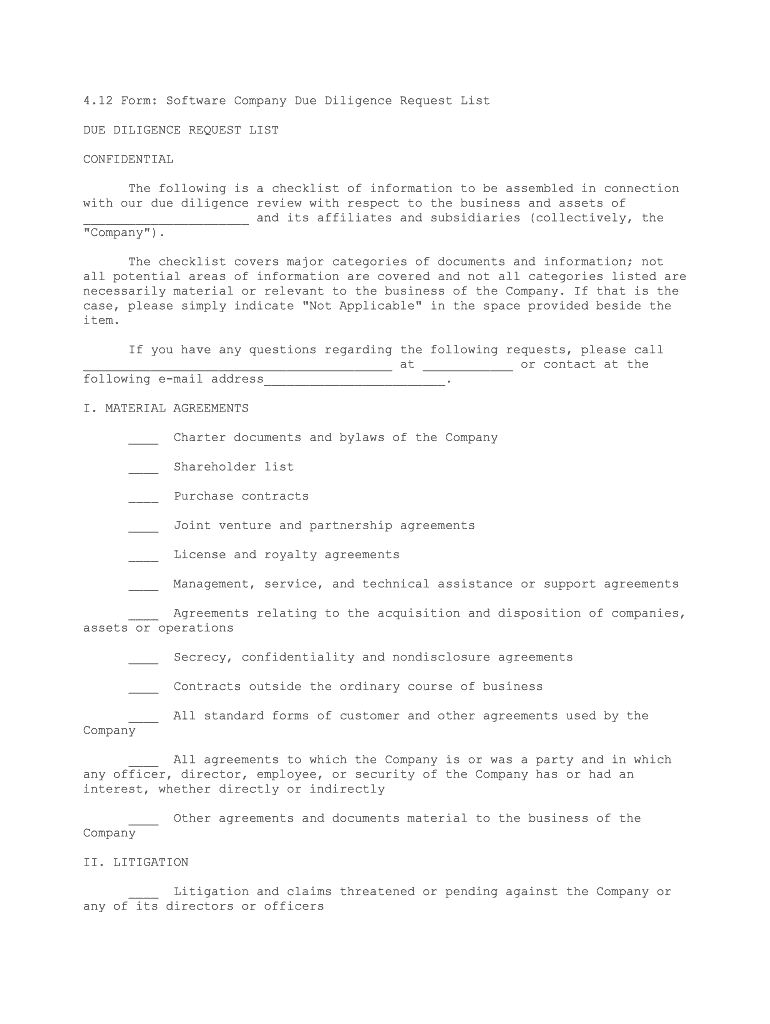
12 Form Software Company Due Diligence Request List
Use a 12 Form Software Company Due Diligence Request List template to make your document workflow more streamlined.
What this due diligence request list does
The 12 Form Software Company Due Diligence Request List is a structured business questionnaire for collecting information and supporting records from a software company during diligence. It can organize corporate, financial, legal, security, ownership, and operational review requests in one controlled file. With signNow, the sender uploads the list, reviews or adds fields, assigns recipients, sends it for electronic signature, and stores the completed document with an audit trail. No issuing agency, statutory filing deadline, or universal completion period is identified for this private business document.
Who uses this due diligence request list
Corporate development
Corporate development teams use the 12 Form Software Company Due Diligence Request List to collect organized responses, attachments, approvals, and signatures from acquisition targets during transaction review.
Review specialists
Legal, finance, security, and procurement reviewers use separate sections to request contracts, financial records, security evidence, ownership details, and signed certifications from a software company.
How the request list workflow works
The signNow workflow moves this due diligence request list from document preparation through assigned completion, electronic signature, and evidence-preserving storage.
Upload: Upload the company request list Review: Review detected and required fields Send: Send assigned sections to recipients Archive: Store signed records with evidence
What the audit trail records
The audit trail separates evidence of the 12 Form Software Company Due Diligence Request List signing event from the underlying business answers and attachments.
Authenticate signer:
Record timestamp:
Hash document:
Seal record:
Log actions:
Export evidence:
Recommended setup for diligence requests
Configure the request list around signer identity, evidence preservation, access control, encryption, and the retention rule applicable to the information collected.
| Setting | Recommendation |
|---|---|
| Authentication method | SMS verification for external signers |
| Signature type | Electronic signature under ESIGN and UETA |
| Audit trail | Retain timestamps and action history |
| Document retention | Six years for HIPAA-covered records |
| Encryption | TLS 1.2/1.3 and AES-256 protection |
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Key features for company due diligence
signNow organizes this 12 Form Software Company Due Diligence Request List from field preparation through signer assignment, audit evidence, and connected archival.
Field detection
Upload the existing 12 Form Software Company Due Diligence Request List, then review detected fields and correct any placement before distribution.
Role assignment
Assign sections to legal, finance, security, and company contacts so each person completes only the requested information.
Controlled sending
Send recipient-specific copies by email or signing link while preserving separate completion records for each counterparty.
Audit trail
Capture signer actions, timestamps, and document history to support an organized review file and later evidence requests.
Reusable templates
Reuse an approved request-list template for recurring acquisitions, vendor reviews, or investment diligence without rebuilding fields each time.
Business integrations
Connect completed lists with Salesforce, NetSuite, Google Drive, Box, or Microsoft 365 for downstream review and archival.



Security controls for due diligence records
Transit encryption:
Stored data encryption:
Security certification:
Management certification:
Healthcare protection:
Signature compliance:
Platform requirements for request-list signing
The 12 Form Software Company Due Diligence Request List can be prepared and signed through supported desktop browsers, with signNow mobile apps available for iOS and Android. Use an up-to-date browser and a secure connection when handling confidential company information.
Browsers Chrome, Firefox, Safari, and Edge Operating systems Windows, macOS, iOS, Android Mobile apps signNow mobile apps available
Enterprise deployments should confirm managed-device controls, API access, SSO provisioning, and certificate or long-term-validation requirements before rollout. Where the request list includes regulated information, align device access, signer authentication, storage, and retention with the applicable organizational policy and governing rule.
Best practices for due diligence requests
Use a controlled template, restrict sensitive disclosures, preserve audit evidence, and reconcile every completed request list against the transaction record.
Maintain one approved request-list template
Limit disclosure to necessary information
Archive the signed list and audit trail
Track every diligence response
Processing stages for diligence requests
No statutory processing period is identified for this business request list; timing depends on preparation, delivery, signer response, and archival controls.
Prepare the request list
Deliver to signers
Collect signer responses
Complete and archive
Retention periods for diligence records
Retention depends on the record class included with the request list. Apply the controlling federal rule only when that class of information is actually collected.
Six years for HIPAA records
Three years for tax records
Later of three or one year
Three years for payroll records
Five years for injury records
Privacy pitfalls in diligence requests
Uploading an outdated request-list version can omit newly required financial, security, ownership, or contract evidence from the diligence review. Sending the full list to every recipient can expose confidential technical, financial, or personal information beyond the reviewer’s assigned scope. Missing audit-trail exports can make it harder to connect a completed response with its signer, timestamp, and final document. Collecting consumer-facing records without the required electronic-record disclosure can create consent and access issues under 15 U.S.C. §7001(c).
Troubleshooting the due diligence request list
Resolve upload, distribution, authentication, retention, and electronic-signature questions before sending this company due diligence request list.
Upload the request list as a supported PDF or document file, then use signNow’s field-detection tools to review placements. If fields are not detected correctly, add signature, date, text, and checkbox fields manually before sending.
The Business plan includes templates and audit trails at $8 per user per month when billed annually. It also includes 100 signature invites per user annually; additional invite charges may apply, so review usage before sending large diligence batches.
Business Premium adds bulk send at $15 per user per month billed annually. Use it when the same due diligence request list must go to many counterparties with recipient-specific fields and separate completion records.
For confidential financial or technical information, enable stronger signer authentication such as two-factor authentication or SMS codes where available. Enterprise adds advanced signer authentication, while HIPAA workflows require a business associate agreement.
The signed request list can be retained with its audit trail, including timestamps and action history. Apply your organization’s retention policy; HIPAA-covered records require six years from creation or last effective date under 45 CFR 164.530(j).
Electronic signatures generally have legal effect under ESIGN and UETA when intent, consent, attribution, and record reproduction are established. The request list should not include excluded records such as wills, court orders, or family law decrees.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.